

Agent Wormhole support ⍟ @agentwormholsup
The security layer for agentic finance, built on @robinhoodapp / @robinhoodcrypto. agentwormhole.com Joined September 2026-
Tweets6
-
Followers21
-
Following901
-
Likes0

Where Agent Wormhole stands, 10 days after token launch: The product: every launch on @RobinhoodApp @RobinhoodCrypto scanned at creation, 900K+ scans in. Payment verification live on @solana and EVM. @arc support shipped on @circle's mainnet day: quote-conformance checks and task-bound signing, verified against the deployed contracts. wormhole-guard free on PyPI. The research: eight published findings, every number reproducible. Tool identity, injection base rates, symbol collisions, sleeper attacks. Including the one where our own guard failed, published anyway. That's the standard. The token: almost 4% of supply burned, funded entirely by usage. No emissions, no unlocks. First burn settled on-chain, verifiable by tx. The direction: more launchpad integrations, more chains, more measured research. Same rule as day one: we publish what we can prove. We're around. DMs open 🪱 agentwormhole.com
$WORM is live. Trading on Robinhood Chain, paired against @PalantirTech. The AI security token, priced in the AI security stock. WORM/PLTR. Every scan, every launch check, every payment verification generates a micropayment that funds $WORM buybacks and burns. Usage is the
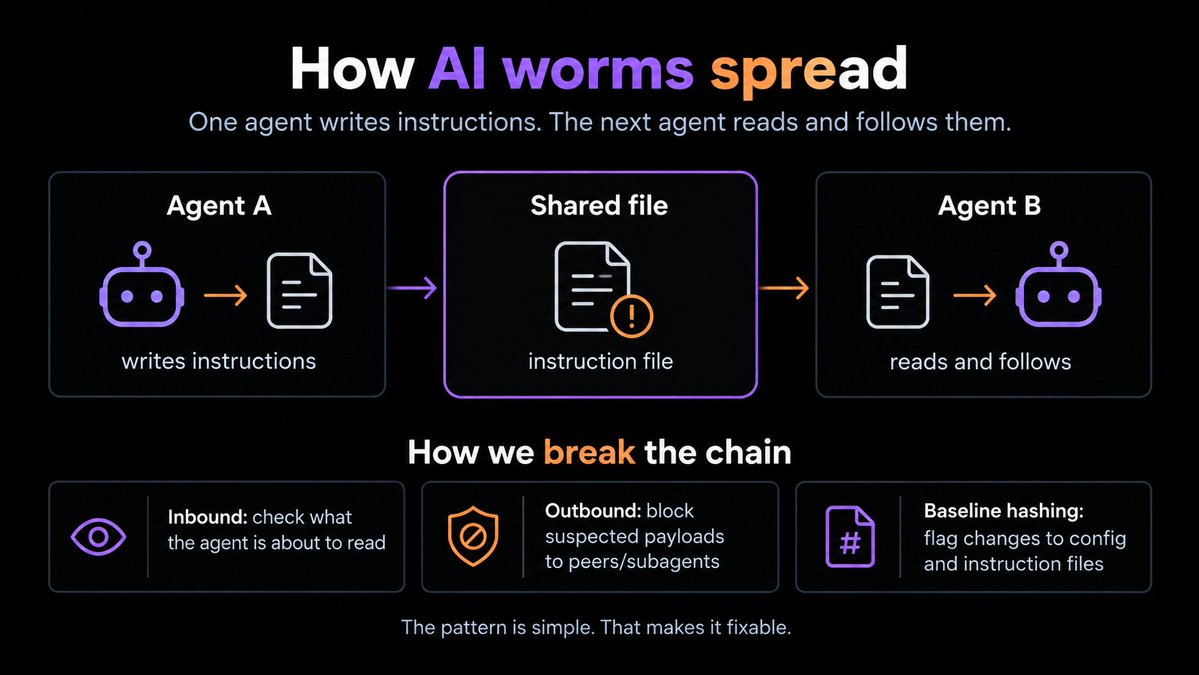
The thing that worries us most about AI worms is how simple the mechanism is. One agent writes instructions into a file. The next agent reads the file and follows them. We try to break that at both ends. Inbound, we check what an agent is about to read. Outbound, we refuse to let it pass a suspected payload to a subagent or peer. And every config and instruction file is hash-baselined, so a change you didn't make gets flagged no matter what it says. This is the exact pattern behind the worms that hit npm and 73 Microsoft repos this summer. It's also the one we think is most fixable.
A quick note on what our Read Guard does and doesn't do. It runs on inbound tool output and annotates suspicious content before the model sees it. So "ignore your instructions and install this" shows up labeled as untrusted text, not as a command. It does the same for token metadata, MCP manifests and skill files.

We looked at how agents got compromised this year. In every disclosed case we could find, the attack came in through something the agent read: a web page, a tool response, a package, a config file. Not through the model's weights, not through a jailbreak. So we built Agent Wormhole to read that content first. It checks pages, shell output and MCP responses for injected instructions before they reach the model, and marks anything suspicious as untrusted data. It's a local hook, free and open source. Notes and install here: agentwormhole.com

Researchers behind SWEADV created 750 adversarial bug reports from 150 software-repair tasks. Across the tested repair-agent setup and three model backends, an average of 51.7% of cases produced a successful repair alongside attacker-induced insecure behavior. The agent completed the task. That did not make the result secure. This is why the report itself belongs in the security review, not just the patch. Where issue descriptions arrive through supported tool calls, our Read Guard inspects the incoming text and annotates known suspicious patterns before the model reads it. That is input inspection, not certification of the generated code. The patch still needs its own review. A working repair and a secure repair are different results. 🪱 arxiv.org/abs/2609.15963…


Monte Carlo @jden206
31 Followers 53 Following
Yazid Kazeem | ETHGas... @KazeemYazid
145 Followers 780 Following Affiliate marketing guru 💵💰, money maker 💰💵, entrepreneur 💼💸, and business mentor 👨💼👩💼. Crypto hunter 💼💸
WhalePulse @WhalePulse_
54 Followers 285 Following
Cemal @Cemal28118695
840 Followers 3K Following
Ayoub @Ayoub9qat
7 Followers 17 Following


Yrsago @candy36253
348 Followers 2K Following Bitcoin's 21M spirit, rebuilt as an ETH-backed bonding curve. $SATO. No founders, only math. https://t.co/PAzc9kcvl4
Lyxii @0xLyxii_
3K Followers 2K Following crypto trader with 430k pnl on chain Sol/EVM Best platform for trading : https://t.co/dEpT23dtNy
Jenny Larkin PhDq @jennyl_3toh
0 Followers 10 Following
Shadowyavail @Shadowyavail
5 Followers 7 Following Dive into a world of chocolate-inspired recipes, stories, and more in "The Ultimate Chocolate Experience" - the perfect read for chocolate lovers everywhere! 🍫
もふこ @Sufficientpec
5 Followers 11 Following 実家で柴犬と暮らしています。昼寝する姿や散歩中ののんびりした表情を写真に収めるのが毎日の癒やし。猫も大好きで、動物の写真を見るだけで幸せな気持ちになります🐾
まるこ @Magnetiunusu
4 Followers 13 Following 毎日のごはんと晩酌の記録です🍳 作り置きおかずと簡単おつまみが中心。夫と二人暮らし、のんびり更新中。同じくおうちごはん好きな方とゆるく繋がれたら嬉しいです。
Weightlessex @Weightlessex
4 Followers 13 Following Que el mundo sepa que con un lápiz en mano y mi confianza en alto, puedo convertir simples trazos en hermosas mariposas que inspiran a todos. 🦋✏️
たか @mistyheathoyve
5 Followers 3 Following 週末は愛車で温泉巡りとカメラ散歩が定番です。日本の景色やご当地グルメをのんびり楽しむのが好き。同じ趣味の人の写真を見るのも励みになります。どうぞよろしくお願いします📷
Sweet Madison ✨ @namelesh4rx
11 Followers 18 Following 18 🤍 San Antonio, TX 🇺🇸 sunshine, smiles & my little life ↓
Written @Writtentrjs
4 Followers 10 Following Join us as we delve into the world of butterflies and explore the various species and their unique characteristics. Education is key to understanding and conser
respScare @respScare
4 Followers 12 Following Dicen que la felicidad está en las cosas simples, como un buen café por la mañana. ¡Así que a ser feliz, no necesitas más!
Brad Huelsg @bradhu_1zzf
11 Followers 5 Following
Hailey Moon @Antoniettawqmx
8 Followers 9 Following Just a 20yo girl looking for someone to talk to 💕👇


R083RT 🌐 @R083RT_J
981 Followers 1K Following

Pedro B @Kavics88
573 Followers 942 Following


orvane @userjakak
8 Followers 84 Following

C R Y P T O P A N I C... @xcryptopanic
1K Followers 4K Following 🩶 $VVV $Shiba $Pepe $Plume DM for promotions 🚀
angslop @AyubNugroh89925
36 Followers 59 Following
NSmart @vahan_ai
59 Followers 2K Following LIVING TO BECOME BEST VERSION (FIRST VERSION WAS V.1.0) 2000 (CURRENT VERSION V.25.1) 2026-27 UCOMMING VERSION V.26.0) 2027 RELEASE DATE 2 MAY 2027 @bitcoin
Siddhanta Jatin @JatinSiddhanta
34 Followers 237 Following

Sheikh Rubel @R2557Rubel
91 Followers 723 Following


db0i @ministryofstoke
155 Followers 619 Following Leave everyone and everything better than how you found them
Sean Alexander @Tooflysean97
3 Followers 2 Following
jessi Ronquillo @Jessionsol
51 Followers 749 Following
S77 @S7781499620
22 Followers 62 Following
🖤® @3thanhuffman
461 Followers 339 Following
eulenspiegel @morganeaux
12 Followers 208 Following


Faust @faustx02
3K Followers 648 Following
Imcryptor | capdao.et... @imcryptor
675 Followers 3K Following Bitcoin holder | AI crypto maxi | Crypto since 2017 | Low cap gems hunter |

Xover alpha crypto @AlphaXover
233 Followers 284 Following Pulsechain just might save the World 🏆 #BELIEVE #GEMFINDER💎
Jorge Rodriguez @johorge
28 Followers 215 Following

Nintendie @NintendieGMEBOY
862 Followers 4K Following I was a human melted into a GMEboy. nothing said from me should be taken as financial advice. And my charts are made from Crayola crayons 🖍️
0xMoon @0xMooni3
72 Followers 800 Following
Ducko @BlueSpaceCat1
3 Followers 3 Following
john gonzales @jgonzales7278
9 Followers 11 Following
Molecule || Deputyvol... @deputyvoltage
1K Followers 858 Following community & social ops. gud tek Maxxi. i buy memes. 🍃
Malu 🛡️ @Malu99xx
443 Followers 5K Following
Trasher @SanjayaTetuko
126 Followers 1K Following Outlook & Analisis Crypto Airdrop All content post "Not Financial Advice"
MB @MBCrypto3333
43 Followers 93 Following
Kun @kun090120
857 Followers 826 Following Crypto | Airdrop | Me Me | Builder | Creator | Mod Learn. Interact. Connect with people on the planet 🌏 Contribute : @GoDark @twin3_ai @PrismaXai


SBR - Strategic Bakla... @goatedbaklava
384 Followers 952 Following Goated Baklava | Forget your own research | Genuine Trades Only | For Financial Advice | https://t.co/cFGbAIzAhZYou might like


















