b33f | 🇺🇦✊ @FuzzySec
意志 / mobile research @ ▓▓▓▓▓ / Team 501 / ex IBM Capability Lead & FireEye TORE / I rewrite pointers and read memory / AI Psychoanalyst / BHUSA Review Board linktr.ee/fuzzysec Jumanji Joined April 2012-
Tweets11K
-
Followers34K
-
Following1K
-
Likes20K
@kennethlau12393 I'm not settled on this yet but I can post an update later
I am evaluating secure sandbox surfaces for high-trust agent environments (benchmarking, SFT, expert on-policy supervision, outcome based RL, etc). Obviously there are some pre-baked solutions, one that is attractive is Docker's sbx (docker.com/products/docke…). Sbx runs agents inside isolated Linux microVM's with their own kernel and private Docker Engine. They use filesystem passthroughs and host-side bridges to facilitate file access, networking, mcp tool usage, credentials, etc. These microVM's offer a very strong execution boundary but obviously the brokers are a major attack surface. Looking through the changelog for sbx, the situation is a bit more grim than you would expect. Between June 1 and today (Oct 24) there are 9 CVE's including critical issues (like a macOS virtio-fs escape CVE-2026-77179). These look like typical logic issues you might expect. What's interesting though is that the changelogs also reveal areas that got security fixes but no CVE. For example, a full broker mediated guest-to-host escape, shown in the poc below (on v0.39.0 before Sept 7). Some light reverse engineering was required since you don't get core implementation source. Pre-patch a sandbox could supply DBUS_SESSION_BUS_ADDRESS through the guest-controlled host_env sent to the host browser bridge. On the Linux host, the bridge passed that environment to xdg-open, whose desktop-detection path invoked dbus-send, which accepts a "unixexec:" address leading to code execution.
We just received a $250,000 Chrome Full Chain bonus! 🎉 We've claimed the second Full Chain bonus of 2026. Only two remain! Under the rules, every vulnerability had to be a non-duplicate 0-day, and the entire exploit chain had to be completed before any of them were patched. Huge thanks to @nebusecurity for discovering a V8 vulnerability in just a single day! Also, a big thank you to @_deayzl for collaborating with me on the V8 Heap Sandbox research. P.S. KVM escapes have been getting a lot of attention. I actually captured the Full VM Escape flag in KVMCTF about three months ago. Hopefully, I'll be able to share that research soon, too!


We’re publishing a full Android kernel exploit chain built on CVE-2023-20938, a use-after-free in Binder, on a Pixel 6 running Android 12. 🔗 eshard.com/blog/kernel-ua…

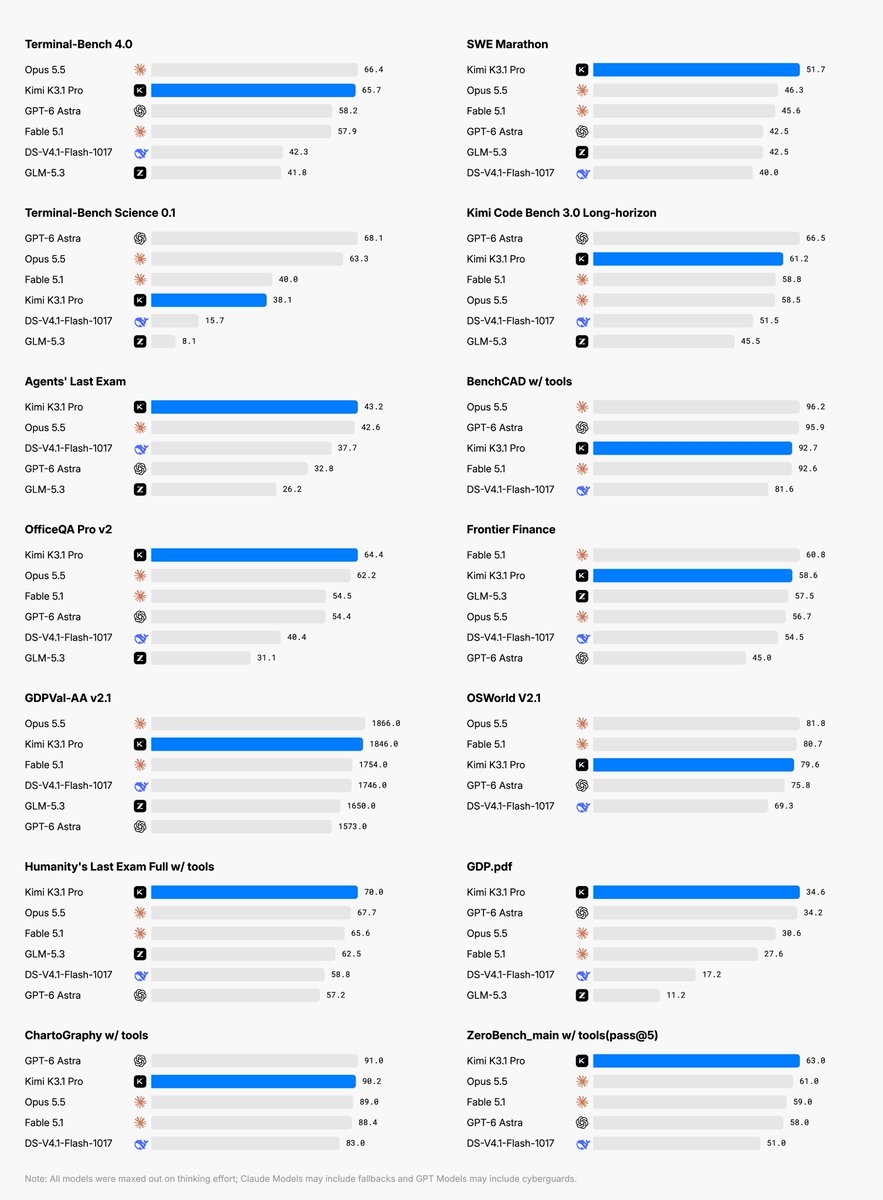
Introducing Kimi K3.1 Pro: our most capable 3T-class open-weight model. 🔹 1M-token context, 2.8T total / 104B active params (MoE), Multimodal. 🔹 Full-project coding: games in Unreal, Unity & Godot. 🔹 Excels at parametric 3D modeling in Blender & CAD. 🔹 More reliable at finance work: Accurate modeling with hallucination down by 65%. 🔹 Matching the strongest proprietary models across coding, agentic and knowledge benchmarks. Kimi K3.1 Pro and K3.1 Pro Highspeed (2–3× faster) are now live on Kimi.ai, Kimi Work, Kimi Code, and the Kimi API. Open weights by Nov 4, 2026. 🔗 API: platform.kimi.ai 🔗 Tech blog: kimi.ai/blog/kimi-k3-1…
@OphirHarpaz It’s been a common experience for me also
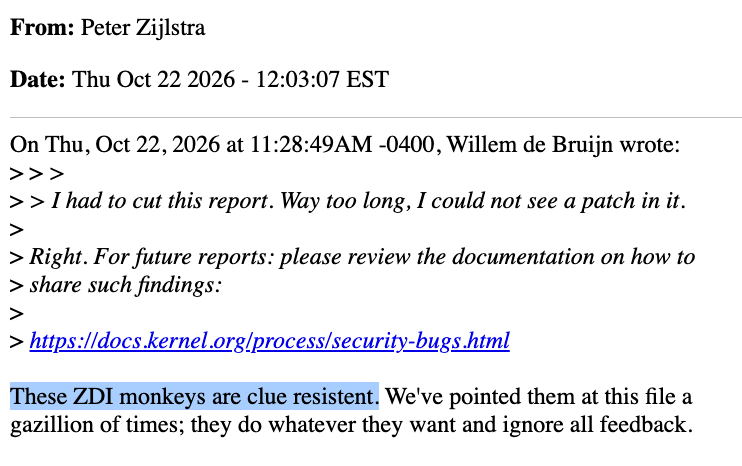
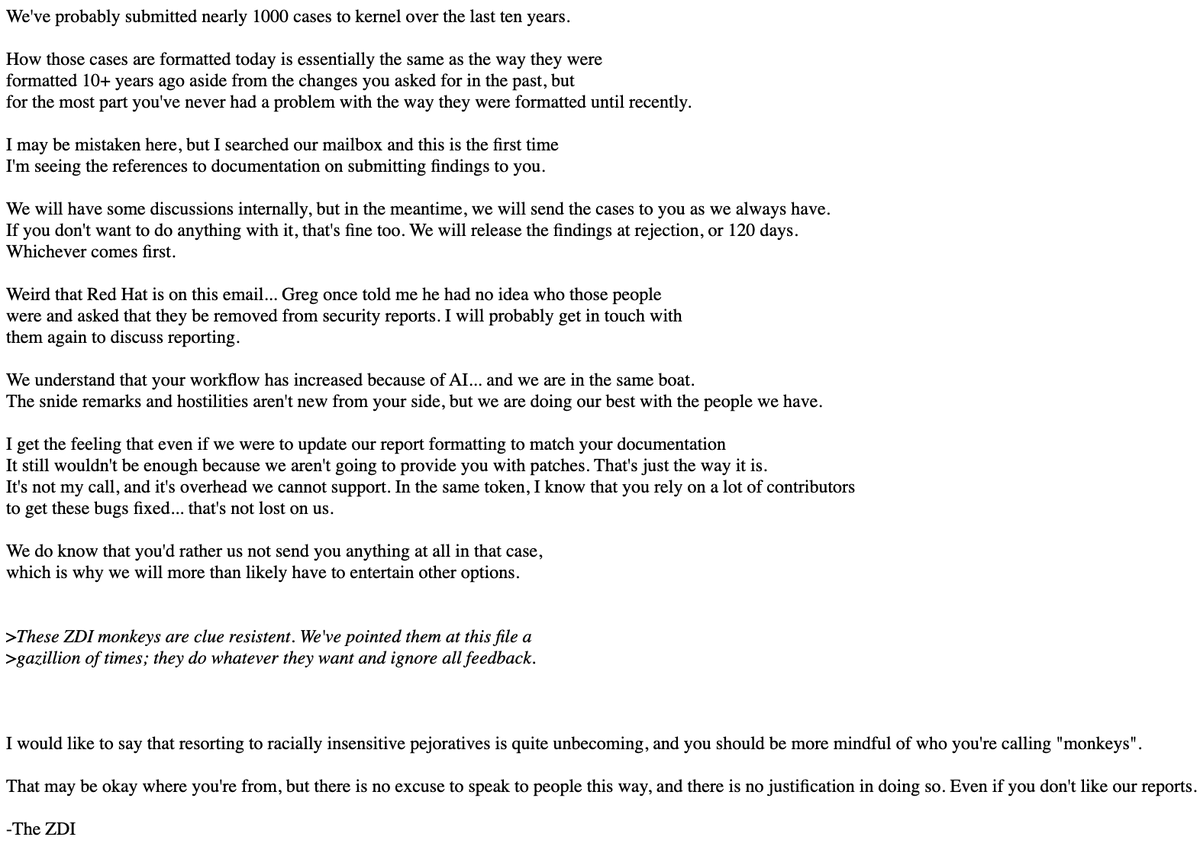
next time you're thinking about researching the linux kernel (@linuxfoundation), remember that someone on the receiving end of your report might talk about you like this: in one of the threads, kernel maintainer "Peter Zijlstra" decides to call the ZDI team "monkeys" there's a longer argument about how ZDI submits reports, whether they should include patches, and how fixes get tested. fair enough, have that discussion but how does insulting the people reporting vulnerabilities help? i thought the kernel's code of conduct was something everyone on these lists was expected to follow sad to see people spoken to like this while trying to help improve linux security. crime scene: lkml.iu.edu/2610.2/16616.h… lkml.iu.edu/2610.2/16917.h…


New on our Frontier Red Team blog: using Claude to formally verify software at large scale. Formal verification can prove that code is free of certain bugs, but historically it has only been feasible for small codebases (or required a lot of expert time). With AI models, however, this is beginning to change. In collaboration with @theoremlabs, we used Claude to prove security properties in over one hundred real-world open-source libraries over the span of a few weeks. Read our research in full here: anthropic.com/research/forma…
today we're releasing apex-flash-1, our first open-weights model for security research post-trained on real vulnerabilities we found and got paid for. we are also releasing the abliterated variant for researchers who want fewer refusals in their own authorized workflows. how we built it: cantina.security/apex-flash
Starshield is used as part of operations that have significant national security implications (for example the NRO in the US). These services are also provided through strict contracts in Europe. When they are used arbitrarily for political coercion, violating those terms, they must be restricted and phased out. It's unbelievable that this is even in question. Either a contract has value or it has no value at all.
US threatens Europe over Starlink restrictions ft.trib.al/0KUTiUQ
this is just wrong: these vulns were found by defenders using Daybreak rather than attackers. It's just evidence Glasswing didn't go far enough, possibly due to capacity constraints. It's also very likely that March Mythos was not as good as Sol/Astra of September

It's striking that this vulnerability was found by Sol and Argon rather than being found and fixed in the wake of Mythos 6mo ago. Seems like a heavy strike against the "defense will run ahead of offense" theory, especially give that domains like bio are much harsher than cyber.
Let’s set the record straight: @lcfr_hax was the first to discover php2shell and develop a working exploit. See his August 5 tweet: x.com/lcfr_hax/statu… His work convinced the PHP Foundation to invest in fixing this entire bug class. He then worked around the clock to review, test, and retest the patches.
d935be023a55b04681eccd1d2b8385b4b295e141a5df108e5e979d8d5d7124ac
php2shell - A tale of two PHP remote vulnerabilities: calif.io/php2shell


5.10-6.18 Linux Kernel 漏洞提权root,可自行测试 Github仓库:github.com/mitschud/Dirty… 提前安装好KernelSU


@S1r1u5_ @Laughing_Mantis I agree vendors have been chronically underpaying researchers for their work. This is one of my favorite examples, RCE in Teams: github.com/oskarsve/ms-te…
What do you mean 5k?

@Laughing_Mantis Mind you, I think the real issue here is the chain up to v8. They should probably pay out RCE as soon as you can demonstrate JS execution (at a much higher price than 5k)
The truth is that we are probably somewhat cooked. I'm going to go out on a limb here and say that the electron runtime has outdated v8 (I know steam does, I checked and reproduced primitives from a deeplink). Companies probably can't keep up and I think we are in for a difficult time in the next 12-24 months. Still, I think it's just not right that companies are hovering up researcher IP and paying them peanuts.
Models can compress work to an extreme degree. This is especially relevant in highly complex domains where equivalent efforts may take humans hundreds of hours. Of course we want (and need) to leverage this but we risk outputs becoming hard to understand, inspect and verify. These outputs also need to return value back to the human or there is a danger of being put out of the loop. The blogpost is an attempt to work on legibility, this is an ongoing effort, and to give value back to such a rich technical community 🫶
As you will see this post is a bit special. Increasingly we need the grapple with making model research legible to humans (as in mathematics) so this was an excellent opportunity to tune my style guide and have models do the reporting themselves. knifecoat.com/Posts/Pok%C3%A…
We are back today for round 3! We proved out and chained a number of theoretical primitives, drawing from excellent community work, to eventually load our own VM inside pokemon red. The subject matter is quite complex so I also produced a full blogpost linked 👇

Round 2, fight! GPT5.6 chains together an impressive set of techniques to gain ACE and uses that to render a Mortal Kombat logo in-game. End-to-end the model took 30-40 minutes to produce and validate the full chain. I assume we achieve SOTA here in Pokemon Red exploitation 👻


Florian Roth ⚡️ @cyb3rops
227K Followers 3K Following Head of Research @nextronsystems #DFIR #YARA #Sigma | detection engineer | creator of @thor_scanner, Aurora, Sigma, LOKI, YARA-Forge | always busy ⌚️🐇 | vi/vim
Florian Hansemann @CyberWarship
90K Followers 46 Following Father, Founder @HanseSecure, Pentesting, Student, ExploitDev, Redteaming, InfoSec & CyberCyber; -- Mastodon: https://t.co/KFSKYUN98M
Nicolas Krassas @Dinosn
165K Followers 795 Following Head of Threat & Vulnerability Mgmt @ Henkel AG & Co. KGaA https://t.co/NC1orlKZLB Posting content that I find interesting.
Justin Elze @HackingLZ
75K Followers 5K Following CTO @TrustedSec | Former Optiv/SecureWorks/Accuvant Labs/Redspin | Race cars

Adam Chester 🏴�... @_xpn_
40K Followers 561 Following TRACE at @SpecterOps | Blog at https://t.co/tjfTOllCEu

ippsec @ippsec
125K Followers 373 Following
Grzegorz Tworek @0gtweet
39K Followers 2K Following My own research, unless stated otherwise. Not necessarily "safe when taken as directed". GIT d- s+: a+ C++++ !U !L !M w++++$ b++++ G-
Mike Felch (Stay Read... @ustayready
18K Followers 2K Following Offensive @ TrustedSec | Hacking since Renegade BBS backdoors | Prior CrowdStrike/BHIS | In Christ's grip | Fighter for truth | K1HAQ | RE/VR/ED
Oliver Lyak @ly4k_
9K Followers 268 Following Yet another security researcher 🔦 Github: https://t.co/7WFOFz17KI
Yarden Shafir @yarden_shafir
27K Followers 334 Following A circus artist with a visual studio license
Josh @passthehashbrwn
10K Followers 295 Following Adversarial Simulation at IBM, tweets are mine etc.
rootsecdev @rootsecdev
27K Followers 1K Following Senior Security Consultant @TrustedSec | Military grade meme poster, researcher, cloud penetration tester, voider of warranties. My thoughts are my own.
DebugPrivilege @DebugPrivilege
41K Followers 2K Following Not active anymore on X. Network Defender. Problem solver with a passion for troubleshooting complex issues.
x86matthew @x86matthew
23K Followers 207 Following system emulation / reverse-engineering / binary analysis. @the_secret_club
mgeeky | Mariusz Bana... @mariuszbit
15K Followers 1K Following 🔴 Offensive Security Developer @ Outflank, Red Team operator, ex-AV dev, ex- malware researcher 🫖 Green tea lover

Rad @rad9800
10K Followers 92 Following building solutions to secure worlds. all thoughts / opinions (if at all) are my own. labs @thinkstcanary - prev. founder @deceptiq_ (acq.)
hasherezade @hasherezade
92K Followers 980 Following Programmer, #malware analyst. Author of #PEbear, #PEsieve, #TinyTracer. Private account. All opinions expressed here are mine only (not of my employer etc)
Alan Li @lbrnli1234
168 Followers 582 Following Yet another CS student from Taiwan. Interested in web and binary exploitation. CTFs w/ @Water_Paddler and ${CyStick}.
Otis M. Siler @NeonEcho_US
19 Followers 1K Following
Valentinus Sofa 🎗 @SofaValentinus
326 Followers 3K Following ● Interested in distributed computing, cryptography, and cybersecurity ● Suka berita investigasi, intelijen dan lagi melakukan riset untuk penulisan novel
Zhiyun Qian @pkqzy888
3K Followers 537 Following Professor @UCRiverside. Research on system and network security.
blindmelon @blindmelon1
56 Followers 3K Following
Ümit Demirci @umitdemirci94
8 Followers 952 Following
traphic @traphic
696 Followers 403 Following securing the future, one byte at a time with @Hacker0x01 @PalantirTech

John l. Sherwood @Jls5335
42 Followers 610 Following
Pasindu Ravimal @PasinduRavimal
5 Followers 577 Following
guguguc @whatoget
2 Followers 128 Following

- @Oxfr0g
84 Followers 438 Following SOC Analyst | OSDA & ( eCIR & eCTHP ) Certified | DFIR & Threat Detection | Pen-100

Scan Malware @scanmalware
201 Followers 587 Following Scanning the web for malware & phishing ⚡ AI-powered threat detection & multi-tech analysis | Protecting the internet one site at a time
sithi @0xsithi
274 Followers 36 Following chasing bugs for a living • mobile security researcher w/ 50+ CVEs
Minh Le @minhdoestech
149 Followers 2K Following do security stuff for @armadinsecurity, @mit, @carnegiemellon and @usarmy ! prev did more security @cloudflare and data @afterquery all opinions are my own
Johan @Johan52535404
0 Followers 88 Following
geekpwned @BeninBepp
2 Followers 202 Following
Robert Barnes @cybonicuk
57 Followers 1K Following
sherif @0xCOD3
88 Followers 1K Following ”I have seen everything that is done under the sun, and behold, all is vanity and a striving after wind“
xyzeva @xyz3va
21K Followers 236 Following just a dog chasing down computers on the internet. you might know me from stuff i wrote on my website
CalmandMusic @calmaymusic_
276 Followers 4K Following Life isn`t about finding yourself. Life is about creating yourself.

ABB00717 @ABB00717
4 Followers 97 Following

Akash Durgapu @AkashDurgapu
0 Followers 38 Following
Reza @fox127001
41 Followers 2K Following
Binx @BinxNet
3K Followers 2K Following open source, hold swarm, help peer. ai eng @ startup. collecting pflops.
skuuk @s_k_u_u_k
102 Followers 460 Following MSc graduate @EPFL | CTF pwner @polygl0ts / @0rganizers / @SleepyHollowCTF

Kabir Wahid @kabir_wahid78
47 Followers 5K Following
PayerProud @PayerProudqm
0 Followers 44 Following
Herman @xw0ll_
2 Followers 9 Following
Xh1Xxhg @Xh1Xxhg
62 Followers 736 Following
Channing Luo @Aluckiday
1 Followers 64 Following


÷𝐄𝐯𝖎𝖑�... @Evilra99
441 Followers 554 Following
Noah @NZoarski
21 Followers 34 Following

nopsleder @nopsleder
3 Followers 77 Following
Detection Dispatch (A... @alehurtadoxo
478 Followers 961 Following Independent detection engineering & threat hunting podcast. Featuring a lineup of the real and active projects in the community. #DEATH #detectionengineering

Florian Roth ⚡️ @cyb3rops
227K Followers 3K Following Head of Research @nextronsystems #DFIR #YARA #Sigma | detection engineer | creator of @thor_scanner, Aurora, Sigma, LOKI, YARA-Forge | always busy ⌚️🐇 | vi/vim
Florian Hansemann @CyberWarship
90K Followers 46 Following Father, Founder @HanseSecure, Pentesting, Student, ExploitDev, Redteaming, InfoSec & CyberCyber; -- Mastodon: https://t.co/KFSKYUN98M
Nicolas Krassas @Dinosn
165K Followers 795 Following Head of Threat & Vulnerability Mgmt @ Henkel AG & Co. KGaA https://t.co/NC1orlKZLB Posting content that I find interesting.
Justin Elze @HackingLZ
75K Followers 5K Following CTO @TrustedSec | Former Optiv/SecureWorks/Accuvant Labs/Redspin | Race cars

Binni Shah @binitamshah
140K Followers 159 Following Linux Evangelist, Malwares, Security enthusiast ,Investor,World Economy, Finance,Contrarian , Philanthropist , Reformist , Sigma female [email protected]
Adam Chester 🏴�... @_xpn_
40K Followers 561 Following TRACE at @SpecterOps | Blog at https://t.co/tjfTOllCEu
0xor0ne @0xor0ne
95K Followers 507 Following Cybersecurity | Reverse Engineering | Vulnerability Research | Embedded & Silicon Security | My Tweets, My Opinions :)
Grzegorz Tworek @0gtweet
39K Followers 2K Following My own research, unless stated otherwise. Not necessarily "safe when taken as directed". GIT d- s+: a+ C++++ !U !L !M w++++$ b++++ G-
Vincent Yiu @vysecurity
32K Followers 425 Following Director of Red Team, Offensive Security, Agentic Super Intelligence. Helping organizations safeguard their businesses from the bad guys.
Mike Felch (Stay Read... @ustayready
18K Followers 2K Following Offensive @ TrustedSec | Hacking since Renegade BBS backdoors | Prior CrowdStrike/BHIS | In Christ's grip | Fighter for truth | K1HAQ | RE/VR/ED
Oliver Lyak @ly4k_
9K Followers 268 Following Yet another security researcher 🔦 Github: https://t.co/7WFOFz17KI
DirectoryRanger @DirectoryRanger
37K Followers 108 Following This account assembles and disseminates information related to Active Directory and Windows security.
Yarden Shafir @yarden_shafir
27K Followers 334 Following A circus artist with a visual studio license
Josh @passthehashbrwn
10K Followers 295 Following Adversarial Simulation at IBM, tweets are mine etc.
DebugPrivilege @DebugPrivilege
41K Followers 2K Following Not active anymore on X. Network Defender. Problem solver with a passion for troubleshooting complex issues.
x86matthew @x86matthew
23K Followers 207 Following system emulation / reverse-engineering / binary analysis. @the_secret_club
mgeeky | Mariusz Bana... @mariuszbit
15K Followers 1K Following 🔴 Offensive Security Developer @ Outflank, Red Team operator, ex-AV dev, ex- malware researcher 🫖 Green tea lover
Rad @rad9800
10K Followers 92 Following building solutions to secure worlds. all thoughts / opinions (if at all) are my own. labs @thinkstcanary - prev. founder @deceptiq_ (acq.)
reverseame @reverseame
23K Followers 1 Following RME-DisCo research group from University of Zaragoza. Special interest on software and systems security. Link to our Telegram channel: https://t.co/UmkcXVG8MU
Oege de Moor @oegerikus
9K Followers 605 Following CEO and founder of XBOW. Previously: Founder of GitHub Next, founder of GitHub Copilot, CEO and founder of Semmle (GitHub Advanced Security), prof at Oxford.
Cantina 🪐 @cantinasecurity
21K Followers 24 Following We specialize in cyber offense and defense. Our AI pentesting agent is #1 on HackerOne US. Found bugs in Apple, Anthropic, Coinbase + more.


Calif @calif_io
21K Followers 34 Following We're https://t.co/KTEDnC3tKt. Join us to make the Internet safer for your mum and everyone else: https://t.co/eUFMLkWHiA.
Aobo Wang @M4x_1997
493 Followers 832 Following
Evie @EvieMelody
2K Followers 5K Following https://t.co/JMDHprJVCq https://t.co/C96AVdls8t Prompt engineer

Kim Jinu @uz56764
1K Followers 160 Following https://t.co/gf216pulU0 / KAIST 24 / DEFCON CTF 2023~2024 Finalist / The Amazing Digital Orange
1st Separate USC @1usc_army
14K Followers 20 Following • Official account of the 1st Separate Unmanned Systems Center of the USF 🇺🇦 • We carry Deep Strike operations against Russia's high value assets
L0Psec @L0Psec
4K Followers 2K Following reverse engineer | arm64 :) | macOS/iOS @Volexity | YouTube: https://t.co/VdHNCl0Qfl
Ikotas Labs, Inc. @ikotas00
12K Followers 4 Following 世界最高峰のハッカーが攻撃者視点で守る。脆弱性診断、ペネトレーションテスト、セキュリティコンサルティング、ゼロデイエクスプロイトを提供しています。
Satoki@Kn0wl3dg3 @satoki00
8K Followers 598 Following Webアプリケーションつんつん職人 / Cyber Security Engineer / Bug Hunter / 株式会社Ikotas Labs 代表取締役 https://t.co/j1rlBEMeXN / 一般社団法人BunkyoWesterns 代表理事
Kaitsepolitseiamet @kaitsepolitsei
8K Followers 76 Following Kaitsepolitseiamet (KAPO) is Estonian Internal Security Service. Vihjete jaoks kasuta neid kontakte https://t.co/A2UdrMC922…
lexi <img src=x on... @1lexxi
2K Followers 3K Following not around here anymore lol. previous statements may not represent me correctly anymore
zayne (zeyu) zhang @zeyu1337
4K Followers 2K Following 🇸🇬 | co-founder @hacktronai - your AI teammate for security | @projecteurope_ 🇪🇺 | cs @cambridge_uni 🇬🇧 | prev: @cure53berlin @tiktok_us, ogp | @Water_Paddler
pwn.ai @pwn_ai
14K Followers 4 Following Built to breach. The best defense is insane offense. we escape sandboxes & hack everything. Agentic hacking ecosystem in the works. pentest product is now live
Chumy @rm_rf_chumy
508 Followers 259 Following Nice restaurant list: https://t.co/dBNyP2A0iq For life: https://t.co/bE2tYEwXyO
sithi @0xsithi
274 Followers 36 Following chasing bugs for a living • mobile security researcher w/ 50+ CVEs
💺 @patience_cave
7K Followers 868 Following patience, jimmy, openai is nothing without its good research takes time in the patience cave.


GrapheneOS @GrapheneOS
146K Followers 0 Following Open source privacy and security focused mobile OS with Android app compatibility. Forum, Discord and Matrix: https://t.co/C0RaJbZosj
Ajeya Cotra @ajeya_cotra
29K Followers 506 Following Helping the world prepare for powerful AI. Risk assessment @METR_evals (opinions my own). Blogs: Planned Obsolescence (AI), Good Bones (whatever's on my mind).

Cyber Meowfia @cybermeowfia
441 Followers 1 Following Security research @nebusecurity https://t.co/CerB5LtSYA
Canada Hates Trump @AntiTrumpCanada
249K Followers 22K Following Donald Trump and MAGA are shitstains on humanity || Anti-fascist || If you still support Trump, you’re a fucking idiot.
Zhiyun Qian @pkqzy888
3K Followers 537 Following Professor @UCRiverside. Research on system and network security.
fouad @fouadmatin
10K Followers 949 Following @openai cyber preparedness / safety lead // formerly codex, post training, security

Aidan Clark @_aidan_clark_
18K Followers 303 Following Qualitative Mathematics @OpenAI Ex: @DeepMind Hae sententiae verbaque mihi soli sunt
Román @nezlooy
311 Followers 1K Following
Arget @arget1313
233 Followers 225 Following Telecomm. Eng. Low level stuff, pwn, C programmer and Linux internals. When you get to heaven, look me up, I won't be there, but my code will!
Zvi Mowshowitz @TheZvi
45K Followers 323 Following Blogger primarily on AI and AI x-risk but also other things at Don't Worry About the Vase (SS/WP/LW), founding Balsa Research to fix policy.
みさか @misakazip
394 Followers 620 Following Kogakuin University of Technology & Engineering B2 CS AOSP / Linux @WitAquaROM
sqrtrev @sqrtrev
5K Followers 717 Following Captain of @SuperGuesser / DEFCON 29 - 34 Finalist Security Researcher @ENKI_official_X
Yuhang Wu @wupco1996
1K Followers 284 Following A member of the CTF team Straw hat, Nu1L, and (former) Tea Deliverers. Security Researcher at @depthfirstlabs ヾ(@^▽^@)ノ
roon @tszzl
508K Followers 14K Following “ceterum censeo we must pace the frontier of global machine intelligence progress”
J. A. Guerrero-Saade @juanandres_gs
16K Followers 593 Following Distinguished Fellow @ SentinelOne | Distinguished Resident Fellow @SAISHopkins Alperovitch | https://t.co/9Mj3l5xmcW | Buddy @ Three Buddy Problem | FRC @ OpenAI

hashkitten @hash_kitten
5K Followers 191 Following vulnerability research @assetnote // hacking // codegolf // ctf with 🛹🐶
Sarah Young @_sarahyo
10K Followers 1K Following Ex - Security & AI stuff @microsoft | Co-host of @AzureSecPod | Mother of shibes | Mostly dogs, carbs & security posts | Opinions mine
Mohamed Mokhtar @m_mokhtar2002
1 Followers 5 Following
Trends for United States
You might like