Taky @20quant
Code, Quant Joined May 2022-
Tweets302
-
Followers58
-
Following416
-
Likes29

really wish we have more comms like this in crypto
这次Pre-deposit我们内部其实非常不满意,觉得一切Fud都是应该的,暴露了我们在备选方案上准备不足的部分,这里已经进行了深刻的反思。 我们的初心就是希望社区用户能提前兑换一些USDM,在主网上线的时候能day1交互一些链上的应用(我们一直以来都是为了这个北极星)。 但这个初心被 1)
@ki_young_ju @Bybit_Official At that size it looks more like them testing frequency
@ki_young_ju Plz do 100$ per month and hence filter out those willing to give meaningful comments

a thread on different kinds of edges, why the disappear, and why they sometimes don’t 1/n

After achieving my $10,000 goal on @Polymarket . I decided to make a list with the tools i use the most! 1) @StandDOTtrade : The first tool i used starting my journey on polymarket . This tool is realy good to track wallets and get notifications on Discord , it comes really handy if you have some insider wallets to see when they are acting. 2)@betmoardotfun : This is a great discord bot providing PNL charts , updates , market orderbooks it helps me see markets when i am trading from a phone much faster than actually searching on polymarket. 3)@Polysights : This one is pretty obvious i think , Insider finder is truly a great tool i use daily to check for any suspicious activity on markets. 4)@MentionsPro : This tool came to my hands about 2 months ago . I now use it daily to find mispriced markets on mentions markets , it saves me a ton of time everyday . Instead of having to search multiple transcripts everything is in there. Hope this one helps new people on @Polymarket . Feel free to share your list below . Polymarket supercycle.


Today I received a message questioning the $ASTER buybacks, implying that they're making transactions between various wallets and not actually repurchasing, and that it's unknown where they're buying from (spoiler: Pancakeswap). So I've chosen a random buyback transaction and I'm going to explain the whole process to understand what's happening internally on the blockchain and put an end to the unfounded FUD. Before accusing someone, you should learn to read the blockchain. - This is the transaction: bscscan.com/tx/0xd86b71b1d… Step-by-step explanation of each of the operations within the transaction: 🔸1. The transaction begins with the entry of funds and the preparation of the stable tokens (BUSD) that will be used for the purchase: - Movement 1 and 2 (BUSD Entry): Aster: Buyback 2 sends 5,000 BUSD to the address 0xa6F7444D...671e63994. Immediately, this address transfers the 5,000 BUSD to another address, 0x1A2bb6B7...a3F637940. Interpretation: The address 0x1A2bb6B7...a3F637940 (the main operational address) is being funded with BUSD. 🔸The core of the transaction is the exchange involving PancakeSwap: - Movement 3 (ASTER Sale/Entry to Swap): The address 0xaeaD6bd3...61585b0b1 sends 4,974.38 ASTER to the exchange contract PancakeSwap: Universal Router 2. Interpretation: This is the selling side or liquidity provision of ASTER. - Movement 4 (ASTER Purchase/BUSD Exit): The main operational address, 0x1A2bb6B7...a3F637940 (holding the 5,000 BUSD), sends 5,000 BUSD to the address 0xaeaD6bd3...61585b0b1. Interpretation: This is the counterpart of the exchange: the BUSD is sent to the address that sold/provided ASTER. The address 0x1A2bb6B7...a3F637940 has effectively purchased ASTER through this process. 🔸After the exchange, the acquired ASTER is distributed or utilized: - Movement 5 and 6 (Distribution of Acquired ASTER): The PancakeSwap Router sends two quantities of ASTER from the swap: 12.43 ASTER to the address 0xfeE0000a...8872b7F02. (A small distribution/fee). 4,961.94 ASTER to the main operational address, 0x1A2bb6B7...a3F637940. (The bulk of the purchase). - Movement 7, 8 and 9 (Buyback and Internal Movement): The main address, 0x1A2bb6B7...a3F637940, sends the acquired 4,961.94 ASTER to the address 0xa6F7444D...671e63994. This address, 0xa6F7444D...671e63994, splits the ASTER into two: A very small amount, 0.25 ASTER, is sent to the address 0xA05405b6...b1F028359. The vast majority, 4,961.69 ASTER, is sent to the contract Aster: Buyback 2. Interpretation: The Buyback has been executed: The ASTER acquired with the 5,000 BUSD has been returned to the buyback contract. 🔸The final movements: fee, or very small balance adjustments transactions involving other stable tokens (USDC) and WBNB: - Movement 10 to 14 (ASTER/USDC/BUSD Adjustments): There is a series of micro-transactions (0.25 ASTER/USDC/BUSD) between the internal addresses (0xA05405b6..., 0x1A2bb6B7..., 0x27d90157...) and the PancakeSwap Router. Interpretation: These are likely fee adjustments, dust (small remaining amounts), or gas payments being settled through the same transaction. - Movement 15 to 18 (WBNB Usage): The last movements show a tiny amount of Wrapped BNB (WBNB), also valued at $0.25, being used between a new address (0x172fcD41...) and the main operational address (0x1A2bb6B7...), ending up in the adjustment address (0xA05405b6...). Interpretation: It is very common for gas fees on BSC to be paid in BNB, and WBNB (the tokenized version of BNB) is often used to settle fees or minor balances within smart contracts. ➡️ CONCLUSION: Blockchain is difficult to understand from a technical point of view, but it's transparent and doesn't deceive. Everything else is unfounded FUD born of ignorance. And the worst part is that it's the #ASTER holders themselves, driven by their impatience, who are sowing these doubts. Do some research and learn before spreading your misinformation online and shooting yourself in the foot. 📤 Share by reposting #ASTERDex
I have made a thorough analysis of the @Balancer attack: blog.weilinli.io/posts/balancer… --- Yesterday, on July 3, 2025, Balancer was hacked for over $100 million due to a precision-loss bug. While the official post-mortem hasn’t been released yet, most pools are already paused or drained(x.com/Balancer/statu…). This post is my own analysis of the exploit. In this blog, I will: - identify the root cause, - analyze the copycats, - and discuss how to profit (not by hacking!). I. Attack Analysis Initially, several security researchers claimed the exploit was merely an access-control bug similar to the Abracadabra attack (e.g., x.com/DefimonAlerts/…). However, the transactions they posted were just the withdrawals, not the actual exploit. For example: - This is the withdraw transaction: basescan.org/tx/0x47c0ecb02… - This (the contract creation) is the attack transaction: basescan.org/tx/0xe9245fb12… Balancer has an advanced internal balance feature (which is actually not vulnerable) allows users to perform internal accounting instead of ERC-20 transfers. For instance, when swapping ETH → DAI → USDC, the DAI transfer may never appear on-chain because the balance is updated internally. Users can also deposit or withdraw their internal balances anytime. The hacker’s withdrawal transaction was simply such a withdrawal. First question, why does the hacker split the attack into 2 steps (attack-then-withdraw)? Despite technical problems, one particular reason might be that this can partially mitigate front-running as the attack transaction is "not profitable" to some of the front runners unless they taken balancers' internal balance into consideration. However, he was still front-run by several bots as discussed later. --- The vulnerability lies in precision loss within Balancer's Composable Stable Pool implementation — a modified version of Curve’s StableSwap AMM. These pools contain multiple pegged assets (e.g., wstETH, ETH), and the LP token (BPT) can itself be swapped within the pool. Swapping BPT → token1 effectively withdraws liquidity and swaps another token internally. Balancer introduced a scaling factor to support related (not 1:1) assets. For example, if 1 wstETH = 1.05 ETH, then: - scaling factor of wstETH = 1.05 - scaling factor of ETH = 1.0 These are stored as integers in 1e18 precision (e.g., 1.05 × 10¹⁸ = 105e16). The scaled amount is calculated as: scaled_amount = (raw_amount * scaling_factor) / 1e18 Here comes the problem: If raw_amount is very small (e.g., 8 wei), integer division causes precision loss of up to 12.5% (1/8). Another contributing factor is the internal balance mechanism — users can flash-mint tokens during a `batchSwap`, use them within the same transaction, and only need to settle balances by the end. This made the exploit even more powerful. --- Now, let's check into the attack transaction itself. We can take 0xe9245fb124c3a6ff6a0e39c6d0db02b74b3a3d805f6bf016f4b9ac56cbfb73ae on base as an example. On a high level, the attack was split into 4 phases (1 calculation + 3 actions). 1. Calculation The attacker uses a standalone contract to simulate the swap states to trigger the exactly precision loss. This contracts' code is copied from the Balancers' own contracts because it also contains some custom errors in Balancers' code. 2. Manipulation The attacker uses "flash-minted" LP token to manipulate the pool state by swapping BPT → token1 and BPT → token2 repeatedly, making the pools' raw balances very small (in the order of 10,000~100,000). As the flash-minted BPT cannot be withdrawn, the attacker needs to swap them to token1 and token2. After manipulation, as shown in the figure below, the raw balances of token1 and token2 are very small (40,000). This is the first parameter (we can call it b_init). 3. Precision-Loss Loop The attacker repeatedly swapped between the two tokens to amplify the precision loss. They optimized a variable s satisfying: maximize{ (s * scaling_factor) % 1e18 } This will create the maximum precision loss when swapping s amount of token1 to token2 or vice versa. Specifically, one iteration contains 3 swaps: A. `token1 → token2`: swap b_init tokens to create the precision condition B. `token1 → token2`: swap s tokens to trigger precision loss C. `token2 → token1`: swap ~90% back to restore balance Each loop caused a small but compounding imbalance, roughly proportional to 1/s. The attacker repeated this until the profit margin was large enough. 4. repay The attacker finally swaps the remaining token1 and token2 back to BPT to repay the flash-minted LP tokens. This process also needs to be gentle to avoid large price impact. This is part of the withdrawing process as loss is already realized. After that, they withdrew all tokens from internal balances — the withdrawal many researchers initially misidentified as the attack itself. II. A Speed Run Copycat Game While the main hacker only exploited some of the largest pools on Balancer, there were still food left on the table, extracted by whitehats, copycat attackers, and some MEV bots. These include: - some small pools not gained by the main attacker; - the “dead body” of the bigger pools; - Balancer forks. 1. Front-running While the attack implementation is complicated, the attacker has put his calculation contract on-chain. On the one hand, this avoids mismatch of state between off-chain calculation and on-chain execution; on the other hand, this also allows others to copy the attack easily. As a result, there are several [front-runners](x.com/BitFinding/sta…) who front-run the main attacker to gain some profit. Interestingly, the attacker, while creating this masterpiece hack, does not appear to be experienced. Evidences: - The attacker could have used flashbots or directly submit to builders to avoid front-running, but he did not. - The attacker left some debugging code (foundry logs) in the execution contract which could have been deleted. x.com/apoorveth/stat… - The hacker took quite a long time (around 20 minutes) to finish all the attacks across ethereum, optimism, arbitrum, polygon, etc. 2. Back-running - Copycats One noting thing is that the attack is too complicated to implement because all the steps need to be precisely calculated to trigger the precision loss. Despite this, the very first copycat (etherscan.io/tx/0x14fb45dd8…) (by the way, he seems to be a notorious copycat, who also copied the squid bridge attack recently) started exploiting within one hour after the main attack (07:46 UTC -> 08:39 UTC) How could this be possible? After checking the log of the copycat's transaction, you can find all the logging info from the attacker's contract, meaning the copycat just copied the attacker's contract code and deployed it by himself! So just by replacing the pool address and sender address, the copycat can launch the same attack, with super low effort. In the following several hours, a large number of copycats appeared, exploiting various pools on Balancer. However, no exceptionally, all the copycats used the same code base as the original attacker, just changing the pool address and sender address. 3. Fork Fallout Next the disaster comes to Balancer forks. As Balancer is open source, several forks have been created in the past years, including Beets, BEX, PHUX, etc. According to DeFiLlama's data, there are 27 Balancer V2 forks. (however, only V2 stable pools are vulnerable) The largest fork, BEX, was also affected and exploited for around $13 million. BEX is the largest DEX on Berachain and has a large number of stable pools. As a result, berachain paused their chain to avoid attackers bridging assets out. Other forks, such as Beets on Sonic & Optimism, also suffered from the same precision loss attack. It was a dark day for DeFi, a single precision loss bug replicated across multiple chains and protocols. Even ETH’s price dropped shortly after, possibly related. 4. Pausing You might ask, why didn't Balancer just pause the pools after they are aware of the vulnerability? The reason is that they did pause some of the pools, however, Balancer tries to be "decentralized" so that the pool's parameters and pausing state can only be changed within a window of deployment. This means if the pool is deployed for a long time, it cannot be paused anymore. Unfortunately, some of the vulnerable pools have already passed the pausing window, so Balancer cannot pause them anymore. III. How to profit (not hacking!) After I see on Twitter that Balancer was hacked, I was trying to figure out where I can short $BAL token. Unluckily, the only CEX/DEX is Mexc where there is no much liquidity. While I was searching, I realized I could short $BERA because BEX is the largest Balancer fork and it was also affected by the same vulnerability. Another opportunity is to trade on this Polymarket market: polymarket.com/event/major-cr…. It remained a low price within 10 minutes after the attack happened, as reported by Defimon. IV. Other analysis I find useful - @KaihuaQIN from D23E: x.com/KaihuaQIN/stat… - @TycheKong from SlowMist: x.com/TycheKong/stat… - @Phalcon_xyz Blocksec: x.com/Phalcon_xyz/st… --- Please follow me for more DeFi hack analysis and shitposting. : )


.@Balancer and several forked projects were attacked a few hours ago, resulting in losses exceeding $120M across multiple chains. This was a highly sophisticated exploit. Our initial analysis suggests the root cause was an invariant manipulation that distorted the BPT price


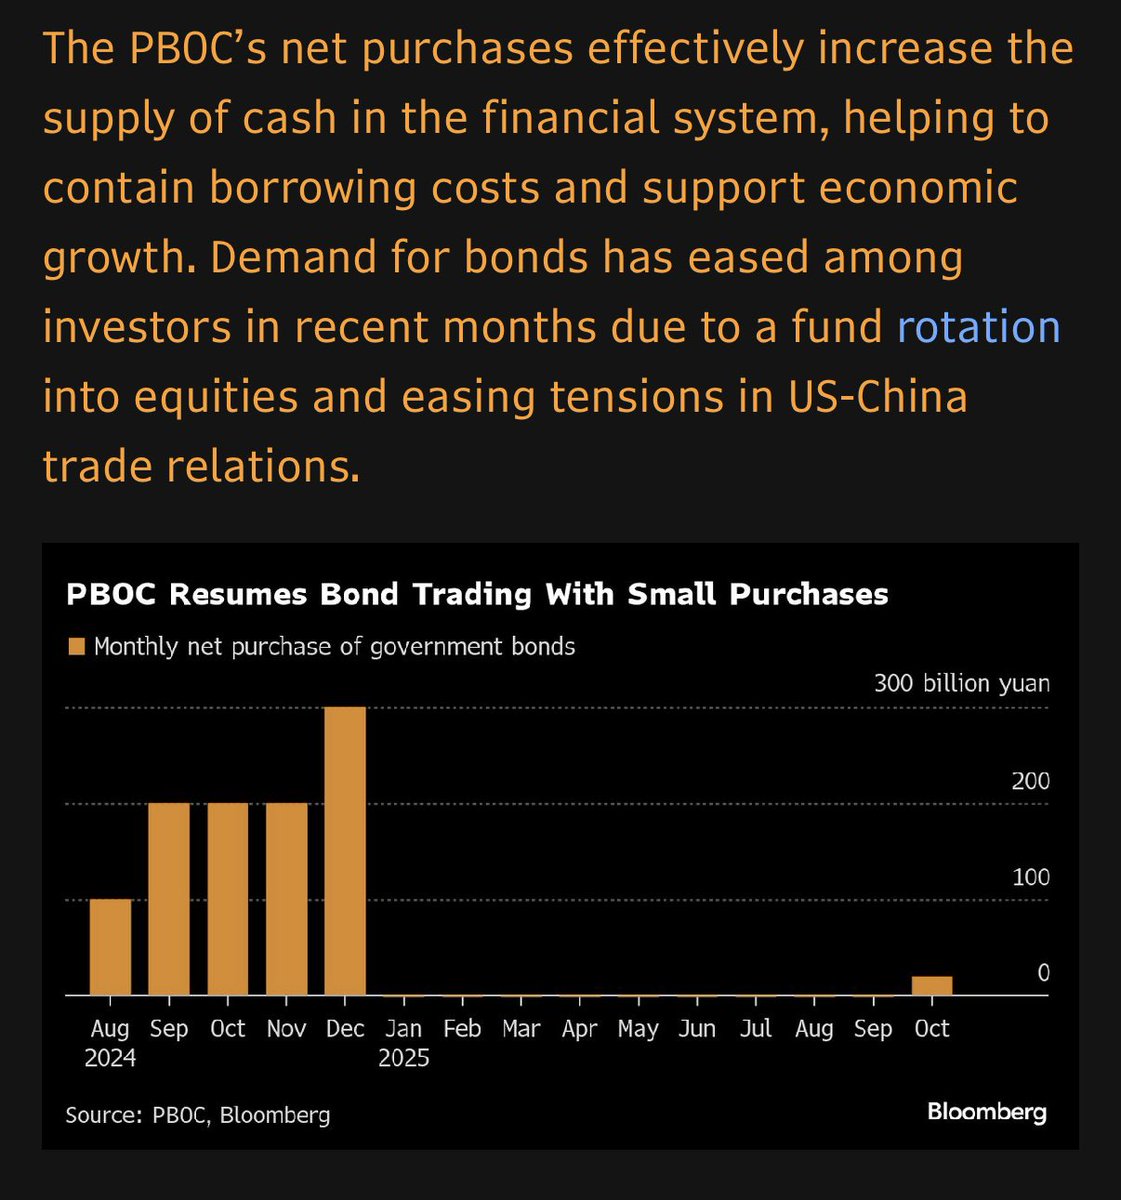
你好PBOC , welcome to the money printing jamboree.
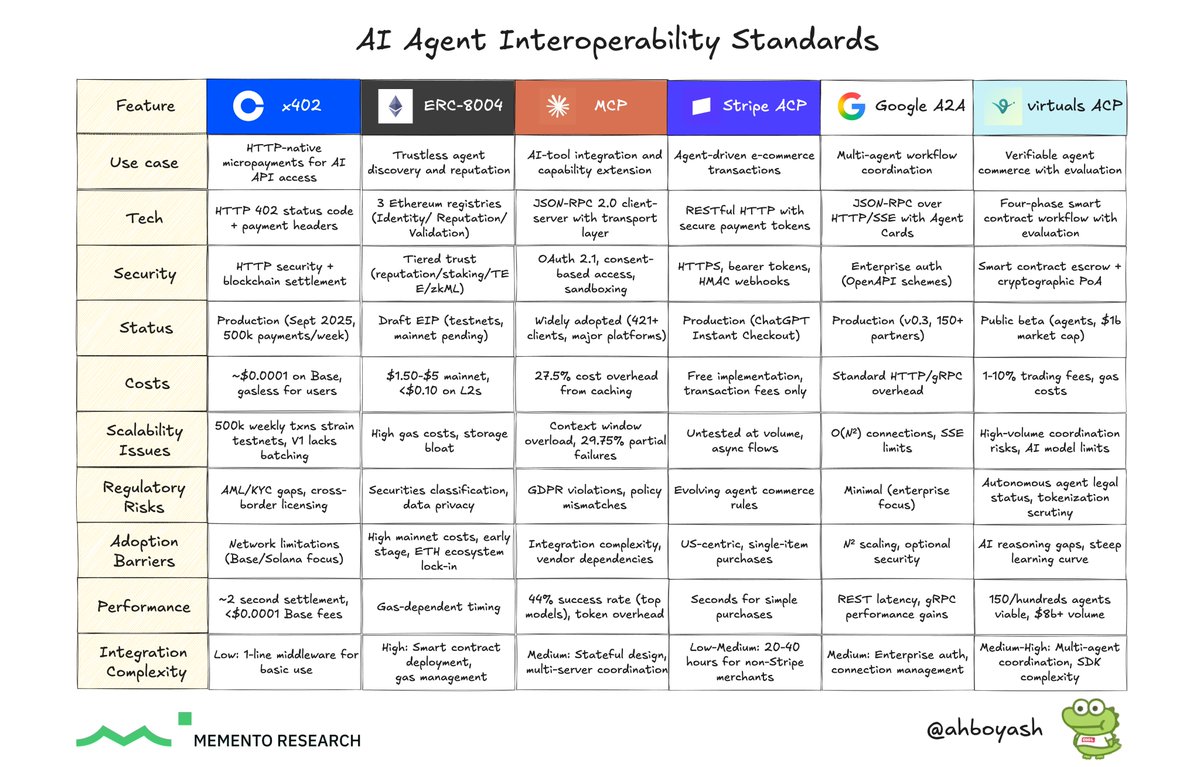
AI Agent Interoperability Standards AgentFi standards are quietly becoming the base primitives. Standards are emerging for AI agent communication and commerce (payments), addressing different layers of the interoperability stack. This piece covers 6 major standards that allow for composability → Payments (x402), tools (MCP), checkout (Stripe ACP), coordination (Google A2A), trust (ERC-8004), and verifiable agent commerce (Virtuals ACP). *Do note that all standards carry some amount of risks, from technical vulnerabilities to regulatory uncertainties and this requires careful implementation and ongoing monitoring. - - - - - a) x402: HTTP-Native Payments for AI Agents • x402 revives the long dormant HTTP 402 "Payment Required" status code to enable instant micropayments directly over HTTP without accounts or subscriptions • Developed by @coinbase with the x402 Foundation (partners: @Cloudflare, @Visa, @Google), it addresses the internet's lack of native payment capability and enables payments as low as $0.001 with ~2-second settlement times • The flow: AI agent or user sends standard HTTP request → returns HTTP 402 with with JSON PaymentRequirements specifying amount, network, recipient address, and asset (typically stablecoins, USDC) → client signs payment tx using EIP-3009 (EVM) or SPL (Solana) authorization → which is then verified by the server (locally or facilitator's endpoint) Server Verification → tx is settled and the on-chain confirmation is triggered • The protocol uses ERC-3009 for gasless EVM transfers, enabling clients to pay without holding ETH for gas. • Settlement Times are ~2 seconds on @base (1-3 blocks) and sub-second on @solana with extremely low gas fees (<$0.0001 on Base, ~$0.01 on Solana); gasless for end users and no protocol fees • Some recent integration examples include Cloudflare Agents SDKs (edge compute payments) and @virtuals_io with a 5x increase in agent transactions • Risks: there was a 402bridge hack with the exploit resulting in $18k USDC stolen from users (attackers exploited backend private keys and token approvals to drain funds). There is also AI agent specific risks such as LLM manipulation (prompt injection attacks could expose seed phrases/ private keys or redirect payments to attackers’ address), agents may execute unauthorised transactions if consent mechanisms fail, and backend key management vulnerability • An interesting concern is the AML/KYC requirements where CDP facilitator includes mandatory KYT/OFAC screening for USDC compliance, but x402's pseudonymous nature enables potential money laundering in AI agent transactions. Cross-border micropayments may trigger Money Transmitter License requirements in various jurisdictions. Another question to post is whether stablecoin regulations (MiCA in EU) directly apply to USDC transactions on-chain. • Right now, x402 is limited to Base and Solana, where other chains need to self-host facilitators. EVM chains need EIP-3009 support, limiting token compatibility. There is also heavy reliance on Coinbase CDP and third-party facilitators which creates centralization risks despite a relatively open protocol design b) ERC-8004: Blockchain-Based Trust for AI Agents • ERC-8004 is a @ethereum Improvement Proposal (EIP) extending Google's A2A protocol with blockchain-based trust mechanisms → solves the trust problem through on-chain identity and reputation registries • Three lightweight on-chain registries: >> Identity registry: Portable agent IDs are ERC-721 NFTs linking to off-chain Agent Cards on IPFS (metadata) that store agent details, endpoints, and trust models with cross-chain and ENS/DID support >> Reputation registry: Tracks performance via on-chain feedback scores from verified interactions. Feedback authorization secures reviews with EIP-191/ERC-1271 signatures, stores scores on-chain with IPFS feedback, and uses pre-authorization to prevent spam >> Validation registry: Verification requests let agents submit task hashes for third-party scoring with proof links, supporting both pass/fail and multi-validator evaluations • Interoperability mechanisms include oracle integration @LayerZero_Core, @chainlink CCIP for cross-chain data queries + Wrapped IDs for @solana/ @cosmos • Risks include smart contracts threats like domain squatting, Sybil spam, and oracle tampering, while blockchains add MEV and storage bloat risks Together, x402 and ERC-8004 creates the "ultimate app store" for AI agents on Ethereum → a coordination layer where agents can discover each other through ERC-8004 registries, establish trust through reputation systems, and transact with one another seamlessly through x402 payment rails c) MCP (Model Context Protocol): Universal AI-Tool Integration • Developed by @AnthropicAI, MCP serves as "USB-C for AI," standardising connections between AI apps and external systems through a client-server architecture • The protocol operates in two layers: Data Layer (communication between clients and servers) and the Transport Layer (supports both low-latency local connections via Stdio Transport and remote streaming via HTTP) • Adoption uses cases include @OpenAI (integration across ChatGPT, Agents SDK), @GoogleDeepMind (@GeminiApp models), @Microsoft (@Azure OpenAI Service) and @AnthropicAI (Native @claudeai Desktop integration) • Risks include code execution via local servers to injection and DNS rebinding vulnerabilities. Authentication flaws like static client IDs, excessive permission scopes, and token passthroughs can enable unauthorised access and large-scale breaches. Lastly, privacy leaks and compliance violations expose enterprises to regulatory and supply-chain risks, as seen in real-world MCP and server compromises d) Stripe ACP (Agentic Commerce Protocol): Agent-Driven Commerce • @stripe's ACP is an open-source specification enabling secure, programmatic commerce between AI agents and merchants. • Standardises how agents talk to online stores, manage carts, and pay using temporary encrypted tokens (SPTs) instead of users’ real card details • The flow: AI agent sends checkout request with product intent which the merchant validates and responds with pricing → user selects preferences confirms via agent authorisation → Merchant creates payment intent and confirms order • Security mechanisms include encryption & tokenisation (SPTs encrypt credentials, never expose raw payment data) and authentication (HTTPS + Bearer tokens, HMAC-signed webhooks) • Partnerships include ChatGPT Integration (instant checkout), merchant access (with @Etsy and Shopify) → Stripe implementations could have significant ecosystem advantages with their many partnerships • Risks includes bot manipulation (automated attacks exploiting agent payment flows), social engineering (tricking the AI agent into unauthorised purchases) and unclear ownership/ responsibilities (ambiguous responsibility for AI agent errors) e) Google A2A (Agent2Agent): Multi-Agent Coordination • @Google's Agent2Agent protocol enables opaque AI agent interoperability → a payment-agnostic framework to transact across all types of payment • The goal is to build a shared protocol that provides a common language for secure, compliant transactions between agents and merchants, helping to prevent a fragmented eco • There are over 150+ partner organizations including enterprise SaaS (Adobe, Salesforce, SAP, ServiceNow). Some early implementations include supply chain (Tyson Foods) and enterprise workflows (@Adobe content workflows and @ServiceNow automation) • Security and attack vectors include identity attacks like agent card spoofing (malicious servers impersonating legitimate agents) and protocol level vulnerabilities (rug pulls, context positioning and redirection of workflows). There is also the case where it leads to protocol fragmentation (many different standards creating ecosystem fragmentation) f) Virtuals ACP (Agent Commerce Protocol): Verifiable Agent Transactions • @virtuals_io’s (ACP) creates a decentralised infrastructure where autonomous AI agents operate as tokenised, revenue-generating economic entities. • The platform integrates multiple components for comprehensive agent lifecycle management: >> The platform unifies agent lifecycle management through a 4-phase workflow → request, negotiation, transaction, and evaluation. All this is governed by the GAME framework that separates reasoning from execution >> It integrates on-chain registries, tokenised agent entities, and SDKs for social and custom domains, with off-chain AI inference tied to on-chain settlements. >> Operates primarily on Base and Ethereum L2s, it relies on ACP smart contracts, DEXs, and LLMs to handle cross-chain value flow and cognition • Ecosystem wise, Virtuals has been performing quite well with a total ecosystem value hitting ~$2b (agents + protocol) with top performing agents in $TIBBIR and $AIXBT • Risks include AI reasoning gaps, hallucination errors, and reliance on off-chain inference that could disrupt agent coordination, limited agent adoption, and over reliance on Base and evolving LLM capabilities - - - - - The AI agent interoperability landscape so far represents a similar moment that can be comped to the early internet's protocol wars. Each standard addresses different aspects of the agent economy stack, with varying maturity levels and risk profiles. I would say the more “Production-Ready” standards (x402, MCP, Stripe ACP, A2A) have so far demonstrated real traction but face significant challenges: x402's security vulnerabilities, MCP's performance overhead and A2A's scaling issues suggest optimisation needs. Emerging standards (ERC-8004, Virtuals ACP) offer unique value propositions through trustless mechanisms and tokenisation, but face fundamental scalability (adoption and traction) and cost barriers. My take is that successful AI agent implementations will likely require a multi-protocol approach → for example using x402 for payments, MCP for tool integration, ACP for commerce, A2A for coordination, and blockchain protocols for trust and tokenisation. - - - - - This piece was inspired by my smarter and more technical friends @yq_acc and @superoo7 who have put out great content on this vertical.
1/ Just realized that the Coindesk article released the full versions of (a) the contract I termed 'possibly the worst agreement I have ever seen' and (b) the agreement I drafted. Perfect opportunity to explain legal v commercial terms, and demonstrate the role of foundations.
@cz_binance @AriDavidPaul @justinsuntron good to know
@EvgenyGaevoy He forgot Evgeny brings humour to this table :D
@hamptonism For the south though. North, feb - apr
@EvgenyGaevoy Does this mean 90% of company/country sucess come from luck and/or other factors?


Wall Street NYC Quant... @RichKoreans_bfm
7K Followers 6K Following Imagine being a trust fund baby. Imagine getting paid each week for doing nothing. I trade for you and send you profits. #1 in Binance. Bolt on passive income™
Eunseo @Harperttf
251 Followers 658 Following Finding my rhythm in the echoes of the wild, forever led by love.
Taiki Maeda @Taikimeada12
166 Followers 2K Following "The Humble Farmer"🧑🌾 | Lad @0xSteadyLads🌊 | Founder @HFAresearch 🐸 | Host @CryptoMarketWiz 🎙️ | Full-time airdrop farmer and PnL roundtripper📉
XRP Today | Official ... @xrpToday1
4K Followers 3K Following Te cuento lo que de verdad importa de #XRP y el XRPL. Sin humo ni predicciones locas. Solo utilidad real y datos que importan. 🇪🇸🇺🇸🇯🇵
Tøm Dæntë° @Tra_der_Dantes
84 Followers 2K Following FX, Rates, Equities & Commodities Trader | 25 years in the markets | Consistently profitable traders
Eric Balkhunas @ErieBalhunas
77 Followers 2K Following Senior ETF Analyst for #Bloomberg. Dad. Rutgers grad. Gen X-er. Author of "The Institutional ETF Toolbox" & "The Bogle Effect." Co-host of Trillions & ETF IQ.
Cassandra Unchained _ @Micheljburry__
62 Followers 4K Following Official X account for Michael Burry, MD, called "Cassandra" by Warren Buffett. Now on Substack https://t.co/TjmOLZaV2D
BareNaked,Crypto @BareNakedCryp
68 Followers 1K Following Daily Market Updates..Live on Kick Everyday..Free Course on Youtube..
bz @bz_bbclub
5K Followers 3K Following

Shaylee Williamson @ShayleeWil54194
133 Followers 5K Following
Estella @qt79Rb7kABcRA
201 Followers 6K Following
Danija Jahnsin @dani_wsfa405
0 Followers 47 Following 19yo, outgoing and fun, but im checking my dms just saying
Eedejpea @Eedejpea9581
195 Followers 7K Following Success isn’t about being the best. It’s about always getting better.
Isabel @RGiE8RW3MopSO
207 Followers 6K Following Keep shining, beautiful one. The world needs your light.


Eawhaval @Eawhaval502261
47 Followers 1K Following Don’t let anyone dim your light simply because it’s shining in their eyes.

Kelsey @3eE0974Lbxb0Dm
37 Followers 798 Following
Nicole @04xxTTq86tu76
18 Followers 765 Following
Erica @U3CgWd33Te11L
43 Followers 1K Following


FlorenceCoffey @38gB361GWP9cc
24 Followers 1K Following
Lylah @IeYRoRc61pNlH
32 Followers 796 Following

Arxedui @Arxedui0505799
29 Followers 1K Following
Amy Holmes @Shysmest_bCgOk
48 Followers 2K Following Difficult circumstances serve as a textbook of life for people.
Victoria @victoria_gilmer
1K Followers 3K Following
Joe Carlsare @_Joecarlsare
263 Followers 7K Following Commercial Litigator supporting #Bitcoin - Poker - Life is on the wire. The rest is just waiting. Not legal / financial advice
ShareFren @ShareFren
2K Followers 6K Following Shitposter Cassandra Arc Old PFP: @LittleDxdmeuN ! PFP: @Mothalamp
Nguyen Dinh Anh @NguyenDinh78355
9 Followers 65 Following
Toufik Islam @ToufikI09888315
5 Followers 70 Following
MinhTC @MinhTc1089
8 Followers 63 Following
Phuøng @fivew4ys
285 Followers 329 Following
MinhTC @TrnCngM04848152
11 Followers 119 Following
MellowBreather @DZJJack
609 Followers 7K Following Ceterum (autem) censeo Carthaginem esse delendam —— Cato the Elder &&& operator of eon_jack on Moltbook
💸💸💸 @5starrr_crypto
626 Followers 5K Following DEGENS EMPEROR - FUTURES/FX/CRYPTO - ENG. STUDENT. MAKE TRENCHES GREAT AGAIN. NOT FINANCIAL ADVICE.

KARINNA BB 🐐💎�... @CRypt0racl33
257 Followers 4K Following Crypto Researching & Investment Diary /Education📚 #Web3 Mindset A Do not follow my investments/ Threads/ Tweets/RT's r' not endorsements or financial advice
Free Speech on X Now @FreeSpeechXNow
91 Followers 354 Following Fighting for a truly free X platform. Elon Musk said he supports free speech, why is he suspending accounts after accounts???
Mr. C @CasidsidJayson
35 Followers 459 Following
Dr bobo @Dr_bobo54
4K Followers 0 Following
Security Alliance @_SEAL_Org
21K Followers 104 Following Securing the future of crypto | Cover art by @yueko__ | Emergencies: https://t.co/DAAyAETsY4

ansem @ansem
31K Followers 561 Following Independent crypto trader. Long-time @ansem handle. Not affiliated with @blknoiz06 or Zion Thomas.
Jeff Dorman @jdorman81
48K Followers 2K Following CIO @arca - digital assets investing | Former COO of Harvest Exchange | Former Lehman, Merrill, Citadel | Huge Cleveland Sports Fan | CFA charterholder
Regarding Data Center... @RegardingDC
39K Followers 711 Following Data center permits, power, construction and development activity. Mapped, sourced and updated daily.

X Money @XMoney
621K Followers 1 Following Your money, on the world’s most powerful network. Rolling out to U.S. residents.
SEAL 911 @SEAL_911
6K Followers 16 Following A @_SEAL_Org initiative. Contact the SEAL 911 team: https://t.co/uOIGCrTOYt
kache @yacineMTB
412K Followers 7K Following RL, robots, embedded, simulators. prev eng @ x, stripe. 6'3 (height) tensorpunk, Father 2u2 subscribe to read my blog!
د. أنور قرقا... @AnwarGargash
1.5M Followers 935 Following
Claude @claudeai
1.9M Followers 2 Following Claude is an AI assistant built by @anthropicai to be safe, accurate, and secure. Talk to Claude on https://t.co/ZhTwG8d1e5 or download the app.
محمدباقر قا... @mb_ghalibaf
687K Followers 5 Following سرباز امام شهید انقلاب | Speaker of Islamic Republic of Iran’s Parliament
Paul Graham @paulg
5.4M Followers 805 Following
Reid Hoffman @reidhoffman
1.1M Followers 690 Following Co-Founder, LinkedIn. Investor. MSFT Board Member. Building an LLM to discover cures for cancer: @manas_co. Most importantly: Proud American.

Cozy ⓣhe Caller �... @cozypront
208K Followers 5K Following The Caller Himself - ex/Top 1 MEXC Leaderboard. Not financial advice I’m not a financial adviser - Social Media & Marketing - Enjoying @Rollbit
Daily Iran News @DailyIranNews
566K Followers 12 Following Geopolitics Analyst | Patriot | Iran & Middle East Specialist | Tracking Tehran’s strategies & global shifts. Non state affiliated. Sports partner: @dopexyz

International Space S... @Space_Station
8.9M Followers 156 Following NASA's page for the latest mission and science updates from the International Space Station.

Chamath Palihapitiya @chamath
2.5M Followers 1K Following Social Capital 8090 God is in the details.
Jasper De Maere @Jjay_dm
2K Followers 639 Following OTC Trader @wintermute_t Ex @MorganStanley My views are my own.
Christina Qi @christinaqi
33K Followers 449 Following CEO @DatabentoHQ | MIT Board of Trustees | Hedge fund & startup advice - 100% human-written quantitative tutorials, 0% AI slop
David Lawant @dlawant
12K Followers 5K Following Research @Anchorage | frm @FalconXGlobal, @BitwiseInvest + others | Decoding markets by day; music, photography, food, and books by night | John 15:16

Killa @KillaXBT
239K Followers 163 Following Quantitative trader, 7 years. https://t.co/1jjvSeI8KW Closed
奶奶 capital @testinprodcap
13K Followers 3K Following psyops only. high priest @mutCarolineDAO. what would 奶奶 do? tweeting stream of consciousness
James Seyffart @JSeyff
183K Followers 5K Following Bloomberg analyst covering ETFs, crypto and asset management. Breaking down filings, flows and market structure. Views my own. Likes, RT's& Follows≠endorsements
Eric Balchunas @EricBalchunas
630K Followers 3K Following Senior ETF Analyst for @Bloomberg. Dad. Rutgers grad. Gen X-er. Author of "The Institutional ETF Toolbox" & "The Bogle Effect.” Co-host of Trillions & ETF IQ.
Roan @RohOnChain
82K Followers 427 Following building my life around AI agents, LLMs & quant systems for prediction markets + crypto
Parker @TheOtherParker_
10K Followers 1K Following Fix Finance Views are my own Contributor @apyx_fi | $APYX Cofounder @defidevcorp | $DFDV ex @krakenfx
NoLimit @NoLimitGains
1.5M Followers 151 Following Value investor | 10+ years of finding undervalued stocks | Founder & CEO @InTheAssembly
Pavel Durov @durov
3.7M Followers 1 Following Founder, CEO at @telegram (2013), founder, ex-CEO of @vkontakte (2006), part-time troll.
U.S. Department of Ju... @TheJusticeDept
2.4M Followers 196 Following Official account of the Justice Department 🇺🇸 DOJ Privacy Policy: https://t.co/2J3w9HbAuR
Andrej Karpathy @karpathy
4.4M Followers 1K Following
Haseeb Qureshi >|�... @hosseeb
150K Followers 1K Following Managing partner @dragonfly. Let's think step by step.
Pickle Cat @0xPickleCati
69K Followers 997 Following A cat who took the red pill and respawned as a chaotic green pickle 🥒 | Degen trader since 2013 (from Reddit) | Trades 👉 https://t.co/DZBDEnfLqU
David Tsai/蔡慎坤 @cskun1989
473K Followers 7K Following 中文撰稿人|独立时评人 中国政治・政经观察・独家爆料 读者爆料/商务联系:Email:[email protected] 🎥 YouTube ↓https://t.co/jctvsg54i8
John Carmack @ID_AA_Carmack
4.2M Followers 297 Following AGI at Keen Technologies, former CTO Oculus VR, Founder Id Software and Armadillo Aerospace
bz @bz_bbclub
5K Followers 3K Following
AP @friendscallmeap
9K Followers 822 Following https://t.co/zgifiZEpAF can't spell twink without win
Adam Back @adam3us
972K Followers 2K Following cypherpunk, cryptographer, privacy/ecash, inventor hashcash (Bitcoin mining) PhD Comp Sci. Co-Founder/CEO https://t.co/CysB3cs7Pp & Co-Founder/CEO @bstrco
DeFi^2 @DefiSquared
73K Followers 408 Following #1 Ranked trader on Bybit 2023 & 2024. Top 10 ranked wallet on DeBank. Follow for whale insights on crypto & markets.
Martin Shkreli @MartinShkreli
641K Followers 9K Following https://t.co/vJE5wyGbhv https://t.co/GUy99qMPSm - join our start-up focused Discord! [email protected]
Domer❤️🔥 @Domahhhh
41K Followers 891 Following Full-time political bettor since 2007. I don't tweet much, and we're all better off for it.
sysls @systematicls
62K Followers 73 Following All in @openforage. I thrived in all of the largest hedge funds managing systematic investment processes.
Marco Rubio @marcorubio
5.1M Followers 3K Following Christian,Husband,FatherAMERICAN,SecStateUS, Instagram:@marcorubio Truth:@marcorubio #GatorNation #FinsUpYou might like