

Albert Paredes @Al_Killswitch
Joined September 2026-
Tweets20
-
Followers5
-
Following105
-
Likes129

Discipline ☠️ 🥷

1% at a time will get you to profitability
Let's connect, talk security, and share resources. Following back everyone in the cybersecurity and tech space today! 🛡️🤗 @X
“Barcelos is stable, alert and responsive, with full movement.”

Update on Raoni Barcelos following #UFCVegas121 ufc.com/news/update-ra…
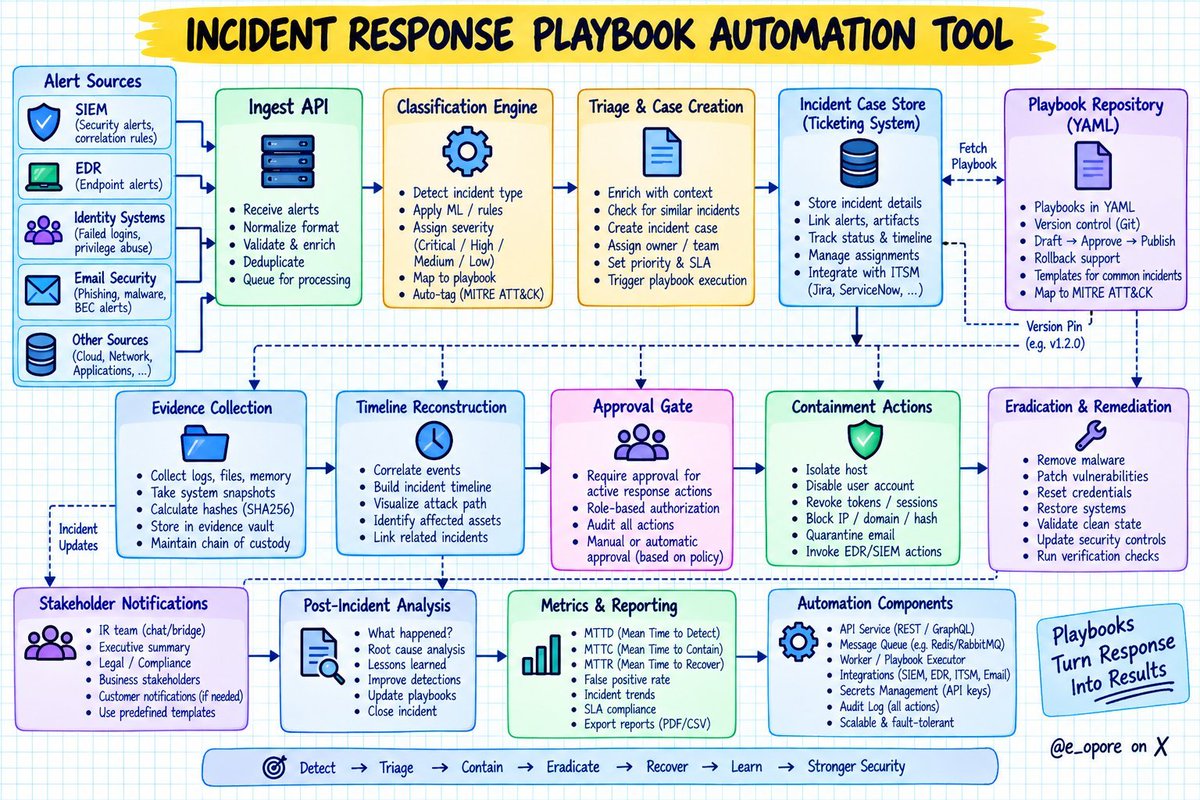
Incident Response Playbook Automation Workflow Credit to @e_opore #cybersecurity #cybersecurityawareness #infosec #SOC #Networks #cheatsheet
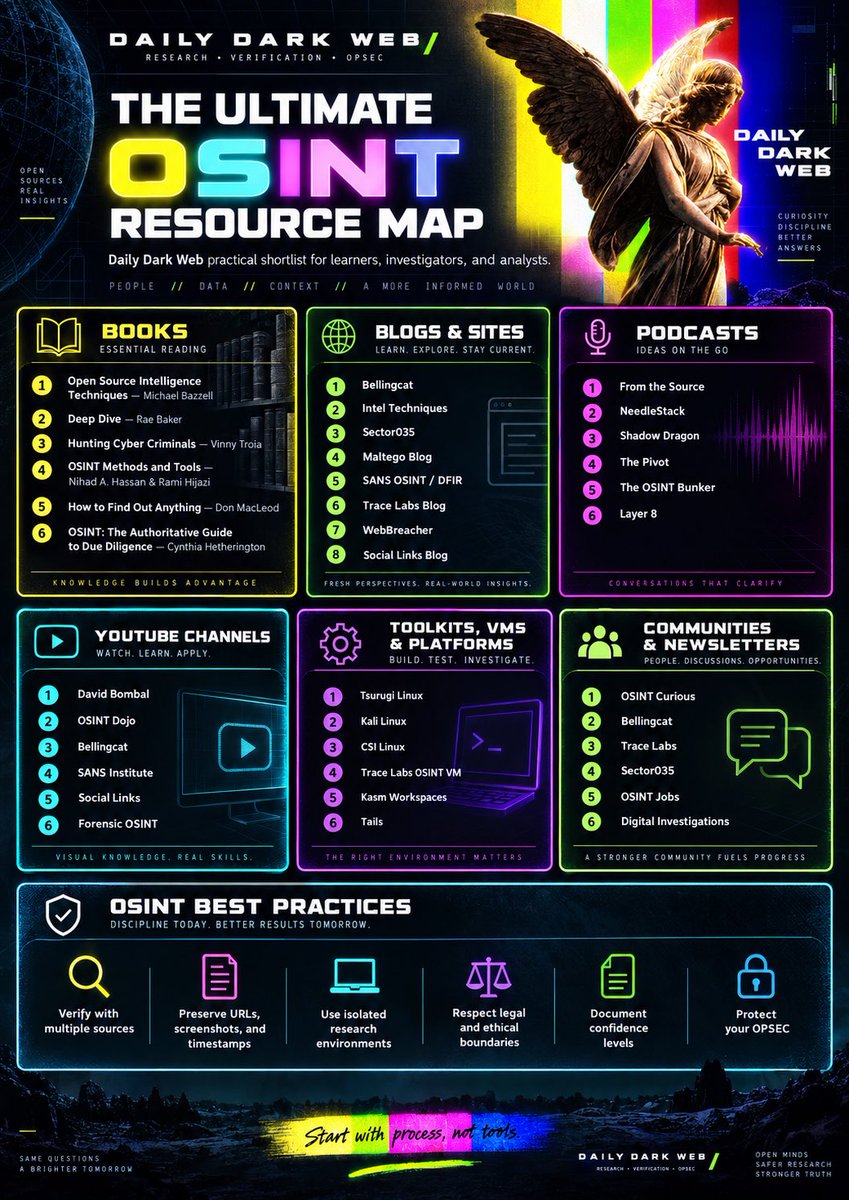
OSINT is not about having the most tools. It is about knowing where to look, how to validate what you find, and how to turn fragmented public information into reliable intelligence. I put together this OSINT Resource Map as a practical reference for analysts, investigators, researchers, and anyone building stronger open-source intelligence skills. It covers useful resources across: • Books • Blogs and research sites • Podcasts • YouTube channels • Toolkits, VMs, and platforms • Communities and newsletters But the most important part is the process: Verify with multiple sources. Preserve URLs, screenshots, and timestamps. Use isolated research environments. Respect legal and ethical boundaries. Document confidence levels. Protect your OPSEC. The biggest mistake in OSINT is assuming that more data automatically means better intelligence. It does not. Good OSINT comes from disciplined collection, careful correlation, and strong analytical judgment. Start with process, not tools. #OSINT #OpenSourceIntelligence #CyberSecurity #ThreatIntelligence #DigitalInvestigation #CyberThreats #SecurityResearch #OPSEC
🚨 A public exploit now targets an unpatched Ubuntu 26.04 kernel flaw that can escape containers and gain root on the host. The AF_UNIX bug is reachable through syscalls allowed by default Docker and Kubernetes seccomp profiles. No attacks are confirmed. How it works: thehackernews.com/2026/09/exploi…
NIST seeks feedback on updated operational technology guide with sector-specific challenges ow.ly/kOwv106F6zu
CISA plans to publish ‘lessons learned’ from critical infrastructure resilience initiative ow.ly/6lKw106F6zx
Attackers Manipulate AI Chatbots in Mass Disinformation, Phishing Campaign bit.ly/3Tkr4yM by Elizabeth Montalbano
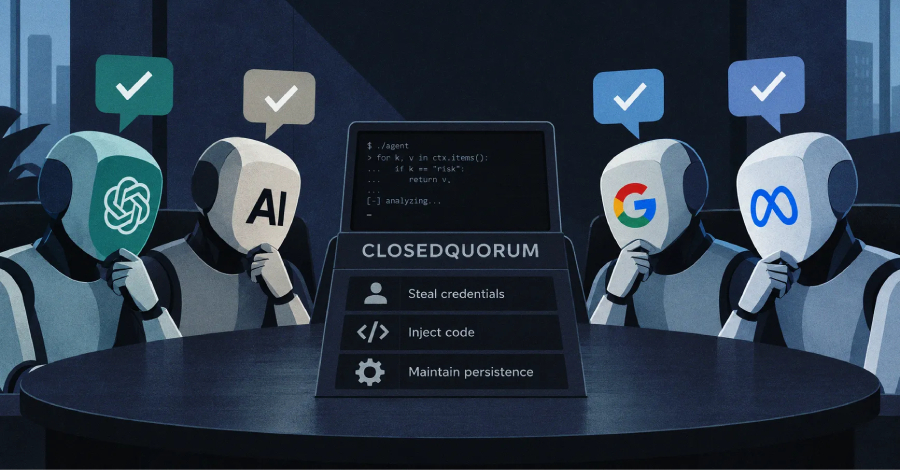
🛑 This Windows malware takes no orders from an attacker's server. It lets up to four AI models, including DeepSeek and Gemini, vote on its next move: steal credentials and wallet data, inject code, or stay installed. Read about CLOSEDQUORUM → thehackernews.com/2026/09/window…
Day 85/100 🔐 I found an exposed admin endpoint hidden in public JavaScript: "/admin-z8w5mv" The UI hid the link, but the server didn't properly protect the endpoint. Accessed the admin panel → deleted Carlos → lab solved. ✅ Lesson: hidden ≠ secure.

If you're in tech, Let's connect 🤝
@bidyut_io Currently in school myself. Definitely looking for more connections.
It's another day to go retry that failed lab,don't give up 💪

I’m documenting my journey from learning the fundamentals to building real security projects. If you’re into: 🛡️ Cybersecurity 🔵 Blue Team / SOC 🔴 Red Team 🐍 Python 🌐 Networking 💻 Tech Drop a follow and let’s connect. I’d love to meet more people building and learning here.
If you’re into cybersecurity, Ethical Hacking Appsec Penetration Testing Bug Bounty I’d love for us to connect.🤗

j @champagnevicyyw
13 Followers 956 Following

emmly @emmy_ly0
97 Followers 2K Following I’m a YouTube content creator,game lover and I also like movies

Emunah @Emunah_0x
622 Followers 600 Following Pentesting & Cryptography | Exploring security with curiosity & discipline | Chess strategist ♟ | Chelsea FC 💙 https://t.co/iKy07lVY4t
Archived Tactical @Archivedtactic
34K Followers 15 Following Documenting tactical trainings and real combat footages.
Team South Florida @TmSouthFlorida
8K Followers 4K Following We honor fallen law enforcement officers, support their families & agencies, recognize & participate in positive incidents & events, & work to bridge the gap.
Homeland Security @DHSgov
3.0M Followers 218 Following With honor and integrity, we will safeguard the American people, our homeland, and our values. #WeAreDHS
𝘡𝘔𝘚𝘍𝘔 @zmsfm
503K Followers 393 Following pfp: @LynaZF My links: https://t.co/t9sfCdmFOn Substar: https://t.co/r1LyxxmfP4 Content posted on this account is not funded through Patreon
Meta Fades @MetaFades
13K Followers 11 Following Meta Glasses Fight Club 🥊 Real people. Real fights. All Meta Style. TAG me in your MetaFades! #metafades
Straiker @straikerai
427 Followers 90 Following The Agentic Security Company https://t.co/eyNz9FrcLS
Malware Unicorn @malwareunicorn
166K Followers 6 Following Mostly on @malwareunicorn.bsky.social @Straikerai. Ex-Microsoft. Ex-Meta.
Conor McGregor @TheNotoriousMMA
11.0M Followers 2K Following 5 time World Champion. Pray EVERYDAY!! #GOD #FAMILY #COUNTRY #TRUTH 🇮🇪
Justin Gaethje 🇺�... @Justin_Gaethje
796K Followers 851 Following UFC Lightweight World Champion, NCAA D1 All-American for The University of Northern Colorado, 2x AZ State Champion Partnered with @Rainbetcom
UFC @ufc
12.7M Followers 731 Following #UFCVegas123 | MOICANO vs NOLAN | OCT 31 | 8pmET on @ParamountPlus
Dark Web Intelligence @DailyDarkWeb
212K Followers 0 Following Cyber Intel 24/7. 🔔 Subscribe for sources and more. Session ID: 051068fee6cdbbdaf0d7bff81e8e90b073abfd04d5bc574ce0dd93a7a41fc8a773
Inside Cybersecurity @InsideCyber
5K Followers 679 Following Daily news and analysis of federal policies and standards to protect data and networks. #cybersecurity Try it free for 30 days: https://t.co/ESgxsS6lcD
Dark Reading @DarkReading
358K Followers 49 Following One of the most widely read and trusted cybersecurity news sites, providing IT security professionals informed insights into the latest news and trends.
Donald J. Trump @realDonaldTrump
111.8M Followers 53 Following 45th & 47th President of the United States of America🇺🇸

Pooja @py_poojaa
2K Followers 2K Following Software Engineer | Tech | AI | Real Talk | Open for Collab
bidyut @bidyut_io
1K Followers 741 Following swe | playing with ai agents, models & tools honest talks + some fun too | dm for collabs
Full Sail University @FullSail
226K Followers 5K Following The official Twitter of Full Sail University, an educational leader for entertainment and emerging technologies careers.
PortSwigger Research @PortSwiggerRes
125K Followers 7 Following Web security research from the team at @PortSwigger
HackerOne @Hacker0x01
345K Followers 3K Following HackerOne makes security continuous. We unite AI and human insight through a unified platform to expose risk and eliminate it.
Web Security Academy @WebSecAcademy
146K Followers 36 Following Free web security training from @PortSwigger
Joseph Yearego @joseph_yearego
1 Followers 48 Following
Emunah @Emunah_0x
622 Followers 600 Following Pentesting & Cryptography | Exploring security with curiosity & discipline | Chess strategist ♟ | Chelsea FC 💙 https://t.co/iKy07lVY4t
Allie Howe @vtahowe
3K Followers 1K Following Member of Technical Staff @keycardai | Host of the @insecureagents Podcast
Harshleen @0xharshleen
30K Followers 671 Following Security Tester | Web3 My mumma thinks I just sit on a laptop all day
Huntress @HuntressLabs
42K Followers 539 Following Huntress X, run by @gleeda, @LindseyOD123, @susannigans, @benn333 + 1-2 Marketing Suits. Security news, research, and unfiltered takes.
David Bombal @davidbombal
184K Followers 786 Following YouTube: https://t.co/xGPVEj6ULN Discord: https://t.co/GZI30F45va Website: https://t.co/MpcS9ylBrV
TCM Security @TCMSecurity
219K Followers 422 Following Come learn to hack at TCM Security Academy! Affordable Learning with Quality results. Need support? Email [email protected]!
Intigriti @intigriti
217K Followers 671 Following Bug bounty & VDP platform trusted by the world’s largest organisations! 🌍
Ben Sadeghipour @NahamSec
254K Followers 1K Following Cofounder @hackinghub_io | Advisor @CaidoIO. I hack companies and make content about it. #NahamCon organizer. ex @hacker0x01🇮🇷
Katie Paxton-Fear @InsiderPhD
100K Followers 2K Following Dr, apparently. Security Adovcate @semgrep & Hacker. #BugBounty hunter & #infosec YouTuber. APIs & Interlinked OffSec, PhD in AI+Sec @hacknotcrime. she/her
Hack The Box @hackthebox_eu
253K Followers 227 Following Cyber Mastery: Community Inspired. Enterprise Trusted.
The XSS Rat - Proud X... @theXSSrat
170K Followers 1K Following Bug bounty profiles: https://t.co/3Uz5K130ah https://t.co/rzbqV5AmZ2 https://t.co/CDlzXdNvPB
meg west @cybersecmeg
156K Followers 926 Following Tweets about #dogs & travel & fitness & cybersecurity, oh my! Opinions are my own. 📧: [email protected]
LiveOverflow 🔴 hex... @LiveOverflow
165K Followers 1K Following wannabe hacker... he/him 🌱 grow your hacking skills @hextreeio
PentesterLab @PentesterLab
210K Followers 0 Following Don’t just learn tools and payloads. Learn why vulnerabilities exist. Hands-on web hacking, security code review, and real-world CVE labs.
John Hammond @_JohnHammond
329K Followers 3K Following Cybersecurity Researcher @HuntressLabs Just Hacking Training @JustHackingHQ w/ @ethicalhacker https://t.co/UtsNJiyiEk && https://t.co/narO3syzIy
NetworkChuck @NetworkChuck
273K Followers 845 Following Believer. Beard. Coffee. Tech. Youtube. Check the link in my bio to see my latest video!
LetsDefend @LetsDefendIO
143K Followers 1 Following LetsDefend, now part of Hack The Box. Read more: https://t.co/jxMnGZ4Yne
Shubham Sharma @Shubham_pen
62K Followers 94 Following In cybersecurity, you should be eager to learn new things.
Florian Roth ⚡️ @cyb3rops
227K Followers 3K Following Head of Research @nextronsystems #DFIR #YARA #Sigma | detection engineer | creator of @thor_scanner, Aurora, Sigma, LOKI, YARA-Forge | always busy ⌚️🐇 | vi/vim
nixCraft 🐧 @nixcraft
399K Followers 1 Following Love Linux/Unix, open source, and programming? Into Sysadmin & DevOps? Follow us! Boost your IT career with daily new tools, apps, and humor ⤵️
Abhishek @aacle_
50K Followers 292 Following Building @Vulncure ⚡ Better SaaS security shouldn't cost a fortune. AI-powered vulnerability finding & code fixes from $49/mo ↓ waitlist open → https://t.co/XkcGeBREXr
Hacking Articles @hackinarticles
312K Followers 489 Following House of Pentesters Join us: https://t.co/Y6XOlSP7YA
TryHackMe @tryhackme
314K Followers 84 Following An online platform that makes it easy to break into and upskill in cyber security, all through your browser.
The Hacker News @TheHackersNews
2.5M Followers 2K Following The #1 trusted source for cybersecurity news, insights, and analysis — built for defenders and trusted by decision-makers.
OccupytheWeb @three_cube
272K Followers 3K Following Pentester, Forensic investigator, and former college professor. Trained hackers at each US military and intelligence. Visit me at https://t.co/G478wug0p4
Cyber Security News @The_Cyber_News
82K Followers 287 Following World’s #1 Largest Cyber Security News 📰 Platform For Security Professionals. Get Latest #CybersecurityNews #HackingNews, #Cyberattack, #Threats & #breaches
Elizabeth Warren @SenWarren
6.8M Followers 486 Following U.S. Senator, Massachusetts. She/her/hers. Official Senate account.
Chuck Schumer @SenSchumer
3.7M Followers 21K Following Official Account of Senator Chuck Schumer, New York’s Senator and the Senate Democratic Leader.Trends for United States
You might like

















