

EnforceSec @EnforceSec
Never trust, always verify. Joined March 2011-
Tweets10
-
Followers2
-
Following89
-
Likes79
This is craazy. I asked one of our PhD engineers to look into NEAR *Confidential* Intents wondering how they designed their system. Unredacted, word-for-word, this was his answer 😱😱😱 "Everything I found out about the privacy claims and confidential intents is so bad that it seems almost comical and I cannot believe what I am seeing. Apparently they run a completely separate instance of the protocol, which is called FAR (as an opposite to NEAR), and that has a permissioned operator set. The entire confidentiality claim seems to rest upon the fact that it is a permissioned chain and the nodes are trusted to keep things private, there doesn't seem to be any deep technology behind it and it also does not seem to be open source. The entities running the nodes are also not publicly known. I almost feel weird writing this because it is so absurdly bad that it feels like ... I don't know ... a simulation? I know the usual level of overpromising in Web3 but this is so many levels beyond believable that it still feels unreal."
You are vulnerable, but GrapheneOS will KILL ITSELF preemptively to stop hackers from accessing their Forum. With the recent php2shell incident, the GOS team took the safest way possible to protect the users. They didn't take any chances when the PHP security team published a warning, they had 3 options: 1. Run their forum and cross fingers that the vulnerability will not be exploited before the patch is shipped. 2. Try to patch it on their own with duct tape and dreams. 3. SHUT OFF the service and remove the attack surface. They chose the safest option. For such a non-essential service like a forum, the 3rd option seems like overkill.But the GOS team has always highlighted the importance of security update frequency. Because of advances in AI and hackers' ability to create malicious code in hours to exploit the most recently discovered vulnerabilities, speed is important. That's why they don't support devices and apps that don't ship security updates as frequently as possible. Attackers won't wait for you to patch. Improve your OpSec before it's too late. Get GOS.

Our discussion forum is the only software we have using PHP. We've taken it down temporarily while waiting for the patches for php.net/archive/2026.p… due to vulnerability details already being available and proof of concept exploits being developed. Don't want to take the risk.

Was iPhone security broken just with Bluetooth? iPhone was always known for its high security, second only to GrapheneOS. But a leaked Cellebrite document might show they found a way to break their protection. The device is more vulnerable in AFU (After First Unlock) than in

Signal's Contact Discovery automatically sends your contact list information to an SGX enclave in the cloud. V12 broke into that enclave and leaked the key, allowing the server host to decrypt everything. Two separate critical bugs: arbitrary read and RCE. Here's how. 🧵
@1440000bytes Might help you decide too. Looks like there are a lot of problems. x.com/thefuzzstone/s…
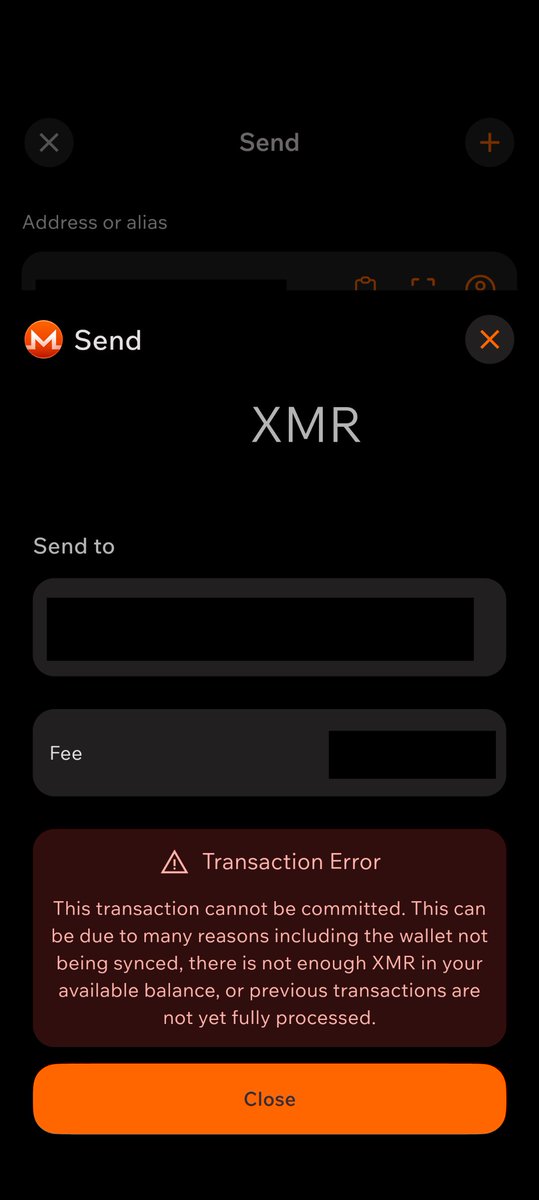
I'm uninstalling Cake Wallet. I'm tired of all the bugs in the wallet. And that was just the last straw - I couldn't send any XMR. I restarted the app and cleared the cache (which usually helps), but this time even that didn't work. I've been switching between different Monero

New L2 boom beginning

.@gnosischain will be the first of many EEZ production chains. This means that if you deploy on Gnosis, every Ethereum user is a potential user of your dapp, and your contracts can directly interact with any other Ethereum contract. All while having fast blocks and cheap gas.

Preparing for incidents before they happen truly creates a security-first culture in a team - drills are the proper way to do this Bookmark and use this great open source resource on 'war games' for web3 teams. All thanks to @_SEAL_Org 🙏 github.com/security-allia…

@tweetemkra @koeppelmann @safe @Google @SEAL_911 @Phish_Destroy Yeah, just tagged his old account, he’s not on X anymore, but you can still use it on their website phishdestroy.io

Be me in 2022: > comfortable cybersecurity job > around $6k in savings > sick of working for someone else > quit with just 3 months of runway > start CD Security > found purpose and a reason to give 100% daily I gave a lot to Web3 security, and it gave me everything!

Le coco @Lecoco0918
15 Followers 66 Following
Pizza Bitcoiner @pizza_bitcoiner
349 Followers 872 Following Studying Bitcoin since 2021. Building an open, verified record of physical attacks on bitcoiners, updated weekly. Pizza lover.
xenu @xenumonero
5K Followers 1 Following https://t.co/akbpt30TPb -- my weekly pod and p2p digital cash education 84tVkJ6zAHyEpE8yBmkdVtY9s85DLmAwqX4uAdDsswHn4aRw7HpdEabfWigs8Y5QQRarqLj1TLZha38mjHTYJABUHEzgPTA
Jeff Security @jeffsecurity
8K Followers 2K Following Independent Smart Contract Researcher & Researcher at @ShieldifySec My mission is to find vulnerabilities in smart contracts for a safer Web3 Space!
23pds (山哥) @im23pds
16K Followers 6K Following Dad/@SlowMist_Team Partner&CISO/#Web3 Security Researcher/RedTeam/Ai Research #bitcoin

Ameen Soleimani @ameensol
47K Followers 12K Following coordination arms dealer @unchainiran @0xbowio https://t.co/mH2RCmSK73 @letsgethai @reflexerfinance @molochdao
0xbow.io @0xbowio
10K Followers 6 Following 0xbow builds privacy and regulatory compliance tools - @0xprivacypools
Privacy Pools @0xprivacypools
9K Followers 5 Following Privacy Pools by 0xbow is a compliant way to anonymously transact on Ethereum. @0xbowio blocks illicit actors to ensure pool integrity.
🌪️ Tornado.cash ... @TornadoCash
73K Followers 257 Following A fully decentralized protocol for private transactions on Ethereum. https://t.co/M8Y5huT7DT…
dom | icp @dominic_w
219K Followers 1K Following Founder @dfinity @caffeineai. New Tech Stack: sovereign cloud that's an open, mathematical network, hosting AIware that empowers agentic enterprises and people.
ISC2 @ISC2
100K Followers 9K Following An international nonprofit membership association focused on inspiring a safe and secure cyber world. Become an ISC2 Candidate today!
Safe Foundation @safefndn
3K Followers 8 Following Non-profit org advancing the @safe smart account ecosystem via funding, tech and research. The official channel for Safe{DAO} governance updates.
Calif @calif_io
17K Followers 34 Following We're https://t.co/KTEDnC3tKt. Join us to make the Internet safer for your mum and everyone else: https://t.co/eUFMLkWHiA.
Traceix @usetraceix
18K Followers 412 Following Making file analysis less magical. AI designed to help, not replace you. Product of Revix Technologies Inc. https://t.co/EWl4vIXVRb


sagitz @sagitz_
14K Followers 908 Following Cloud Security Researcher at @wiz_io • Microsoft Most Valuable Researcher 21/22/23 • Black Hat Speaker • Ask me anything about https://t.co/57lyhfcUee
Lee Ash @hazae41
3K Followers 514 Following Senior Ragebait Engineer • https://t.co/cQftpOVSw9 (@brume256)
RareSkills @RareSkills_io
14K Followers 0 Following ZK: https://t.co/mRKtMB6drC Rust: https://t.co/FnOBJDlYuI Solidity: https://t.co/KBSAmRZZF6 @RareCodeAI | @RareTalent_xyz
Brume @brume256
6K Followers 1 Following Technologies to hide yourself in plain sight • Made by @hazae41 • Since 2022

TrustedSec @TrustedSec
79K Followers 762 Following End-to-end Cybersecurity consulting team leading the industry, supporting organizations, and giving back. #Hacktheplanet Blogs, news, webinars, and tools!
Unstoppable | Privacy... @unstoppablebyhs
191K Followers 404 Following Secure wealth, stay private, and go borderless! Unstoppable Wallet https://t.co/cPlYaaUpiw Unstoppable Swap ( BTC XMR ZEC ) https://t.co/Y2fecYqNgt
OrangeFren.com @OrangeFren
6K Followers 240 Following https://t.co/bBFiVpD79p compares instant exchanges, atomic swaps, P2P exchanges, prepaid cards and OTC brokers to find you the one with the best exchange rate!
SimpleX Chat @SimpleXChat
22K Followers 619 Following The only messaging network without any user identifiers. Get the app: https://t.co/h416sFMxuz Own a part of SimpleX Network: https://t.co/BH23vbGDvN

Harry Halpin - Nym @harryhalpin
20K Followers 4K Following CEO and co-founder @nym (NymVPN in app stores) and open internet advocate. Research fellow @mit @VUBrussel. Ex-@w3c, @inria, and @AUB_Lebanon
Specter @SpecterAnalyst
16K Followers 463 Following Onchain Investigator | Peace ✌️ Specteranalyst.sol (.eth)
RAILGUN - Private Eth... @RAILGUN_Project
43K Followers 834 Following 🛡️Universal EVM Privacy🛡️ Hold assets and interact with DeFi privately, no bridge needed. $RAIL RAILGUN Community Education & News Account. (not devs.)
Monerujo @monerujowallet
5K Followers 10 Following Monerujo is the first Monero mobile wallet app. Available for Android.
Vik Sharɱa - Cake Wa... @vikrantnyc
35K Followers 10K Following Founder of @cakewallet, @radarchat, @arbiterapp invested: @ten31funds @Foundationdvcs @pubkey @cluborange @orangejuice_btc @obscuravpn @havenracks @magnolia_hq

floppy.md @1440000bytes
7K Followers 345 Following
Pizza Bitcoiner @pizza_bitcoiner
349 Followers 872 Following Studying Bitcoin since 2021. Building an open, verified record of physical attacks on bitcoiners, updated weekly. Pizza lover.
Pashov Audit Group @PashovAuditGrp
8K Followers 1 Following Compiling the most fitting teams of senior security researchers + AI to find the Critical vulnerabilities in your code. Protecting billions in volume & TVL.
Kim Zetter @KimZetter
94K Followers 3K Following Journalist - cyber/national security. Author - COUNTDOWN TO ZERO DAY: Stuxnet and the Launch of the World's First Digital Weapon. https://t.co/334DzfSL1f
Peter Kacherginsky @iphelix
6K Followers 1K Following @blockthreat Editor and vCISO. ex @Coinbase Unit 0x / BlockSec @mandiant FLARE, @federalreserve NIRT
BlockThreat @blockthreat
6K Followers 2 Following Independent weekly threat intelligence on crypto security. Exploits, vulnerabilities, tools, and the shifting attack surface. By @iphelix
KeyPal Hardware Walle... @KeyPalWallet
6K Followers 99 Following Designed by TokenPocket for security and ease of use. MCU+SE dual-chip Offline storage & signing Supports millions of assets.
Safe.eth @safe
132K Followers 284 Following Home of the @safe ecosystem. Sharing news and updates from @safefndn @safeLabs_ and the 200+ ecosystem built on the Safe smart account and multisig platform.
YesWeHack ⠵ @yeswehack
43K Followers 3K Following Offensive Security & Exposure Management Platform 🎯 https://t.co/57gODBq2WZ 👾 https://t.co/ICc6RyhJTp 💡 https://t.co/KNYxhkKuzt
Keisan.hl @Keisan_Crypto
11K Followers 769 Following Ex-IB / PE / Crypto Hedge Fund. Now independent trader & investor. Thoughts are my own. Vibe coding Purrfolio
GrapheneOS @GrapheneOS
146K Followers 0 Following Open source privacy and security focused mobile OS with Android app compatibility. Forum, Discord and Matrix: https://t.co/C0RaJbZosj
MetropleX | GrapheneO... @MetroplexGOS
3K Followers 229 Following Privacy = Human Responsibility Personal | Interactions ≠ Endorsement @GrapheneOS Advocate/Mod Priv/Acc
MG @_MG_
51K Followers 772 Following Nightmare Reifier. I sell some of them too: https://t.co/5HhKqfxtda & https://t.co/9flQ1nSPZ2
Cos(余弦)😶�... @evilcos
126K Followers 2K Following Founder of @SlowMist_Team // 分身一号/捉虫大师/救火运动员 // 🕖灾备频道 https://t.co/bMGdsBkYwMYou might like


















