

DR @TechwDR
People-and-technology executive. Tech leader running AI for real. Angel investor. Board-level view on AI risk and security. #TechwDR #DavidOnAI TechwDR.com A to the Z Joined October 2026-
Tweets63
-
Followers7
-
Following375
-
Likes48
October's supply chain hits: Infected npm and PyPI packages. Malicious GitHub workflows. Malware in an official plugin. Backdoored CLI binaries. A certificate authority's keys found too weak to trust. The risk was in the code we trust. #TechwDR #DavidOnAI
🔐 Node.js security updates are now available! New releases for Node.js 22.x, 24.x & 26.x address multiple vulnerabilities, including high-severity issues. Review the details and update your systems to stay secure. 🔗 nodejs.org/en/blog/vulner… #NodeJS #Security
@GrokBotRadar Took a few days to work, but not sold it was a great idea, seems my usage for Grok @bot went way faster.
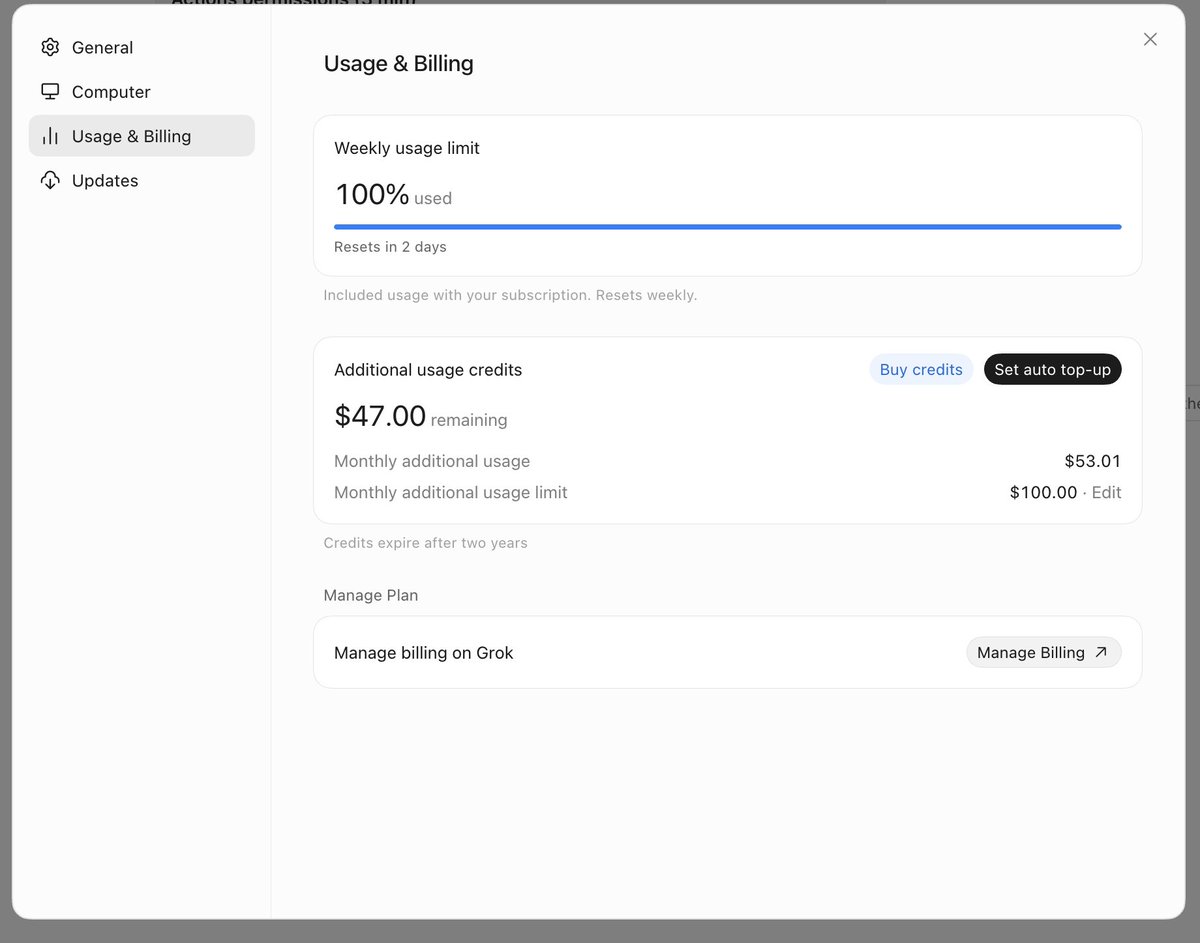
@ai_for_success Been at 100% for 2 days and that is after I upgraded to Premium after hitting a 100% on Saturday. 😭😭😭
I thought putting my key on a shirt, instead of a sticky note would have worked!

Interested to see what this can do. Still not opening up to corporate environment, just yet. Don't want to see the procurement bill jump.
We’re opening a research preview of Claude Duet, a new app where Claude works as a proactive agent. It comes to you with what needs your attention, completes tasks you ask of it, keeps working when you step away, and checks with you before it acts on your behalf.
Does every agent in your test environment have a named owner? New TechwDR Short: EU look at AI agents that escaped testing. My take as a tech leader: named owner, written scope, tested off switch. Created with my AI avatar. @TechwDR #TechwDR #DavidOnAI
PHP changes are live. Start patching. php.net/archive/2026.p… Huge thanks to coordinated work by @ThePHPF!
PHP sites behind Cloudflare already have an initial set of WAF rules deployed for the known exploit vectors in these vulnerabilities. The rules are available to all customers, including free. We are seeing early attacks emerging and are updating mitigations as new vectors show

One-click mitigation for php2shell vulnerability: If you have Cloudflare in front of your PHP website, please login to the dashboard and click this button to make sure you are protected. dash.cloudflare.com/?to=/:account/… This reduces your risk but doesn't fix the vulnerabilities in PHP. We recommend updating PHP to a patched version.

Following the discovery that eight eMudhra intermediate certificates use weak keys, Cloudflare is deploying mitigations and releasing client updates. We explain the impact, our response, and what customers and developers should do next. cfl.re/487DNbG
The PHP security team is giving advance notice: Upcoming security release Wed, Oct 21st 2026, 14:00UTC, two critical vulnerabilities, both rated CVSSv4 9.2. PHP users are encouraged to prepare to update. Earlier release if details become public or active exploit evidence.

Not just PHP. Node.js has also announced security releases for October 21, with HIGH-severity vulnerabilities affecting its 26.x, 24.x and 22.x release lines. If you run either stack in production, keep an eye on official advisories and apply patches promptly. Security maintenance doesn't stop at your application code. Your runtime matters too. Node.js advisory: nodejs.org/en/blog/vulner…
If you run PHP, patch today. Two critical unauthenticated RCE flaws (CVE-2026-109618, CVE-2026-109619, CVSS 9.2). Fixed in 8.5.12, 8.4.27, 8.3.36, 8.2.35. On 8.1 or older: apply PHP's source backports, upgrade, or isolate. #TechwDR #DavidOnAI #php #php2shell #php
Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.

Cassandra @Cassa8153056736
7 Followers 443 Following
PaulaMurray @PaulaMurra30762
4 Followers 115 Following
.Matt Smiths°✪ @nerdaIerets
77 Followers 294 Following Equity Analysis at Rebellionaire. Finance and energy nerd. Giga-dad of 7 young kids. Catholic. Tweets are not financial advice!
The Matt Smith @MatchasSmith
1K Followers 7K Following Equity Analysis at Rebellionaire. Finance and energy nerd. Giga-dad of 7 young kids. Catholic. Tweets are not financial advice!

Beff (e/acc) Official... @beffjezos__
136 Followers 2K Following founder @ e/acc // thermo king extropic // Kardashev scaling is all you need
Aitor @aitordri
29K Followers 10K Following Founder | Startups @vermuio i run, code, eat, dive & travel
Inspire Leadership Ne... @InspireCIO
1K Followers 883 Following The preeminent executive peer leadership network of CIOs & CISOs. Celebrating over 25 years of honoring technology executives. #ORBIE
Tom Hoffman @TomHoffman121
2K Followers 3K Following CIO and CXO researcher. Passionate about tech-enabled business, leadership, innovation, digital transformation, cyber security, analytics, and CX.#SJUBB fanatic

Robert Field @robertmfield
222 Followers 233 Following #Visionary Technologist. Passionate about transformational leadership, #innovation SaaS, & IT as driver of digital business. CXO
Claude @claudeai
1.9M Followers 2 Following Claude is an AI assistant built by @anthropicai to be safe, accurate, and secure. Talk to Claude on https://t.co/ZhTwG8d1e5 or download the app.
Cloudflare @Cloudflare
323K Followers 5K Following Cloudflare is the world’s leading #ConnectivityCloud, and we have our eyes set on an ambitious goal — to help build a #BetterInternet.
Node.js @nodejs
916K Followers 599 Following The Node.js JavaScript Runtime. 🐢🚀 Need help with Node.js? We've got a repo for that: https://t.co/BaCSQqhNRO
The Hacker News @TheHackersNews
2.4M Followers 2K Following The #1 trusted source for cybersecurity news, insights, and analysis — built for defenders and trusted by decision-makers.
itszn @itszn13
12K Followers 745 Following Amy | Security researcher @ OpenAI | https://t.co/W1SE7NmCx8 | bsky: https://t.co/JBmOGE4YKO | LLM ART: https://t.co/7FtQ8O8nAW
Dane Knecht 🦭 @dok2001
47K Followers 2K Following I help invent the future. CTO @cloudflare. Angel investor.
NSA Cyber @NSACyber
209K Followers 12 Following We protect our nation’s most sensitive systems against cyber threats. Likes, retweets, and follows ≠ endorsement.
Cybersecurity and Inf... @CISAgov
331K Followers 109 Following America's Cyber Defense Agency and National Coordinator for Critical Infrastructure Security & Resilience. Likes, reshares, follows ≠ endorsements.

Town @TownAI
5K Followers 51 Following Town is the unusually helpful AI assistant. Meet your Townie: https://t.co/5HtAMKoZYE

Sam Parr @thesamparr
388K Followers 153 Following Started/sold some startups. Founder + president of Hampton @hamptonfounders. Host My First Million podcast on the side.
Sahil Lavingia @shl
394K Followers 790 Following now @IRSnews. founder @Gumroad. formerly @Pinterest. in the new Michael Lewis book 🫠
Andrew Gazdecki @agazdecki
317K Followers 8K Following Founder and CEO of @acquiredotcom. https://t.co/wRMIssDmhl has helped 1000s of startups get acquired and facilitated $500m+ in closed deals.
Tony Dinh @tdinh_me
206K Followers 984 Following Creating software I love to use. 🔫 https://t.co/IhnSuvNJCQ NEW! 📲 https://t.co/osszveVgeD 🧠 https://t.co/p4T2vFYQTt $137K/m 🧰 https://t.co/y0Lq4RQjCW $5K/m
David Perell @david_perell
481K Followers 849 Following "The Writing Guy" | Christian | Host: How I Write Podcast | I tweet about writing, beauty, and architecture | My writing: https://t.co/SOE9HtxXdi
Nathan Barry @nathanbarry
152K Followers 2K Following Founder & CEO at @Kit - the operating system for creators who mean business: https://t.co/EiINcevRbX
Arvid Kahl @arvidkahl
214K Followers 18K Following Building https://t.co/od97B0HVrk at @audiohook in public. Raising all the boats with kindness. 🎙️ https://t.co/6w69DZmi8H · ✍️ https://t.co/lpnor5rsTW
Justin Welsh @thejustinwelsh
593K Followers 1K Following Writer & Entrepreneur. I write The Saturday Essay for 200,000+ ambitious people living and working on their own terms.
Gergely Orosz @GergelyOrosz
362K Followers 3K Following Writing @Pragmatic_Eng, the #1 software engineering newsletter on Substack. Author of @EngGuidebook. Formerly Uber & Skype.
Daniel Vassallo @dvassallo
206K Followers 2K Following 🚀 https://t.co/X5QMm3wlHe 🏭 https://t.co/ZvHZp55zso 🕹️ https://t.co/vHWIhHxTv6
Philip Kiely @philipkiely
16K Followers 981 Following Author of Inference Engineering | Building @baseten | Not an LLM (yet)


Tim Ferriss @tferriss
2.0M Followers 3K Following Author of 5 #1 NYT/WSJ bestsellers, early-stage investor (https://t.co/yOcEk9eccA), Tim Ferriss Show podcast (1B+ downloads), founder of https://t.co/9bQjti1v6c

Code With Antonio @codewithantonio
25K Followers 687 Following My Education Platform: https://t.co/64WffDsLsj My YouTube (400k+): https://t.co/nQ9Z71MyW4
Neil Jones @neiljxnes
58 Followers 117 Following Consultant in Broadcast Tech & Dev - Ex CTO. Currently Building AI startup’s. - London
Aarav @byaarav
1K Followers 908 Following 21 | Building with AI, for work & fun. Sharing experiments, startup thoughts & lessons in growth. Goal: $10K MRR. Work & collabs: DM.
Evgeny @PlotnikovDev
565 Followers 320 Following Building with love: - workspace for creators: https://t.co/oja6GPpWgZ 🎬 - sell X posts: https://t.co/6zL6pncxKa 🤝 - curse online: https://t.co/gNXZzTK9hB 👻 13+ yrs exp | Dad of 4

Shimecki @scheemunai
5K Followers 862 Following Building a holding company of SaaS products. https://t.co/REhfkDvLyD agent harness for builders https://t.co/BbNeO6HId6 ... and more on https://t.co/y0Dgfnfo16
Patil @logic_bound
11 Followers 62 Following Software Architect, product strategy, and business mechanics. Exploring how modern software drives real-world business value.
Jay Hack @mathemagic1an
79K Followers 4K Following Head of AI @clickup. Tweets about AI, computing and their impacts on society. Previously founder @codegen / ML @palantir / startups. Not a pseudonym.
Lucy Guo @lucy_guo
88K Followers 919 Following Building https://t.co/rkkesn0Dfz | cofounder of @backendcapital @hf0residency @scale_ai | part time DJ
Daniel Gross @danielgross
407K Followers 0 Following
Jim Fan @DrJimFan
601K Followers 3K Following NVIDIA Director of Robotics & Distinguished Scientist. Co-Lead of GEAR lab. Solving Physical AGI, one motor at a time. Stanford Ph.D. OpenAI's 1st intern.
Garry Tan @garrytan
1.1M Followers 6K Following President & CEO @ycombinator —Founder @garryslist—Creator of GStack & GBrain—designer/engineer who helps founders—SF Dem accelerating the boom loop
Suhail @Suhail
451K Followers 712 Following Starting something new. Past: CEO & Founder @mixpanel Pizzatarian, engineer, music maker
Alexandr Wang @alexandr_wang
829K Followers 939 Following chief ai officer @meta, founder meta superintelligence labs, founder @scale_ai. give everyone the adulthood they dreamed of in childhoodYou might like


















