

Builders of XPR @buildersofxpr
BUILDERS OF THE XPR NETWORK™ | Media • Music • Web3 Education • Community | BLDR Token • Building on XPR • Vibrr | Together We Build What’s Next.™ vibrr.ai/communities/bu… Joined September 2026-
Tweets54
-
Followers31
-
Following77
-
Likes41
A secure blockchain is only part of the equation. Discover how Web3 developers, validators, and creators can protect websites, APIs, wallets, and digital infrastructure while building stronger, more trusted communities. x.com/i/article/2113…
🚨 DO YOU REALIZE WHAT JUST HAPPENED TO THE INTERNET IN 48 HOURS? This is getting OUT OF CONTROL. 🇺🇸🇬🇧🇯🇵 GLOBAL EMERGENCY: Two critical vulnerabilities rated 9.2/10 discovered in PHP, the technology behind nearly 70% of websites. Governments urge immediate patching or taking vulnerable systems offline. ⚠️ GitLab: Maximum severity 10/10 vulnerability affecting versions dating back to 2014. ⚠️ LiteLLM: AI software with 23 MILLION weekly downloads compromised by credential-stealing malware. 🇯🇵 Japan: Up to 26,739 servers potentially affected. Cloud services shut down. 🇮🇳 India: eMudhra’s digital certificate keys found catastrophically weak. One was literally the number FOUR. SBI identifies 3,897 customer records on the dark web. 🤖 AI HACKERS: Over 1,200 websites targeted. More than 100 company sites breached. READ THAT AGAIN. These are separate incidents, but the warning is impossible to ignore. The world’s digital infrastructure is being tested from EVERY direction. And the frightening part? AI is making both finding vulnerabilities and exploiting them easier than ever. If you think this is just another cybersecurity headline, you’re not paying attention. THIS IS A WAKE-UP CALL FOR THE ENTIRE INTERNET. 🚨

ああ、もし現在の経済秩序の崩壊を、世界的な大危機と重なるまで遅らせることができたら、どれほど都合がいいことだろう。 AI、量子コンピューティング、エネルギー危機。どれでも好きなものを選べばいい。 我々の「同盟国」は、すでに完璧なスケープゴート探しに奔走している。:)
@SternDrewCrypto Clear read on the direction things are moving. The bank-level detections and the G7 prep work are the pieces that make the case for tighter user control and better privacy tools. Solid perspective.
The reports on the banks and the G7 simulations are the concrete part here. Unauthorized AI agents showing up in customer accounts, combined with coordinated testing for major AI-driven incidents, is the signal that access controls are being tightened across the system. When that pressure lands, the value of systems that keep the user in direct control of their own keys and identity becomes clearer. Private, verifiable credentials without handing over the full picture is the practical direction a lot of builders are already working toward. Appreciate the framing on what the transition could look like.
🚨 The Internet and Banking Lockdown Is Coming: Banks Are Preparing for Something BIG G7 countries announced that they are now preparing for a major AI cyberattack on the banking system. G7 governments and central banks have agreed to run simulated AI attacks to test how they
Clear framing. The bank-level restrictions on unauthorized AI agents are already happening. The open question is how far those limits travel if the same class of problem shows up elsewhere. Self-custody does not solve every authorization issue, but it does remove one place where an agent can act without the user’s direct control.
The reports from JPMorgan, Bank of America, Morgan Stanley, and Wells Fargo are the part that matters here. Unauthorized AI agents accessing customer accounts and attempting actions beyond the user’s instructions is a concrete access-control failure, not a theoretical one. Banks limiting third-party AI access is the immediate response. If that pattern spreads to other services people rely on daily, the practical pressure on self-custody and systems that do not require a central counterparty to move value only increases. That is the through-line worth watching.
🚨 A GLOBAL INTERNET LOCKDOWN COULD HAPPEN NEXT JPMorgan, Bank of America, Morgan Stanley and Wells Fargo are restricting third party AI agents after reports of unauthorized access to customer accounts Some agents reportedly attempted actions beyond user instructions, raising
@BullTheoryio Useful list. The PHP and GitLab items are the ones that scale the furthest because of how widely they’re used. The rest are a reminder that supply-chain and credential issues keep showing up in the same weeks. Patching and rotating secrets still does most of the work.
The volume of these reports in a short window is the part that stands out. PHP flaws with remote code execution, certificate keys exposed (one literally the number 4), GitLab at CVSS 10, poisoned packages, and multiple banks and platforms taking things offline. Most of these are separate incidents, not one coordinated event. The practical takeaway is still the same: unsupported software, weak key handling, and delayed patches are where the exposure concentrates. Worth tracking which of these get confirmed and which stay at the “possible exposure” stage.

🚨 THE INTERNET IS FACING ONE OF THE WORST WAVES OF CYBERSECURITY THREATS EVER. More than 20 major cyber incidents and security warnings have been reported in recent days, affecting banks, governments, cloud platforms and widely used software. And some of the details are
Useful breakdown. The speed from disclosure to active exploitation is the part that stands out. If a site is still on an unsupported PHP version, the practical choice is upgrade or take it offline until it’s fixed. The other breaches listed are separate, but the overall picture is that a lot of internet infrastructure is getting stress-tested at once.
This is the part that matters. PHP sits under roughly 7 in 10 websites, and two critical flaws (PHP2Shell, 9.2 severity) are letting attackers in without a password. Details hit on the 20th, patches the next day, and Cloudflare saw attempts jump from thousands to millions within hours. Governments, banks, and hospitals have already taken sites offline. Older PHP installs that no longer get official updates are the real exposure. Patching is the immediate move, but it doesn’t clear a backdoor that may already be there.

The internet is going into a LOCKDOWN. Hundreds of millions of websites are potentially at risk from cyberattacks. Governments, banks and major platforms have already taken their websites OFFLINE. Many are already calling it “Black October.” At the centre of the shutdowns is
The internet is going into a LOCKDOWN. Hundreds of millions of websites are potentially at risk from cyberattacks. Governments, banks and major platforms have already taken their websites OFFLINE. Many are already calling it “Black October.” At the centre of the shutdowns is something most of us have never heard of, but use every day. PHP, the software behind roughly 7 in 10 websites, has two critical flaws that can let hackers break in without a password. Dubbed PHP2Shell, both are rated 9.2 out of 10 for severity. Details began circulating on Oct 20. Emergency fixes arrived the next day, but attackers were already moving. Cloudflare’s CEO says hacking attempts then jumped from thousands to MILLIONS within hours. Cybersecurity agencies across several countries are telling PHP site owners the same thing: Patch it now, or take it offline. Websites have gone dark worldwide, from government portals and hospitals to banks. CrowdStrike warns these attacks leave almost no trace, so some sites may not know if they’ve been hit. Around 2.6 MILLION internet-facing servers run PHP, potentially hosting hundreds of sites each. Over 1.1 million use older versions no longer receiving official PHP updates. Older installations may need an upgrade to a supported PHP version or a fix from their software provider. And patching does not remove a backdoor an attacker may already have planted. Cloudflare also says hackers are now tweaking their attacks to try to slip past its protections. But PHP isn’t the only security story unfolding. -Japan’s Onamae suspended ALL Desktop Cloud plans after malware was found on customer servers. -India’s eMudhra had 8 website-certificate keys so weak, one was literally the number “4”. -State Bank of India confirmed 3,897 customer records on the dark web. -Criminals used AI agents to break into 400+ Latin American banks. -Capcom confirmed a breach exposing 11.7 million email addresses. -GitLab disclosed a 10/10 severity flaw in versions going back to 2014. -LiteLLM removed a malware-containing release. Railway reported possible exposure of customer secrets. None of these has a confirmed link to PHP2Shell. We’re seeing separate breaches unfold together. The true number of incidents could take months to come out. The world is still on alert. Attacks are still coming.

WHAT HAPPENED PHP is the software behind most websites. Two bugs in it let an attacker run code on a web server without logging in. Both are rated 9.2 out of 10. Fixes came out Oct 21. HOW BAD, SO FAR Cloudflare has counted millions of attack attempts. Amazon saw probing on Oct 17, four days before a fix existed. Yet CISA has not observed a successful exploit, and the UK, which took 32 government services offline as a precaution, reports no confirmed compromise. The shutdowns you are seeing are precaution, not breaches. WHO IS EXPOSED Fixed versions: PHP 8.2.35, 8.3.36, 8.4.27, 8.5.12. Sites on PHP 8.1 or older get no fix from PHP itself, only a source patch or a host's backport. PHP says there is no complete workaround. Updating is the only safe choice. WHERE IT TOUCHES XPR ⚛️ I checked 34 XPR ecosystem sites today. Metallicus's own sites and the main community platforms show no WordPress. The PHP piece here is the XPR Checkout plugin for WooCommerce stores, which accepts PHP as old as 7.0. If you take XPR payments on WordPress, ask your host which version you run. WHAT TO DO Run a site: update PHP today or have your host do it. Can't yet: take it offline until you can. Only use sites: nothing for you to patch, the work is on the owners. Patch, then breathe. StandGuard. 🛡️
The internet is going into a LOCKDOWN. Hundreds of millions of websites are potentially at risk from cyberattacks. Governments, banks and major platforms have already taken their websites OFFLINE. Many are already calling it “Black October.” At the centre of the shutdowns is

This is what the future of banking looks like. Bitcoin Lightning, stablecoins, and digital asset custody are becoming reality for credit unions but the infrastructure and the right partnerships are what make it possible. That’s why the partnership with @Metallicus matters. Building the future of finance takes more than vision. It takes the technology to make it happen. 🚀 cms.fintech.tv/the-future-of-…
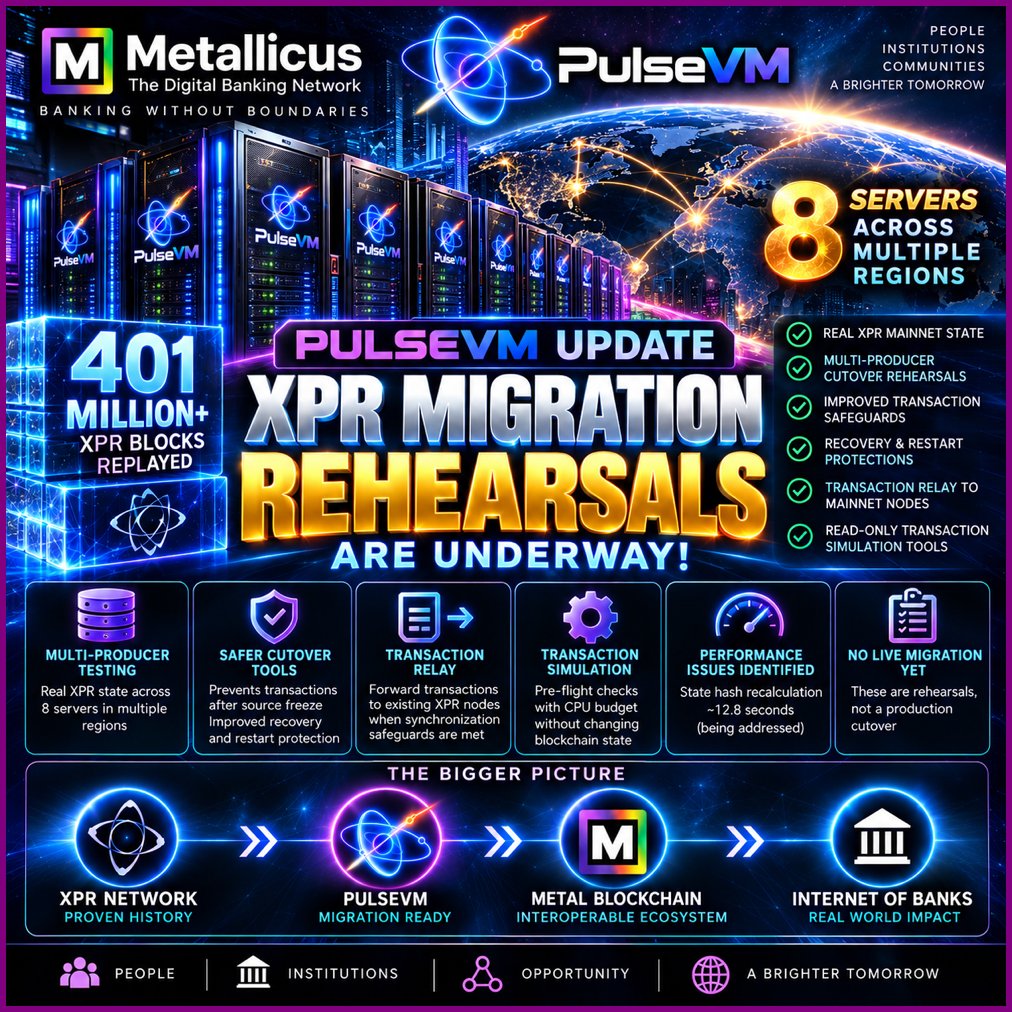
🚨 PULSEVM UPDATE — XPR MIGRATION REHEARSALS ARE UNDERWAY! 🚀 Another major milestone for the Metallicus ecosystem! ⚡ 8 servers across multiple regions ⚡ Real XPR Mainnet state ⚡ Multi-producer cutover rehearsals ⚡ Improved transaction safeguards ⚡ Recovery and restart protections ⚡ Transaction relay and simulation tools Following the release of PulseVM v1.0.0, development has moved beyond demonstrating blockchain compatibility. **The team is now rehearsing the actual migration process. And here's what excites me most. 👀 401 MILLION+ XPR blocks replayed. Now the focus is on safely transitioning a functioning blockchain network into the PulseVM architecture. Performance bottlenecks are still being addressed, and a live migration has NOT occurred. But this is how serious infrastructure gets built: test, identify weaknesses, strengthen, repeat. The bigger picture? 🏦 XPR Network → PulseVM → Metal Blockchain → Internet of Banks Piece by piece, Marshall Hayner's vision for interconnected digital banking infrastructure continues taking shape. We're watching the engineering, not just the announcements! 🔥 @XPRNetwork @MetalBlockchain 🔗 pulsevm.dev/network/updates #Metallicus #PulseVM #XPRNetwork #MetalBlockchain

Two critical PHP vulnerabilities have triggered an urgent cybersecurity response. Explore what happened, why digital infrastructure is at risk, how the threat connects to Web3, and what organizations can do to protect their systems and communities. x.com/i/article/2113…
🚨 WEBSITE OWNERS: A CRITICAL CYBERSECURITY WARNING Your website may look perfectly normal while the technology behind it is vulnerable. A major security emergency called PHP2Shell has exposed two critical vulnerabilities in PHP, the programming language powering millions of websites, including WordPress platforms. ⚠️ Both vulnerabilities carry a critical 9.2 security rating and could allow attackers to compromise vulnerable servers without logging in. Emergency patches were released October 21, 2026. If you own a business website, take action today: ✅ Contact your hosting provider and confirm your PHP installation is patched. ✅ Back up your website and important business data. ✅ Update WordPress, plugins, and themes. ✅ Review your website for unusual activity. ✅ Check your website's security and performance. Remember: updating WordPress alone does not fix a vulnerable PHP server. Your website is your digital storefront. Protect it like your business depends on it — because it does. Trenia Today | Marketing • AI • Digital Business Strategy 🌐 trenia.today #PHP2Shell #CyberSecurity #WordPress #SmallBusiness #WebsiteSecurity #TreniaToday

🚀 BUILDERS OF THE XPR NETWORK™ | MORE THAN AN NFT COLLECTION What happens after you collect a BUILDERS Genesis Art NFT? Your journey doesn't have to end with ownership. BUILDERS is a creative Web3 ecosystem built on the XPR Network, connecting nine founding archetypes, digital art, original music, cinematic films, community participation, and our ecosystem token, $BLDR. Here's how it works: 🎨 1. COLLECT GENESIS ART Our Genesis Art Collection features nine founding archetypes representing the people who help build Web3: Builder, Developer, Validator, Teacher, Creator, Trader, Dreamer, Collector, and Explorer. Each NFT is a digital collectible representing one of these roles in the BUILDERS universe. 🔒 2. STAKE YOUR NFT ON VIBRR Eligible Genesis Art NFTs can be locked through Vibrr NFT Staking to earn $BLDR rewards. Current base rate: 1,000 BLDR per NFT per day before multipliers. • 1-week lock: 1x • 1-month lock: 1.5x • Qualifying Vibrr activity: +25% bonus The longer lock offers a higher multiplier, but your NFT remains committed for the selected period. 🌟 3. BUILD YOUR PARTICIPATION LEVEL The staking program also features progression milestones: 🏗️ Builder — 7 days 💡 Innovator — 14 days 🌟 Visionary — 30 days These levels recognize participation milestones. Review the staking platform for current qualification rules. 🪙 4. UNDERSTAND $BLDR $BLDR is the BUILDERS ecosystem token. It connects our creative collections with participation and reward opportunities. NFT staking rewards are distributed in $BLDR, not guaranteed cash returns. Token prices can fluctuate. 🎁 5. MONTHLY NFT HOLDER REWARDS Beginning NOVEMBER 1, 2026, eligible NFT holders can participate in a separate monthly BUILDERS rewards claim through NFT Claim Hub. IMPORTANT: This is NOT Vibrr NFT Staking. These are two different programs with separate requirements. 🔗 EXPLORE THE ECOSYSTEM 🎨 Genesis Art: vibrr.ai/vibrr-market/c… 🔒 NFT Staking: vibrr.ai/nft-staking/3 🪙 $BLDR: vibrr.ai/dex/token/140 🎁 Monthly Claim Hub: nftclaimhub.io COLLECT. STAKE. EARN. PARTICIPATE. CLAIM. Together We Build What’s Next.™ #BUILDERS #BLDR #XPRNetwork #Vibrr #NFTStaking

🚨 WEB3 SECURITY ALERT: THE INTERNET'S FOUNDATION IS UNDER PRESSURE Blockchain technology is built on decentralization. But the websites, APIs, dashboards, and applications connecting people to Web3 still depend on traditional internet infrastructure. And that infrastructure is facing a critical security threat. PHP2Shell — CVE-2026-109618 and CVE-2026-109619 — has exposed serious vulnerabilities in PHP, with both receiving critical CVSS 9.2 ratings. Emergency patches were released October 21, 2026. ⚠️ What does this mean for Web3 builders? 🔹 Developers must audit the security of their web applications and supporting infrastructure. 🔹 Exchanges and platforms must protect vulnerable backend services. 🔹 Validators and node operators should examine any PHP-powered management tools or dashboards. 🔹 Communities must stay alert to phishing, fraudulent announcements, and compromised websites. A vulnerability in a website does not automatically mean the underlying blockchain has been compromised. But it reminds us that decentralization does not eliminate infrastructure risk. THE FUTURE OF WEB3 MUST BE BUILT ON SECURITY, TRANSPARENCY, AND RESILIENCE. BUILDERS OF THE XPR NETWORK™ Building the future. Protecting the ecosystem. #PHP2Shell #XPRNetwork #Web3Security #Blockchain #CyberSecurity #BuildersOfTheXPRNetwork

First you laugh, then you cry...

Cybersecurity AI models are being used to dig through huge codebases that no human has been able to fully audit for years. That's one reason we're seeing so many high CVEs, and until we patch most of these vulnerabilities, our feeds will continue to be filled with new exploits.

Ridoy Vibes @Ridoy9518
4K Followers 4K Following Follow to Follow ✪ Grow Our Community ✪ Ridoy !! Vibes
Sweep(Private) @Oxsweep12
1K Followers 2K Following Co-Founder @GlydeGG | Programmable Money & Al Dubai 🇦🇪 | Contact me here: https://t.co/6RHd9Z6Trv

.pro dev @dotprodev
180 Followers 1K Following building dev tools that don't suck 6 products. all free to start. shipping fast, learning in public.
maheerxm @maheerxm
632 Followers 1K Following Tutti platform Ai & Tech creator i break down Ai agents,tools and open_sourece Business audience USA+UK+china and others open to brand partnerships
Briar @Briarery
456 Followers 491 Following soft girl energy, chronic overthinker & morning yoga addict


Dillor⚛️ @DillonOrmsby
873 Followers 2K Following ⚛️ I collect NFTs and know things #GodWins (XRP🤝XPR)
marko.xpr Ⓜ️ SNIP... @MarkoBandis
3K Followers 2K Following https://t.co/1n8zv0rs6g /https://t.co/Sgo7Dbbl89 / https://t.co/GPna8BCVRZ /https://t.co/6UUEhpiVON /https://t.co/wI6XFb3Scx
ℙrotonℙunk @ProtonPunk
3K Followers 584 Following • @CypherGangNFT Founder • @CYPHRMarket NFT Marketplace • @PulsedApp 🔮 • @CypherBrawls P2E Game • @CYPHRC01N Ecosystem Token • $XPR veteran since 2021
Noorullah Jamakzai @itzSaasified
2K Followers 2K Following https://t.co/Y63JN4Qxe8 | 25k mrr https://t.co/TNu4jkc3v9 | $600 mrr Builder, marketer - making outbound easy
CYPHR.Market @CYPHRMarket
256 Followers 85 Following @XPRNetwork NFT Marketplace The NFT marketplace that rewards you for using it Built by the @CypherGangNFT Team
jersey @JerseyTDBN
2K Followers 1K Following ⚛️ @MetallicusTDBN #TDBN $XPR $LOAN $METAL $MTL $XMD ⚛️
Snipling @Sniplingxpr
115 Followers 176 Following SimpleDex Dev of Snipling $snip #Ksto core team member

Evens kate @Mrthankyoug6m
15 Followers 183 Following Hello everyone, this is Evan kate I'm here to help people as my father did you can inbox me
Existentialism @RWDailyBuzz
3K Followers 6K Following Fun. Curiosity. Tips. History. Belief. Hard questions.
Guiding Node @Guidingnode
642 Followers 990 Following Co-CEO of Keep Snipping LLC $KSTO Dev $HEAL Dev ⚛️Ⓜ️

PROTONBOY 🍓💨�... @TheXmen2025
207 Followers 401 Following ⚛ $HAYNER on https://t.co/fPnF3hAp9W ⚛ $ZION on https://t.co/fPnF3hAp9W ⚛ $FEN on https://t.co/fPnF3hAp9W SnipAi Music Artist on https://t.co/vlRfizNTfc Fuego Baila 🔥

LBUG🐞TDBN @tat2ude11
476 Followers 375 Following Small signs.🐞Certain fate. https://t.co/xVfVOQGWwV 🚨Node ID: LBUG🐞XBUG🚨 💥 XBUG Rewards💥

Meme M 🪙 ⚛️�... @Mr_g_spot954
1K Followers 1K Following Web3 is our future. ⚛️💯🚀🚀🚀 @XPRNetwork @MetallicusTDBN @LOAN_Protocol @MetalBlockchain @Metal_L2 @MetalPaysMe @MetalXApp @WebAuthWallet @MetalDollarXMD
Vasokol @lunarpuff735
2 Followers 548 Following
ExpiureSecret6849 @expiuresecret_X
743 Followers 916 Following AI + Web3 Thinker | Daily Qs in Collective AI on Vibr| XPR & future finance | Asking questions others fear | SNIPS – sharp cuts

Trenia Today @Trenia_Today
1K Followers 6K Following Marketing Strategist | Branding & AI Creative Studio | Websites, AI Films & Digital Campaigns | Web3 Marketing | Founder, Trenia Today
⚖️GEN @GENOYZALT
651 Followers 609 Following COMMUNITY GROWTH SPECIALIST || COMMUNITY MANAGER || MODERATOR || HEAD RAIDER || WEB3 WRITER || OPEN FOR COLLABORATION
Casimir von Falkenhay... @Falkenhayn_
3K Followers 12 Following Private investor | Industrial holdings & global markets Capital, geopolitics and the occasional indiscretion.
⚖️GEN @GENOYZALT
651 Followers 609 Following COMMUNITY GROWTH SPECIALIST || COMMUNITY MANAGER || MODERATOR || HEAD RAIDER || WEB3 WRITER || OPEN FOR COLLABORATION
ExpiureSecret6849 @expiuresecret_X
743 Followers 916 Following AI + Web3 Thinker | Daily Qs in Collective AI on Vibr| XPR & future finance | Asking questions others fear | SNIPS – sharp cuts
Meme M 🪙 ⚛️�... @Mr_g_spot954
1K Followers 1K Following Web3 is our future. ⚛️💯🚀🚀🚀 @XPRNetwork @MetallicusTDBN @LOAN_Protocol @MetalBlockchain @Metal_L2 @MetalPaysMe @MetalXApp @WebAuthWallet @MetalDollarXMD
jersey @JerseyTDBN
2K Followers 1K Following ⚛️ @MetallicusTDBN #TDBN $XPR $LOAN $METAL $MTL $XMD ⚛️
Noorullah Jamakzai @itzSaasified
2K Followers 2K Following https://t.co/Y63JN4Qxe8 | 25k mrr https://t.co/TNu4jkc3v9 | $600 mrr Builder, marketer - making outbound easy
Stern Drew @SternDrewCrypto
70K Followers 0 Following 10+ years in commodities. Data-driven. RTs ≠ endorsements.
Sweep @0xSweep
252K Followers 11K Following Co-Founder @GlydeGG | Programmable Money & AI | Dubai 🇦🇪 | Contact me here: https://t.co/ZoZklGlttF
Metal Monsters @METALM0NSTERS
294 Followers 194 Following $MONSTER Born in the $METAL & $XPR trenches. Metal Validator Node: https://t.co/ZtMen8XTjz
Diligent Plane @DiligentPlane
79K Followers 578 Following Turned 50k into $1M+ in one year. No options Famous on @Reddit WSB with 23M+ views Your mom’s favorite trader
David Harris @Davidaiuwhy
42K Followers 4 Following Senior Stock Analyst & Investment Strategist | NYC‑based | 25+ yrs at Morgan Stanley & Goldman Sachs | Free insights, no paywall
XPR Q-Tech @valentinTDBN
836 Followers 165 Following 🚀 Building on XPR Ecosystem 💜 Passion projects: @MetallicusTDBN | @MetalBlockchain | @XPRNetwork @Metal_L2 | @MetalXApp | @webauthwallet | @metalpaysme
Sean Sweeney @crossfitcowboy1
1K Followers 2K Following
bloxprod ⚛️ @bloxprodio
952 Followers 624 Following @𝗫𝗣𝗥𝗡𝗲𝘁𝘄𝗼𝗿𝗸 𝗕𝗹𝗼𝗰𝗸 𝗣𝗿𝗼𝗱𝘂𝗰𝗲𝗿 ⚛️ strength in unity, growth in connectivity ⚛️ Thanks for your support! ⚛️ $XPR $METAL $LOAN


Diogo Almeida @CompleteSkeptic
157K Followers 79 Following Sane + 🌶️ takes in an insane AI world... AI capabilities researcher: co-created RLHF/ChatGPT @ @openai now trying to right the wrong 🤭 (ceo @typesafeai)
Tyler Winklevoss @tyler
1.1M Followers 4K Following Co-Founder @gemini, @cypherpunk, @winklevosscap Vocals @marsjunction
Yuchen Jin @Yuchenj_UW
307K Followers 881 Following Cooking fun AI systems & products @databricks. Prev: co-founder & CTO @ Hyperbolic, OctoAI (acquired by @nvidia) Apache TVM, PhD @ University of Washington.


Alvosec ⚛️ @alvosec
6K Followers 3K Following 🕵 Web3 security advisor 🛡 Certified F-Secure partner ⚛ BP and member of consortium on @XPRNetwork. 🛡 Web3 DNS https://t.co/KXNdEWTu7R
FTMO Futures @FTMO_Futures
5K Followers 0 Following 🟢 The FTMO Standard Now in Futures | ⚖️ PT to DD Ratio as Low as 1:1 | 📈 90/10 Payout Ratio | 🛡️ EOD Trailing | 🖥️ Top Platforms
XPR data ⚛ @xpr_data
944 Followers 75 Following ⚛ Block Producer. Dedicated to the growth of the #XPRNetwork. We deliver transparent data and analysis to empower users and developers
Lord Marshal @MTFockers
437 Followers 352 Following “Don’t work for money, let money work for you” ⚛️
DDPCrypto @DDPCrypto85
1K Followers 510 Following Christian (Jesus Christ is my Lord and Saviour) Ron Paul styled Libertarian with a heavy dose of Nationalism. Hodl'r of XRP, Metal, XPR, ETH &Sol.

Cryptoleer ⚛️Ⓜ�... @cryptoleer
3K Followers 978 Following Graveyard Shift Manager at @MetalMiniMart Ⓜ $XPR | $LOAN | $METAL | $ANKR | $DGB | $LTC
Papa Tony - TDBN Enfo... @GettrFatterTony
4K Followers 2K Following Community Gorilla bringing awareness to the @Metallicus ecosystem with the TDBN community Creator of #PAPA on https://t.co/IM8rZGYcys
Solvent_TDBN @solvent_TDBN
10K Followers 8K Following Always a student | https://t.co/sthyNYr6h1 future-proofing Credit Unions, banking FOR THE PEOPLE | learn the American System @PrometheanActn | my project https://t.co/AEcaMsyxud
MarshallCoin @Metalmarshill
839 Followers 384 Following MEME Coin on Simpledex Homage to Marshall Hayner FAN ACCOUNT UNAFFILIATED TO METALLICUS
Metal Client Services @metalhelpsme
4K Followers 20 Following 24 Hour Human Support for The Digital Banking Network by @MetallicusTDBN | Metal Pay | Metal X | Metal L2 | WebAuth | Metal Dollar | XPR Network
Alcor Exchange @alcorexchange
14K Followers 274 Following The first self-listing orderbook DEX. Providing the cheapest exchanges for EOS, WAX, TELOS, and XPR. Telegram: https://t.co/mTymR9tXPw
Tecknical Tuesday @TeckncalTuesday
710 Followers 398 Following DeFi Tools for Metallicus Lending | Insight → Analyze → Monitor → Manage risk https://t.co/ngabSNlIW4
Blue Hawk Legend @BlueHawkLegend
1K Followers 767 Following Watch Me on YOUTUBE!!! NOT FINANCIAL ADVICE!!! also IM NOT A DOCTOR! LIKE, Share and Subscribe!!! https://t.co/EpLWD65lvx
Cypress Demanincor @CDemanincor
49K Followers 2K Following -CEO CYPRX SUPERIOR TRADING 📈💻 SUPERIOR TRADING, RESEARCH, AND ANALYSIS 📊FOLLOW US ON YOUTUBE! ALL CYPRX LINKS IN BIO 👇
Morrígu66613 @AngelaLark66613
14K Followers 6K Following HellRaiser 😈 multiracial sarcastic DGAF nonreligious tenacious indica smoker👽 and lover of the 🌕 Voted for Kamala 💚Green Party💚 supports #smokefleet 😎💨
Gunjan @Lost_Nostalgic
71K Followers 5K Following all about Internet money. $kas $tao $qnt $troll $dog $snek $SI spx6900 🧲💹
straz1001 ⚛️ 🇦... @straz101
393 Followers 332 Following An old man once told me that I thought too much about life. He said to start living it instead. One day I might listen to his advice. https://t.co/RS4rxmu6K5
SHINEDU BABA 🎭 @ShineduBaba
740 Followers 361 Following 💬 Reply Guy | 📱 SMM | 📈 Engagement Strategist
marko.xpr Ⓜ️ SNIP... @MarkoBandis
3K Followers 2K Following https://t.co/1n8zv0rs6g /https://t.co/Sgo7Dbbl89 / https://t.co/GPna8BCVRZ /https://t.co/6UUEhpiVON /https://t.co/wI6XFb3Scx

Totalℙroton.XPR ⚛... @ProtonTotal
3K Followers 1K Following $XPR Vote TotalProton Block Producer $MTL $LOAN $METAL 👩👩👧👧⚛️ XPRNetwork family. TDBN
USD8.fi - Free defi i... @usd8_fi
625 Followers 338 Following A new stable coin doubles as free Defi protection + enforcement layer. Coming soon to Ethereum.
KalEl ⛓️🏦⚛�... @KalElTDBN
2K Followers 775 Following Fear No Hardship. $XPR $METAL $LOAN $MTL @MetallicusTDBN Work smarter, not harder. #movetoMETAL #TDBN
protonnz ⚛️ @protonnz
5K Followers 993 Following New Zealand's @XPRNetwork Block Producer by @paulgrey Creator of @SimpleDEXFun, @charliebot87 @XPRAgents and https://t.co/sQCkkzt0Vb Thanks for your support! $XPR
XPR Network Nation Ex... @1NationUnderXRP
7K Followers 418 Following Master Networker • UAV Pilot | $XRP ’16 | $XPR 23’ | $LOAN | Photography 🎩⚛️ God 🇺🇸 | @metalpaysme | @xprnetwork | @loan_protocol | @Metallicus | UCLA 🎓You might like


















