

-
Tweets95
-
Followers2K
-
Following8
-
Likes48

🚨 Do you understand what happened in the last 48 hours.. > PHP, the code behind 69% of all websites, got 2 holes rated 9.2 out of 10, and the US, the UK and Japan told site owners to patch or go OFFLINE.. 4 days after hackers had already started trying the flaw.. > Japan's Prime Minister posted the request late at night.. the Finance and Health ministries pulled pages, MUFG Bank and JR West went into emergency maintenance, and Onamae shut ALL Desktop Cloud plans after malware hit up to 26,739 customer servers.. > India's eMudhra was caught with 8 intermediate certificate keys so weak one of them was literally the number 4.. the 60,000,000+ certificates it has issued can't be trusted.. > GitLab disclosed a 10.0 severity hole in every version since 2014.. the maximum score there is.. > criminals were caught using a literal AI hacking tool on 1,200+ sites.. it broke into more than 100 companies including John Deere and Cummins.. > LiteLLM, an AI tool with about 23,000,000 downloads a week, was secretly poisoned with a password stealer.. the bad version sat on PyPI for about 2 hours.. > State Bank of India, the country's biggest bank, confirmed 3,897 customer records on the dark web.. > WIRED now calls the PHP flaw "broadly exploited".. nearly 55,000,000 web properties still run PHP.. every single government on this list told PHP site owners the same thing within the last 48 hours.. patch it or take it offline.. all of this.. 48 hours.. if you're not following me you're finding out about this 48 hours late from someone who read my post.. it's only getting crazier from here..

The internet is going into a LOCKDOWN. Hundreds of millions of websites are potentially at risk from cyberattacks. Governments, banks and major platforms have already taken their websites OFFLINE. Many are already calling it “Black October.” At the centre of the shutdowns is something most of us have never heard of, but use every day. PHP, the software behind roughly 7 in 10 websites, has two critical flaws that can let hackers break in without a password. Dubbed PHP2Shell, both are rated 9.2 out of 10 for severity. Details began circulating on Oct 20. Emergency fixes arrived the next day, but attackers were already moving. Cloudflare’s CEO says hacking attempts then jumped from thousands to MILLIONS within hours. Cybersecurity agencies across several countries are telling PHP site owners the same thing: Patch it now, or take it offline. Websites have gone dark worldwide, from government portals and hospitals to banks. CrowdStrike warns these attacks leave almost no trace, so some sites may not know if they’ve been hit. Around 2.6 MILLION internet-facing servers run PHP, potentially hosting hundreds of sites each. Over 1.1 million use older versions no longer receiving official PHP updates. Older installations may need an upgrade to a supported PHP version or a fix from their software provider. And patching does not remove a backdoor an attacker may already have planted. Cloudflare also says hackers are now tweaking their attacks to try to slip past its protections. But PHP isn’t the only security story unfolding. -Japan’s Onamae suspended ALL Desktop Cloud plans after malware was found on customer servers. -India’s eMudhra had 8 website-certificate keys so weak, one was literally the number “4”. -State Bank of India confirmed 3,897 customer records on the dark web. -Criminals used AI agents to break into 400+ Latin American banks. -Capcom confirmed a breach exposing 11.7 million email addresses. -GitLab disclosed a 10/10 severity flaw in versions going back to 2014. -LiteLLM removed a malware-containing release. Railway reported possible exposure of customer secrets. None of these has a confirmed link to PHP2Shell. We’re seeing separate breaches unfold together. The true number of incidents could take months to come out. The world is still on alert. Attacks are still coming.
How to build a legal AI bug-hunting workflow

‼️A German hacker known as "Martha Root" dressed as a pink Power Ranger and deleted a white supremacist dating website live onstage This happened during the recent CCC conference. Martha had infiltrated the site, ran her own AI chatbot to extract as much information from users as possible, and downloaded every profile. She also uncovered the owner of the site. She has published all of the data.
@WatcherGuru Do White Hat Hackers actually exist? Let's see.

@WatcherGuru This is the kind of hackers we like! Yay.

APRENDE A HACKEAR!!! Hay un catálogo de máquinas vulnerables, montadas a propósito, donde puedes practicar intrusión sin cometer ningún delito. Laboratorios gratis, entorno real. Y cuando te atascas, existen las soluciones escritas paso a paso.

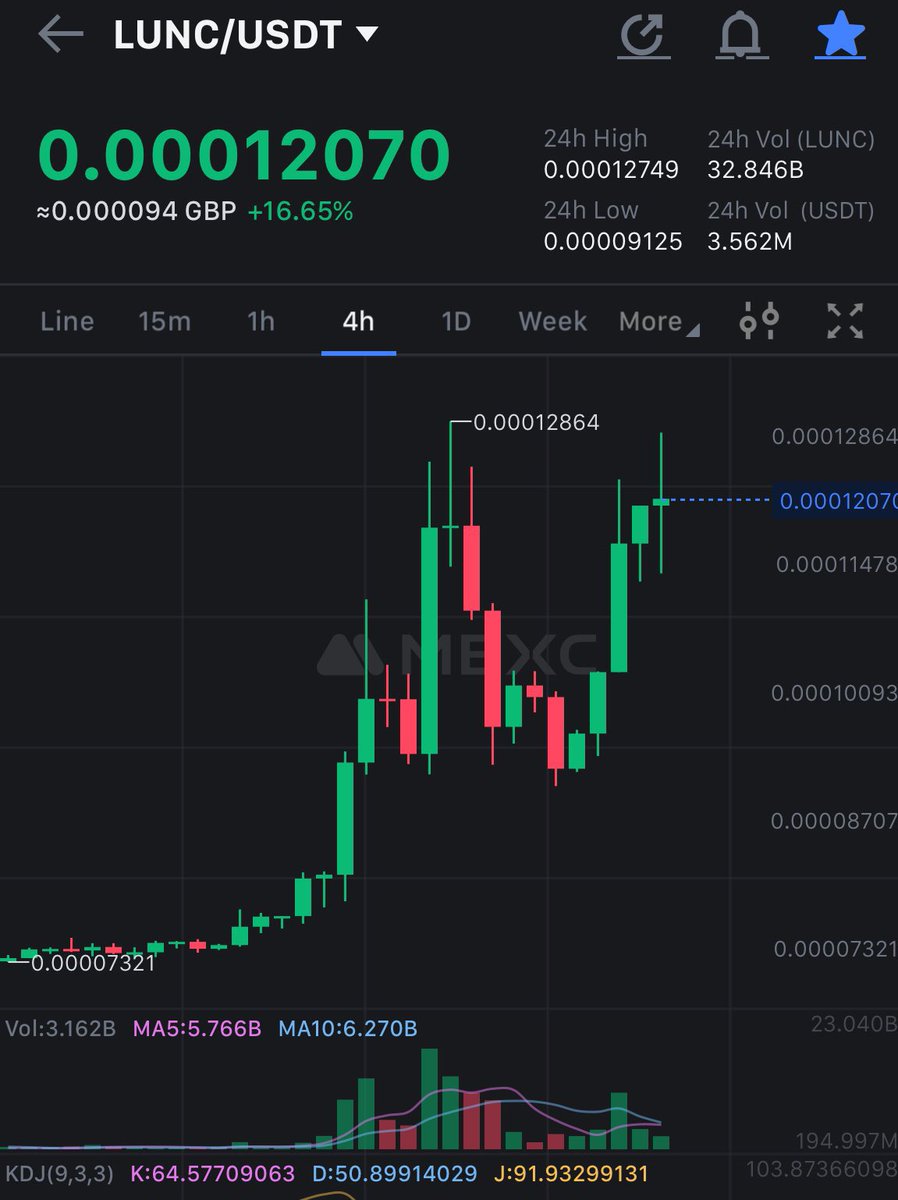
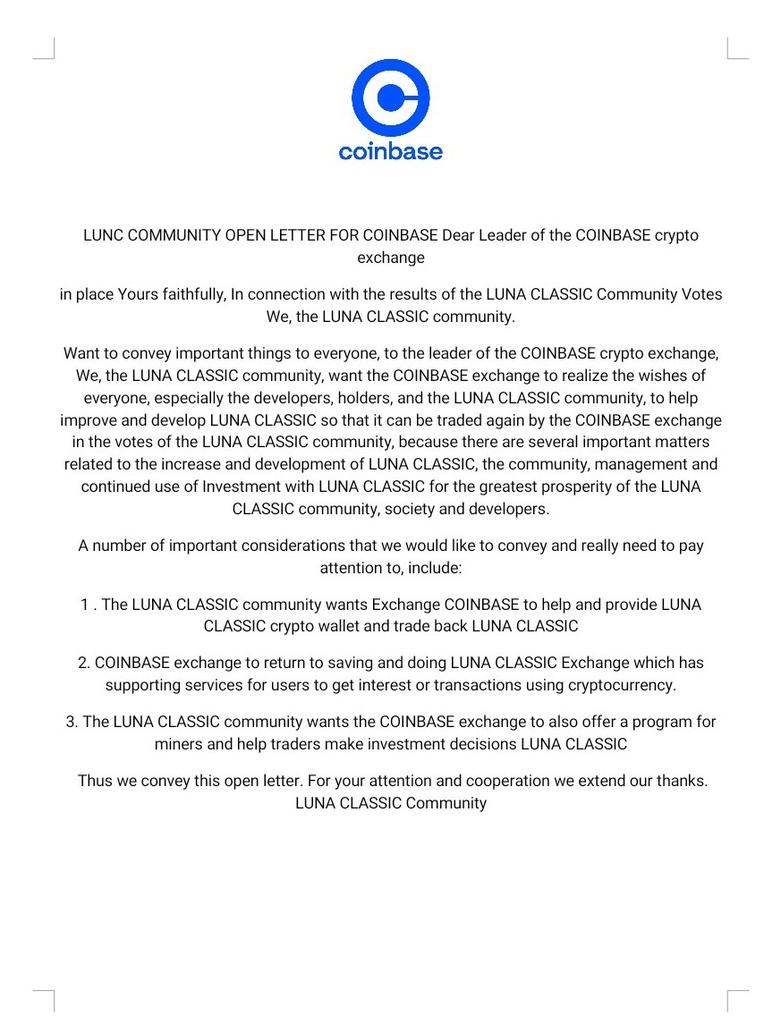
Hello @coinbaseSupport I would like to convey an open letter and voice from the LUNA CLASSIC community, Can @coinbase make what the community wants and hear their voices. Thank You #LUNC ✨ #HaileyLUNC ✨ $LUNC ✨
@BabyWhale69 Send us a dm, sorry about the issue you’re facing.

Are you looking to grow your portfolio with 0️⃣ fees? 😎 #OKX Bot Marketplace is a 360-degree user experience that allows you to select & duplicate top-performing strategy bots in 3 clicks 🤖 Trade easier and smarter today ⤵️

The only reason $DOGE is moving is because Elon, who didn’t say a word about it, has taken over Twitter. That’s crazy.
Good day #LUNC 🌒 🌗 🌗 🌖 🌖 🌕🌕 🌒 🌗 🌗 🌖🌖 🌖 🌕 🌒 🌗 🌗 🌖 🌖🌖 🌕 🌒🌒🌒 🌗🌗 🌖 🌖 🌕🌕 #LUNC ❤️ #LUNACLASSIC 🔥🔥🔥

Update on Deposit and Withdrawal Fees for $LUNC and $USTC on Terra Classic #LUNC Network (2022-09-27). binance.com/en/support/ann…

LUNC Burn Flip @luncburnflip
266 Followers 447 Following Flip a coin 🪙 BURN LUNC 🔥 How to play: https://t.co/BJv7kkiSJA

Charlotte @Charlotteldw3
22 Followers 357 Following

wizard of OZ @Justadude5598
152 Followers 643 Following abracadabra I am a born shaman/sjaman a 🧙/🐲/🌞🏔👍


Mahaz @Mahazkakar12
4 Followers 24 Following
keng ninj @NinjKeng26863
46 Followers 321 Following
@AryanBajalan @AryanBajalan11
35 Followers 167 Following

Nuy12345 @suree555556
35 Followers 712 Following
BeaSbay @Sabuy639
31 Followers 299 Following
YamilTartak @YamilTartak
666 Followers 2K Following 37 years as a Real Estate Broker. Crypto Fanatic. 🇱🇧 🇵🇷 🇺🇸
Muhammad Na'im Bin Mo... @na_saidin84442
0 Followers 3 Following
Mark Anthony @MarkAngel7883
24 Followers 69 Following
Milot Emmanuel @milot_emma73168
21 Followers 233 Following
Chai @ChaiChai1980
34 Followers 152 Following
断翅的鹰 @ChiDe34261
0 Followers 35 Following
Olorunmo Jonathan @OLORUNMO_Joe
233 Followers 1K Following Jesus, Finance,Consultant , Cryptocurrency - Accountant, Believer @SMCDAO



All_LUNC @All_LUNC
25 Followers 358 Following
Vincenz Tansella @VincenzTansella
0 Followers 20 Following
RyuAJJi @RyuAJjii
1 Followers 13 Following
Firas Marouani @Marouani2Firas
41 Followers 325 Following

Santosh Kumar @kumar_sant40466
9 Followers 264 Following सत्य की राह पर चलना चाहते हैं इस पेज को फॉलो करें,🙏🔱🚩
hocco. @mdsaddam1000100
489 Followers 598 Following
Wolfmeister @SeanGib55754356
234 Followers 663 Following
Corvette @CorvetteC8Z06
910 Followers 1K Following Extreme Sports Participant/Enthusiast & Crypto Dude. #LUNC #LUNCdash #TerraLunaClassic #SHIBAINU #XRP #BTC #ETH #DevvE #Corvette #Crypto #NFT #SELE #INDX #JURIS
top update 92 @Fadil_9258805
3 Followers 72 Following
Meh @Pamp_it_again
106 Followers 1K Following
Wizard @Wizard1Br
207 Followers 633 Following Internet Marketer,Personal&Business Development Coach,Martial Artist,Singer/Songwriter/Guitarist.


hotmemelon @hotmemelon93387
8 Followers 139 Following Crypto Blockchain Internet technolory and RAG SI
sushil kashyap @sushilkashyap8
3K Followers 5K Following Nature lover, current events, sanatani, crypto enthusiast, travel& tourism
Faisal khan @Faisalk69108393
20 Followers 109 Following
Sai Kiran Reddy @KIRANSAI943
75 Followers 217 Following
The_lost_wanderer @Maneendravarma1
91 Followers 943 Following 2AM person, trader📈📊 and a traveler for life✌🐼🏃

monty @MSain82076
4 Followers 87 Following
pritesh dedhia @pritesshah9
5 Followers 131 Following
Ryan Reserva @ivancapp90
779 Followers 6K Following
Aurelio Jr @Aurelio26595154
7 Followers 37 Following

Dark Web Informer @DarkWebInformer
250K Followers 96 Following One guy. Global cybercrime. Tracked so you don't have to. Ransomware, data breaches, dark web activity, darknet markets, IOCs & emerging threats. Stay informed!
The Epoch Times @EpochTimes
844K Followers 76 Following Clarity for Independent Thinkers Download our app ➡️ https://t.co/YmpowM2rWt
ZachXBT @zachxbt
1.1M Followers 2K Following Scam survivor turned 2D investigator, Advisor @paradigm
Bitcoin Core Project @bitcoincoreorg
187K Followers 0 Following The Official Bitcoin Core Feed (RT/Fav/Follow does not imply endorsement)

The Hacker @theprocracker
10K Followers 3 Following Growth hacking is a mindset rather than a toolset
Watcher.Guru @WatcherGuru
4.9M Followers 3 Following Watcher Guru gives you unparalleled, unbiased coverage of all-things crypto & finance in real-time | Posts Are Not Financial Advice | @BTCPriceTrends for United States
You might like


