-
Tweets87
-
Followers8
-
Following50
-
Likes1
#HackTheBox write up for debugger unchained, a web app challenge from the recent HTB business CTF! github.com/sentrium-secur…
Check out our latest blog post on #Terraform security best practices. sentrium.co.uk/labs/terraform…
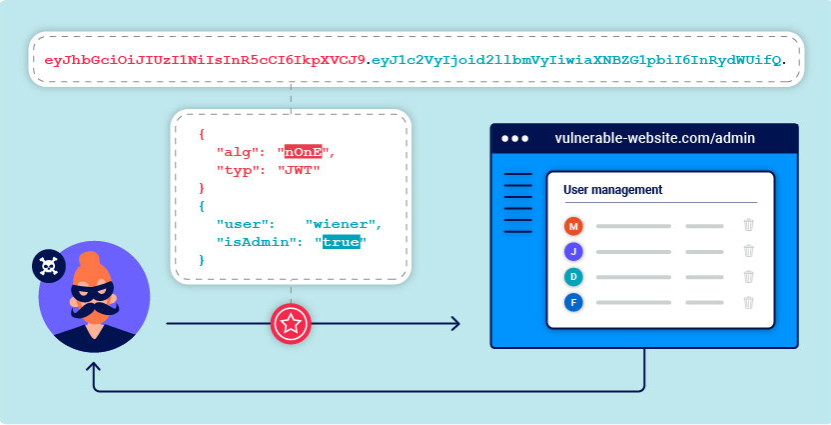
We've launched a brand new topic with eight new labs for you to get stuck into! The topic will look at how design issues, and flawed handling of JSON web tokens (JWTs), can leave websites vulnerable to a variety of high-severity attacks. portswigger.net/web-security/j…
Our latest article on the remediation of #Follina and a simple PowerShell script anyone can use to apply the workaround. sentrium.co.uk/labs/preventin…
WordPress patched an Object Injection #vulnerability (CVE-2022-21663) in its core 3 years after it was reported. Read details here: blog.sonarsource.com/wordpress-obje… #infosec
CISA, the U.S. #cybersecurity agency, has ordered all federal agencies to immediately and mandatorily secure their systems against an actively exploited #vulnerability (CVE-2022-21882) in #Microsoft Windows operating systems. Details: thehackernews.com/2022/02/cisa-o… #infosec #technews
New blog post: We identified a large-scale, multi-phase phishing campaign that first compromised mailboxes and implemented email rules. Attackers then abused one org's lack of MFA to register an attacker-controlled device and propagate malicious messages. msft.it/6010ZfeZG
A 12-year-old #vulnerability (CVE-2021-4034) has been discovered in the Polkit utility that could allow unprivileged attackers to gain root access to targeted #Linux systems. Details: thehackernews.com/2022/01/12-yea… #infosec #cybersecurity #hacking
While monitoring threats related to the Log4j 2 vulnerabilities, we saw attacks being propagated via an input validation flaw in the SolarWinds Serv-U software. We reported our discovery to SolarWinds, and security updates have been released. More info: msft.it/6013ZIZzF
Microsoft identified a unique destructive malware operated by an actor tracked as DEV-0586 targeting Ukrainian organizations. Observed activity, TTPs, and IOCs shared in this new MSTIC blog. We'll update the blog as our investigation unfolds. msft.it/6017ZQ8jH
Burp Suite 2021.12.1 released to the Stable channel, with multi-host Intruder attacks, customizable Inspector panel, and a dedicated version for Mac M1 machines. portswigger.net/burp/releases/…
We have observed a China-based ransomware operator that we’re tracking as DEV-0401 exploiting the CVE-2021-44228 vulnerability in Log4j 2 (aka #log4shell) targeting internet-facing systems running VMWare Horizon. microsoft.com/security/blog/…
#Microsoft warns of continued attempts by nation-state adversaries and commodity attackers to exploit vulnerabilities in the open source logging framework #Log4j to install #malware on vulnerable systems. Read: thehackernews.com/2022/01/micros… #infosec
URGENT: Apache Foundation has issued a new patch (CVE-2021-45046) for #Log4j utility after the previous patch for the recently disclosed #Log4Shell exploit (CVE-2021-44228) was deemed incomplete in certain non-default configurations. Details: thehackernews.com/2021/12/second… #infosec
We updated our blog on the CVE-2021-44228 Log4j 2 vulnerability with details about ransomware attacks on non-Microsoft hosted Minecraft servers, as well as additional product guidance, including Threat and Vulnerability Management msft.it/6015ZzTUV
You can now scan for Log4Shell (CVE-2021-44228) using Burp Suite Pro or Enterprise Edition by installing @SilentSignalHU’s Log4Shell Scanner from the BApp Store. portswigger.net/bappstore/b011…

RCE 0-day exploit found in log4j, a popular Java logging package lunasec.io/docs/blog/log4…
Grafana urges web devs to update following path traversal bug disclosure portswigger.net/daily-swig/gra…
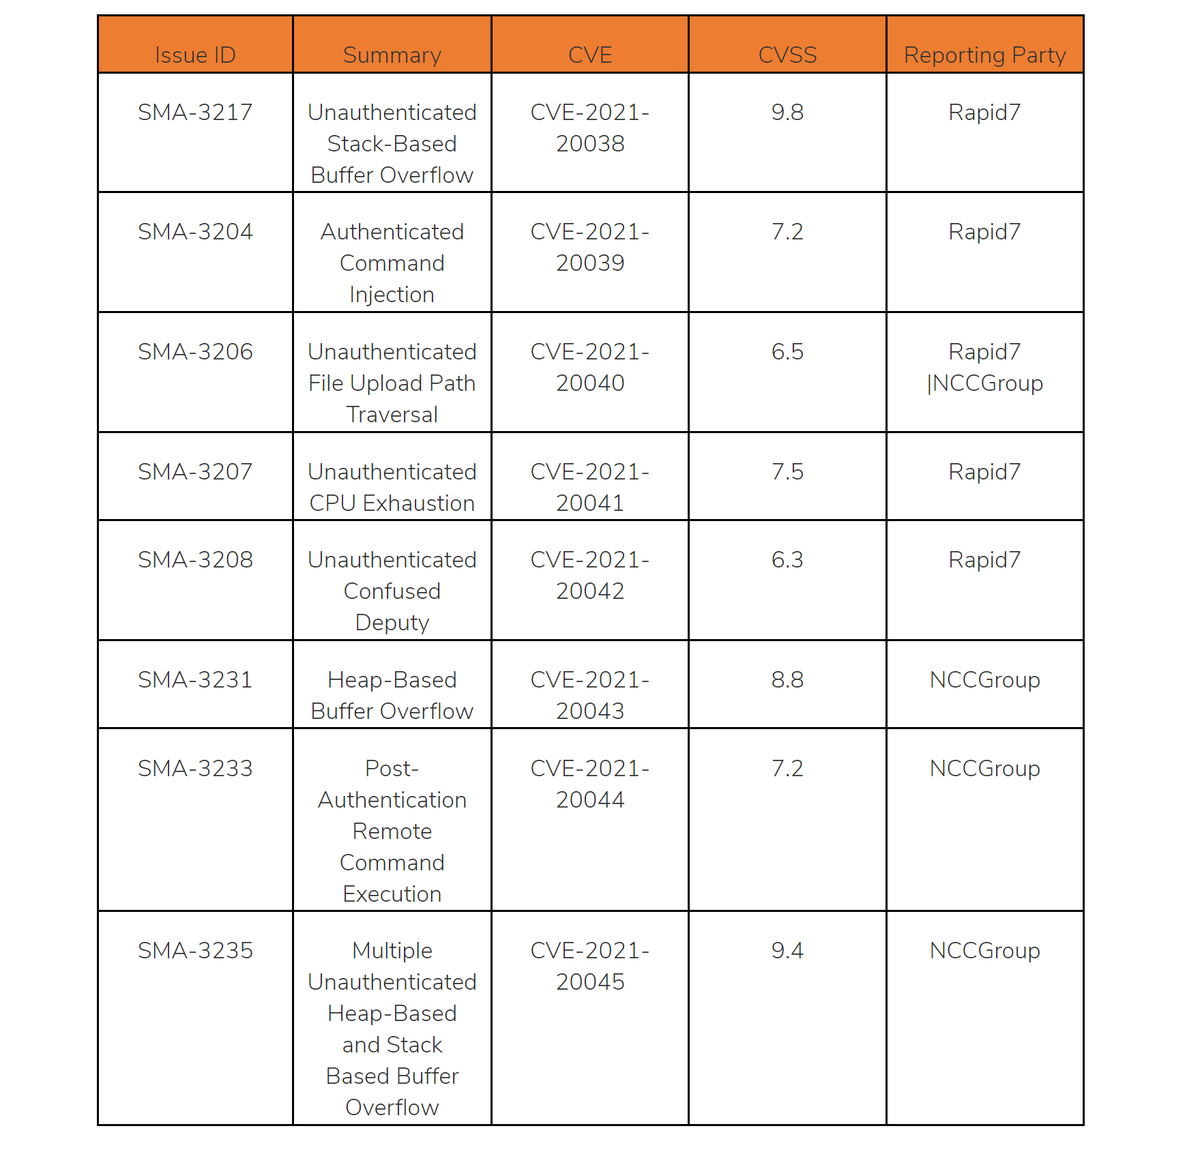
SonicWall urges customers to immediately patch/update their SMA 100 series appliances to the latest version in order to prevent exploitation of newly discovered multiple critical & high-severity security vulnerabilities. Details: thehackernews.com/2021/12/sonicw… #infosec #cybersecurity
Critical vulnerabilities in open source forum software NodeBB could lead to RCE portswigger.net/daily-swig/cri…

OpsMatters @opsmatters_uk
3K Followers 3K Following The Place Where Modern Operations & Technology Come Together #OpsMatters #OpsBuzz #TeamRelated #SecuritySenses #SystemsDigest
51pwn @Hktalent3135773
916 Followers 4K Following #infosec #RCE #poc #exploit #0day #zero-day #ZDI #Cybersecurity #payload #CVE-2022- #0-Dau #NDay #N-Day
IAVURH - Personal Rob... @IAVURH_Robot
18 Followers 671 Following Personal Robot Create Music Blog Images Video Everything and more.
Feidhlimdh @Feidhlimdh
18 Followers 316 Following
Adam King @adamk1ng
27 Followers 26 Following

James Drew @semajwerd
3 Followers 24 Following
InfoSec Community @InfoSecComm
57K Followers 634 Following Largest InfoSec publication with 80,000+ followers and 3M+ monthly views.
The Hacker News @TheHackersNews
2.4M Followers 2K Following The #1 trusted source for cybersecurity news, insights, and analysis — built for defenders and trusted by decision-makers.
SC Media @SCMagazine
119K Followers 2K Following The official Twitter feed for all things IT security. A CyberRisk Alliance Resource.
Sergiu Gatlan @serghei
9K Followers 2K Following Cybersecurity/tech reporter @BleepinComputer Signal: serghei.33
Follow CISA's account... @cyber
293K Followers 113 Following This account is not active or monitored. Follow @CISAgov and @CISACyber for the latest updates.
The Daily Swig @DailySwig
11K Followers 390 Following Web security news and views. The latest on bug bounty programs, technical research, hacking tools, and more. DMs open for tips.
Marcus Murray @MarcusSwede
2K Followers 114 Following Security Specialist - Windows Focus. MVP Enterprise Security. Security Team Manager Truesec
Fabio Viggiani @fabio_viggiani
4K Followers 978 Following CTO / Red Team / Blue Team / Incident Response / Threat Intel / Speaker / at @Truesec
Microsoft Security Re... @msftsecresponse
145K Followers 232 Following We are the Microsoft Security Response Center. To report security vulnerabilities or abuse in Microsoft products, visit https://t.co/kxEbdfMny1.
Nmap Project @nmap
137K Followers 457 Following Free and open source tool for network discovery, admin, and security auditing. Our tweetmaster is Gordon "Fyodor" Lyon. We're also on FB: https://t.co/RVkxWNikvW
TheMayor - Joe Helle @joehelle
28K Followers 54 Following U.S. Army Iraq & Afghanistan Veteran | Former Mayor | Penetration Tester | PPG Trike Pilot | Occasional Political Commentary
John Hammond @_JohnHammond
327K Followers 3K Following Cybersecurity Researcher @HuntressLabs Just Hacking Training @JustHackingHQ w/ @ethicalhacker https://t.co/UtsNJiyQtS && https://t.co/narO3sz7y6
Trellix @Trellix
240K Followers 1K Following Mission-critical security for intelligence-led cyber resilience
Rapid7 @rapid7
126K Followers 3K Following Rapid7 is a leader in AI-powered managed cybersecurity operations. 11,500+ customers utilize Rapid7 to disrupt attackers and advance their cyber resilience.
0xdf @0xdf_
27K Followers 473 Following AI Cybersecurity @ Anthropic Potentially a legit security researcher he/him https://t.co/GCcLVlmdQK https://t.co/uQWVpw4nft 0xdf on discord
BeEF @beefproject
22K Followers 16 Following BeEF is pioneering techniques that provide practical client side attack vectors. Created & led by @WadeAlcorn. Tweets by dev team.
Ben Sadeghipour @NahamSec
253K Followers 1K Following Cofounder @hackinghub_io | Advisor @CaidoIO. I hack companies and make content about it. #NahamCon organizer. ex @hacker0x01🇮🇷
Burp Suite @Burp_Suite
141K Followers 14 Following Burp Suite is the leading software for web security testing.

b33f | 🇺🇦✊ @FuzzySec
34K Followers 1K Following 意志 / mobile research @ ▓▓▓▓▓ / Team 501 / ex IBM Capability Lead & FireEye TORE / I rewrite pointers and read memory / AI Psychoanalyst / BHUSA Review Board
HackerOne @Hacker0x01
343K Followers 3K Following HackerOne makes security continuous. We unite AI and human insight through a unified platform to expose risk and eliminate it.
Web Security Academy @WebSecAcademy
145K Followers 36 Following Free web security training from @PortSwigger
Hack The Box @hackthebox_eu
251K Followers 227 Following Cyber Mastery: Community Inspired. Enterprise Trusted.
STÖK ✌️ @stokfredrik
139K Followers 1K Following Hi.. im that hacker / creative that your friends told you about.,
Marcello @byt3bl33d3r
30K Followers 991 Following CyBeRsEcUrItY | Not afraid to put down with some THICC malware on disk | AI Research @PaloAltoNtwks | former purple team | Ex @spacex
Exploit Database @ExploitDB
216K Followers 9 Following The Exploit Database – ultimate archive of #Exploits, #Shellcodes & Security #Papers/#eZines
Microsoft Threat Inte... @MsftSecIntel
197K Followers 994 Following We are Microsoft's global network of security experts. Follow for security research and threat intelligence.
Cybersecurity and Inf... @CISAgov
328K Followers 106 Following America's Cyber Defense Agency and National Coordinator for Critical Infrastructure Security & Resilience. Likes, reshares, follows ≠ endorsements.
Mobile Security @mobilesecurity_
31K Followers 1K Following Mobile Security ✌🏻 #MobileSecurity #AndroidSecurity #iOSsecurity
/r/netsec @_r_netsec
34K Followers 0 Following Follow for new posts submitted to the netsec subreddit. Unofficial.
James Forshaw @tiraniddo
49K Followers 336 Following Security researcher in Google Project Zero. Author of Attacking Network Protocols. Tweets are my own etc. Mastodon: @[email protected]

Alex Ionescu @aionescu
48K Followers 2K Following Chief Technical Innovation Officer @crowdstrike. Windows Internals author and trainer. He/Him. RTs are not endorsements, opinions are my own.
Maddie Stone @maddiestone
62K Followers 802 Following Security Researcher. Previously Google Project Zero and TAG | 0days all day. Love all things bytes, assembly, and glitter. she/her.
James Kettle @albinowax
85K Followers 106 Following Director of Research at @PortSwigger aka @Burp_Suite. Find my research, tools & contact details at https://t.co/vP6UbGmvl3
chompie @chompie1337
90K Followers 1K Following hacker, exploit developer/weird machine mechanic head of X-Force Offensive Research (XOR) @IBM
Project Zero Bugs @ProjectZeroBugs
37K Followers 0 Following A bot that posts the latest blog posts and disclosures from Google's Project Zero
Schneier Blog @schneierblog
148K Followers 0 Following Bruce Schneier is an internationally renowned security technologist and author. Described by The Economist as a "security guru"
Peter Kruse | Cybercr... @peterkruse
13K Followers 841 Following Peter Kruse is a cybersecurity researcher. Co-founder of CSIS Security Group, Kruse Industries, SIE-Europe & Heimdal. CARO member. Back as a Malware analyst.
ippsec @ippsec
125K Followers 373 Following
Mitja Kolsek @mkolsek
4K Followers 777 Following CEO of ACROS Security; Co-founder of 0patch (https://t.co/XQ9EYMnQYX) Bluesky: https://t.co/HhsFBafHK0 Mastodon: @[email protected]
Will Schroeder @harmj0y
50K Followers 975 Following Researcher @SpecterOps. Coding towards chaotic good while living on the decision boundary.
Threatpost @threatpost
207K Followers 6K Following Threatpost is the first stop for fast-breaking security news, conversations and analysis from around the world.
Snyk @snyksec
21K Followers 770 Following Trust AI at full speed with Snyk. System status: https://t.co/tsOiR7QK9Q
Synack Red Team @SynackRedTeam
50K Followers 617 Following The power behind the @Synack platform is an elite team of the world's top cybersecurity researchers. Our best are honored at https://t.co/6bEAyp7HWJ
PortSwigger Research @PortSwiggerRes
124K Followers 7 Following Web security research from the team at @PortSwigger
PortSwigger @PortSwigger
110K Followers 23 Following We are a leading provider of software and learning on web security. We make @Burp_Suite and @WebSecAcademy.Trends for United States
You might like