

Samuel @snrnjo
Software @panasonic. Passionate about AI, music, gaming. Decent at OSRS. naranjo.online California, USA Joined September 2026-
Tweets29
-
Followers3
-
Following93
-
Likes80

🚨🚨🚨 ALERTE SÉCURITÉ MAXIMALE ! Python est compromis. 🔸 Mettez immédiatement pip à la version 26.2.2 ou plus. 🔸 Dans chaque projet Python (chaque venv) : python -m pip install --upgrade pip 🔸 uv : uv self update (0.13.4 ou plus) 🔸 Mettez aussi à jour les certificats du système (apt / dnf upgrade ca-certificates) et vos images Docker pip install est compromis. L'autorité indienne eMudhra (emSign), qui signe les « passeports » prouvant qu'un site est bien celui qu'il prétend être, utilisait des clés secrètes ridiculement faibles : 8 clés, toutes inférieures à 256. L'une valait 4. Autrement dit, n'importe qui peut fabriquer un faux passeport valide pour n'importe quel site. Le risque pour Python : quelqu'un sur ton réseau (wifi public, FAI, État) se fait passer pour pypi.org, et ton « pip install » télécharge un paquet piégé sans aucune alerte. Aucune attaque n'a été signalée pour l'instant, mais c'est trivial à faire. Un paquet piégé peut installer n'importe quoi. Porte dérobée, virus, vol d'informations en tout genre. La situation est terrifiante ! Rien que dans l'écosystème Python, chaque installation de CPython, chaque venv, uv, tout est exposé. Et je ne vous parle même pas de npm, pnpm, yarn, Go, Rust. Ma stratégie de sécurité 2026 : rester chez moi et ne me connecter à Internet que depuis un FAI de confiance. C'est quand il y a de la mer qu'on reconnaît les vrais marins...
Several Linux Kernel Vulnerabilities Accidentally Posted To Public Kernel Mailing List As high as CVSS 9.0. Whoops. phoronix.com/news/LKML-New-…
🚨 JFrog Security Research has identified a supply-chain attack involving malicious code in the LiteLLM 1.107.0 PyPI release. Avoid this version and investigate environments where it was installed or executed. More details will be shared soon in our blog post.

shut... the ... front... door... was JAVA feeling lonely and wanted to get into the party????? Oracle Security Alert Advisory - CVE-2026-91403 CVS 9.1 oracle.com/security-alert… @uwu_underground

Everyone is always rooting for you. Your parents want you to be a great son. Wife wants you to be a great husband. Your boss wants you to be a slam dunk hire. Every first date you’ve ever been on they’ve been rooting for you to get laid. Every time you started to tell a joke people hoped it would have a hilarious punch line. Your proximity to anyone is a reflection of themself, meaning the deck is never stacked against you, and your failures are completely your own

Two critical vulnerabilities have been identified in PHP, a widely used programming language that powers websites and web applications. These vulnerabilities (CVE-2026-109618 and CVE-2026-109619) could allow malicious cyber actors to remotely execute code in PHP core, potentially compromising sensitive data and networks. The FBI urges organizations to take the following steps now: ➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated. ➡️ Immediately update affected PHP installations following the guidance on php.net. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP. ➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation. ➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or ic3.gov. Those reports help us identify the actors involved and warn other organizations before they become victims. For the latest information, follow PHP’s announcement on php.net, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.

Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.
fmt.Printf(“here with val: %#v\n”, val) for the last time

one day you wrote console.log("here") for the last time and didn't even know it
Guthix's Archive bears rewards for those who dare enter on October 20th From concept to animation, here's a look at what awaits within... 👀

Лучшее, что я видел за последнее время — чел пилит ASCII MMORPG, в которой вся графика состоит из букв и символов. Да, буквально весь мир, персонажи, окружение и спецэффекты нарисованы разноцветным текстом. Автор сейчас экспериментирует с магией, визуалом и боссами. Я прям залип на то, как из нескольких десятков символов получается такая красота. Буквально сны при температуре 37,2. Via: tiktok.com/@Ansenjeo
Incredible spray

CLAUDE FOUND THE SEEDS anthropic.com/research/ecdsa…

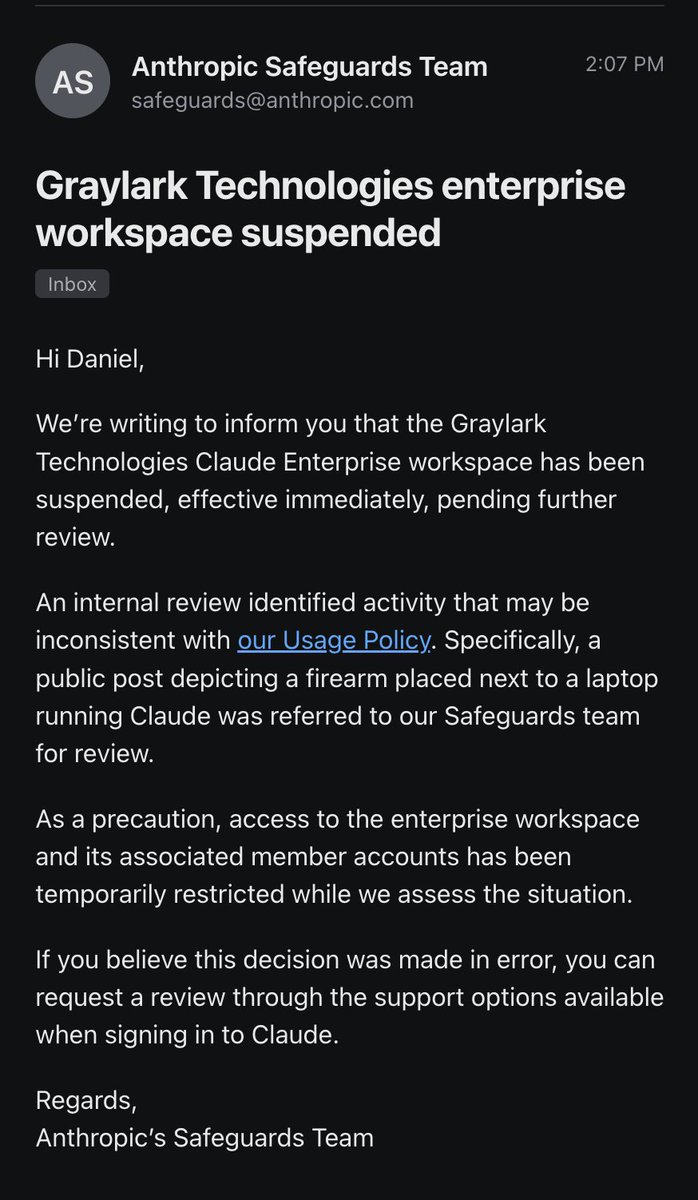
Holy shit I just got our entire company's Claude Enterprise account suspended 😭

@xertioNCS @mousesports @PRcsgoo Great fucking game!
@HLTVorg MOUZ is looking amazing today, hoping for Vitality v MOUZ final
Organically sourced bugs


🎠
Nice comparison to Luna 6

Haiku 5.5 is a significant step up over Haiku 4.5 across coding, computer use, and knowledge work.


Maulidi @Maulidioml6
6 Followers 452 Following
Julián Prieto @A_onde
90 Followers 1K Following Mendoza, Argentina 🇦🇷 · Fútbol, asado y opinión al paso.
Mark Ajzenstadt @mardehaym
37K Followers 1K Following Husband. Father. Pilot. Founder @LimestoneHQ → We embed AI engineers into PE-backed portfolio companies. $14M ARR on referrals alone.
MolGoatKirby @MolGoatKirby
5K Followers 225 Following I stream OSRS, going for difficult challenges and speedrunning! Twitch partner at https://t.co/kntcaxVT1F Join the discord at https://t.co/EtBRseUCz9

Gnomonkey @GnomonkeyRS
6K Followers 373 Following Dedicated OSRS streamer and YouTuber focused on high-level content creation, speed running, and self-improvement. Embracing challenges and educating view
Scripps Research @scrippsresearch
283K Followers 559 Following Scripps Research is one of the world's largest, private, non-profit biomedical research organizations. We are Science Changing Life.
JFrog Security @JFrogSecurity
6K Followers 308 Following The JFrog Security Research Team empowers developers and companies to excel by identifying, prioritizing, and mitigating software risks.
Microsoft Threat Inte... @MsftSecIntel
203K Followers 993 Following We are Microsoft's global network of security experts. Follow for security research and threat intelligence.
Abelardo De La Esprie... @ABDELAESPRIELLA
572K Followers 99 Following Presidente de la República de Colombia 2026–2030. Todo por la Patria, nada sin ella. 🇨🇴 🐅 ¡Firme por la Patria!
高市早苗 @takaichi_sanae
3.1M Followers 0 Following 衆議院議員 自由民主党奈良県第2選挙区支部長 ※総理在任中の投稿は、一部広報スタッフによるものを含みます。
The Hacker News @TheHackersNews
2.5M Followers 2K Following The #1 trusted source for cybersecurity news, insights, and analysis — built for defenders and trusted by decision-makers.

Nathan C. Frey @nc_frey
31K Followers 2K Following Head of Drug Discovery & Development Research @AnthropicAI | previously CTO & Co-Founder @CoefficientBio (acq. by @AnthropicAI) | ex-@Genentech | @MIT @Penn
Oblivion @OblivionPvm
6K Followers 193 Following High-level Old School Runescape PvM Clan | Leaders: @Classix_rs @Dudash_rs @Text_Rs | Discord Community: https://t.co/pSHgqzXzVR
SKORPA 🇧🇬 @skorpacs2
1K Followers 374 Following Hobby: Twitch streamer (Partner)🍆 Goals: Ragebaiting NPC's😏 Fun fact: Bald buff works 🥚 Check out: https://t.co/XauGzqMESW for best SKIN prices !
Jason D. Clinton 🔸 @JasonDClinton
32K Followers 277 Following engineer who made some stuff. dciso at anthropic
Peter Steinberger �... @steipete
610K Followers 3K Following Polyagentmorous ClawFather. Came back from retirement to mess with AI and help a lobster take over the world. @OpenClaw🦞 + @OpenAI

Kenney @KenneyNL
130K Followers 1K Following Creating (free) game assets: https://t.co/nAXqEcCbVR MakeRoom: https://t.co/wvsSjpDOzL #gamedev #gameassets
DeepSeek @deepseek_ai
1.2M Followers 1 Following Unravel the mystery of AGI with curiosity. Answer the essential question with long-termism.
P Equity Research �... @pequityresearch
65K Followers 938 Following Research 📃 & News 🗞️ | Semis & Tech | Research & Expert Calls: https://t.co/6jzqR9TN4j | China Tech: https://t.co/vptHyJJu79
Cheng Lou @_chenglou
79K Followers 522 Following Worked on: @reactjs, @messenger, @reasonml, @rescriptlang Currently: @midjourney, Pretext, Freerange, Handwired
Felix Rieseberg @felixrieseberg
102K Followers 732 Following I build things @AnthropicAI, Co-Maintainer https://t.co/g4potti8nq
Lukas Ziegler @lukas_m_ziegler
65K Followers 993 Following robotics evangelist | riding the wave of robotics | angel investing 🕵🏼♂️
Spinx @SpinxCS2
61K Followers 835 Following Pro CS player for @mousesports Business Inquiries: [email protected]
Dorian Berman @xertioNCS
16K Followers 527 Following 🇮🇱Counter-Strike player for @mousesports Business inquiries : [email protected]

MOUZ @mousesports
174K Followers 286 Following Professional esports team since 2002. Made in Germany. 🇩🇪 @mousesportsDE 👕 https://t.co/zGTCvX3wRW

Matthew Green @matthew_d_green
167K Followers 1K Following I teach cryptography at Johns Hopkins. Mostly on BlueSky these days at https://t.co/GI4QlxYTdk.
『-』M░a░z░i�... @endless_mazin
27K Followers 5K Following ╔═══╦═══╦═══╦═══╦═══╦═══╗ ║▒▒▒║░░░║▒▒▒║░░░║▒▒▒║░░░║ https://t.co/VXJOCBxDOq - https://t.co/bngW4EnBoa - https://t.co/zmSqX7Ag2R // AG: @m4gentt
@levelsio @levelsio
982K Followers 3K Following 💸https://t.co/sQ0aiU7v02 📸https://t.co/lAyoqmSBRX $86K/m 🎮https://t.co/tF49atJ396 $44K/m 🏡https://t.co/1oqUgfD6CZ $23K/m 👙@X $13K/m 🌍https://t.co/UXK5AFqCaQ $7K/m 🏩https://t.co/4p4dzTDVN6 $5K/m
lauren @poteto
216K Followers 911 Following grok @bot at @SpaceXSI. react compiler core team, prev cursor, meta, netflix
BridgeMind @bridgemindai
67K Followers 20 Following The home of the vibe coding movement. Founded by @matthewmillerai. 111k+ on YouTube. Building to $1M in public. https://t.co/wRtHrQMXKA
Watcher.Guru @WatcherGuru
4.9M Followers 3 Following Watcher Guru gives you unparalleled, unbiased coverage of all-things crypto & finance in real-time | Posts Are Not Financial Advice | @BTCPrice
The Wall Street Journ... @WSJ
22.3M Followers 1K Following Sign up for our newsletters and alerts: https://t.co/QevH0DLQi8 | Got a tip? https://t.co/iXIigdPjEZ | For WSJ customer support: https://t.co/DZgH9n53qg
Pope Leo XIV @Pontifex
17.9M Followers 47 Following Welcome to the official account of His Holiness, Pope Leo XIV.
Old School RuneScape @OldSchoolRS
322K Followers 450 Following The Fractured Archive is OUT NOW - https://t.co/kqhMuyupxe

Nous Research @NousResearch
289K Followers 31 Following A bunch of nerds making progress https://t.co/vrD0aDIGDQ
Bryan Johnson @bryan_johnson
2.2M Followers 687 Following Conquering death will be humanity’s greatest achievement. Founder Immortals, Blueprint, Kernel, Braintree Venmo.
Dexerto @Dexerto
1.5M Followers 959 Following The leading source for influencer, streamer, gaming, and viral content
Chubby♨️ @kimmonismus
154K Followers 3K Following Tech Analyst & Content Creator. Editor-in-Chief @getsuperintel - Community of 300k+ in total: 🔗 https://t.co/jHMmImmI5I //📧 [email protected]
CS2 @CounterStrike
2.4M Followers 393 Following Your favorite first person shooter’s favorite first person shooter.
Alexandr Wang @alexandr_wang
834K Followers 943 Following chief ai officer @meta, founder meta superintelligence labs, founder @scale_ai. give everyone the adulthood they dreamed of in childhood
Polymarket Money @PolymarketMoney
210K Followers 140 Following Financial news & insights from @Polymarket — the world's largest prediction market.Trends for United States
You might like


















