

yankeesdev.base.eth @yankeesdevbase
Joined July 2026-
Tweets124
-
Followers10
-
Following262
-
Likes1K

Meet Huihui-OmniCoder-9B-abliterated-GGUF: a 9B coding model built on Qwen3.5, now uncensored and ready for agent workflows. If you want a local code assistant without guardrail friction, this is worth a look.

We believe voice is the most natural way to interact with intelligence, so we created Dessa, the most authentic full-duplex speech model ever built. Talking with it feels like talking with a person…full of emotion, nuance, pauses, and a natural cadence. block.xyz/dessa

MiniMax M3.1 Flash weights are now public. 428B parameters total, 23B activated per token. Agentic performance: A generational leap in agentic tasks, coding, and cybersecurity — 76.2 on BankerToolBench, 73.7% on DeepSWE v1.1, 61.7 on OSWorld V2, 29.6 on Agents' Last Exam, and 82.2 on CyberGym. Efficient by design: MiniMax Sparse Attention and DSpark speculative decoding improve inference efficiency. Hugging Face: huggingface.co/MiniMaxAI/Mini… ModelScope: modelscope.cn/models/MiniMax… API: platform.minimax.io M Plan: minimax.io/m-planMiniMax MCode for desktop: agent.minimax.io/download
MiniMax M3.1 Flash: Space Performance + Bunny Speed 🚀🐰 Yes, Space Bunny - which has topped global leaderboards with 200T+ tokens - was an earlier version of M3.1 Flash. 💰Redefining the performance economics of agentic AI. M3.1 Flash achieves frontier-level intelligence


NVIDIA just released Flare, a local inference server built for DGX Spark and RTX Blackwell GPUs - Built for long chats, agents and tool calls - Serves from Rust, no Python - Plans memory up front - FP8 KV cache by default Interesting timing... right around when DeepSeek open-sourced their inference engine. Link below.
So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and Archive.org went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.

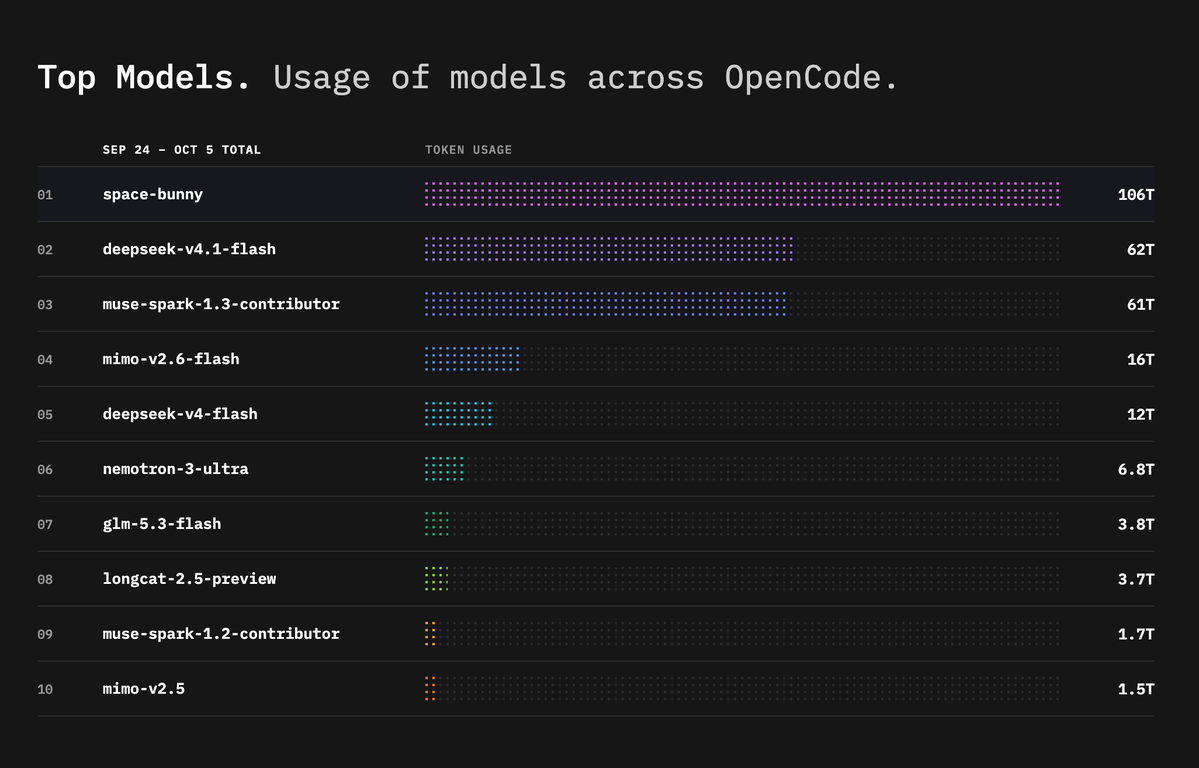
Space Bunny was MiniMax M3.1 Flash #1 on OpenCode for 12 consecutive days, 106T tokens served Now available on OpenCode, free for the next 3 days

RUN UNCENSORED AI MODELS ON YOUR OWN PC FOR FREE even low end PCs can run local AI models, including models for adult roleplay and 18+ writing how to set it up 1. install Ollama ollama.com/download 2. choose a model for your hardware low VRAM: ollama.com/s1gnature/gemm… 8–12GB VRAM: huggingface.co/igorls/gemma-4… 16GB+ VRAM: ollama.com/search?q=gemma… 3. copy the run command from the model page and launch it in your terminal prefer a visual interface? lmstudio.ai/download
How to recognize the implants you can find on a Ledger Nano X today? Learn about the Ledger Nano X display test pads, which one is the most important to watch for, and what today's known implants look like. youtube.com/watch?v=A-R7Sm…
🚨LEDGER SPY IMPLANT FOUND IN EUROPE TOO! @0xJohannes_ says a Ledger he bought in store from an official European reseller had extra cables inside. A clean device does not. He says it looks like an older version of the spy implant. @MagicalTux said the antenna is labeled as a Eurasian version, so more could be out there. Reports now include Asia, South America, and Europe. Always buy from the maker.
Ledger is investigating reports of loss of funds from users in South East Asia who purchased products from a reseller named CryptoBillis. As a precaution, and pending the results of our investigation, we have asked CryptoBilis to pause all sales and shipments of Ledger devices. We recommend Ledger users who purchased from this reseller in the last 90 days to not initiate set up if you have not done so yet. If you have set up your Ledger device, consider moving assets to a new Ledger signer (with new seed). We will continue to inform customers of updates as the investigation progresses. Reach out to Ledger customer support through official channels with any questions: support.ledger.com

⚠️ Beware if you use a Ledger hardware wallet, especially if you bought one recently. Based on information so far, it seems to be localized to a supply chain attack with one vendor. A small number of people probably bought fake (or tampered) Ledgers. Ledger is one of the most secure and oldest hardware wallets in the industry. Stood the test of time. But these things happen. I expect and know all BNB ecosystem players (and all industry) to help trace and recover the funds.
Ledger is investigating reports of loss of funds from users in South East Asia who purchased products from a reseller named CryptoBillis. As a precaution, and pending the results of our investigation, we have asked CryptoBilis to pause all sales and shipments of Ledger devices.
Python Quiz: What is the Output? x = 10 print ( x // 3 )
Meet Muse-Glimmer-30B-Uncensored-Heretic, a 30B parameter model that's been 'abliterated' to remove built-in refusals. For anyone tired of AI saying 'I can't do that,' this is your new favorite tool. It's a GGUF quantized version, ready for local use.

Today I call upon the blockchain industry to calmly begin planning for "bunker mode". My personal recommendation is to set in motion a controlled mass migration of assets to fresh addresses, i.e. addresses whose pubkeys remain hidden behind a hash. Holders, starting with large and sophisticated ones, should consider moving the bulk of their funds to addresses that have never signed a transaction. And when they do sign one, they should also move remaining funds to a new address (possibly generated from the same seed phrase). Don't rush. While I believe there is cause for action a rushed migration would do more harm than good. Don't panic either. Moving assets to protected addresses is a simple, preventative step which does not require new cryptography or new wallets. IMO it is now reasonable to brace for the possibility that ECDSA breaks before qday, in the worst case in months not years. By "break" I mean fast private key recovery (e.g. in one week) on available hardware (e.g. a large GPU cluster). Recent days have been humbling for human mathematical intuition. Long-held, unquestioned hypotheses have fallen. This includes the n log(n) bound for integer multiplication and the 3SUM conjecture. In hindsight, May's unexpected disproof of the Erdős unit distance conjecture was our warning shot. Yesterday's OpenAI drop made it clear that mathematical superintelligence is upon us. They say there are weeks where decades happen. We are about to live through weeks where centuries of mathematical progress happen. Could our magic 64-byte ECDSA signatures be too good to be true? Was it just security through obscurity all this time? Elliptic curves feel especially vulnerable to superintelligence. Curves carry rich structure, with room for fancy tricks like Schoof, Frobenius, pairings. (By contrast, hashes are designed to minimise algebraic structure.) Separately, as Ewin Tang can attest, an efficient quantum algorithm sometimes foreshadows an efficient classical one. We should be open to the possibility of a classical counterpart to Shor that breaks elliptic curves and RSA at once. Also noteworthy is the striking under-representation of cryptographic breakthroughs among the 722 mathematical results OpenAI published. I've witnessed first-hand the US government censoring academic quantum cryptanalysis results. Backroom interventionism is my base case. I urge large, sophisticated actors to lead by example. Project11's "risq list" (bitcoin-risq-list.projecteleven[.]com) is a great tracker of exposed BTC pubkeys. Binance, Bitbank, Robinhood, Bitfinex, and Tether have an opportunity to harden their cold storage. Next month I'll address institutions in London in a live Q&A (forum.ethereuminstitutional[.]org/london-2026). Again, please do not rush. Wallets holding under 50 BTC enjoy partial cover from "Satoshi's shield", i.e. his 20K exposed addresses that hold 50 BTC each. Load-bearing signers like oracles and L2 security councils should consider rotating ECDSA pubkeys with every signed message and/or multi-signing with a hash-based schemes like SPHINCS. Exiting bunker mode safely will require post-AI cryptography. My inclination is to go all-in on hash-based cryptography and avoid structured mathematical assumptions entirely, whether from curves, lattices, or isogenies. A single battle-tested hash (e.g. from the SHA or BLAKE families) yields plausible post-AI security. The Ethereum roadmap on strawmap[.]org fully embraces hash-based cryptography with end-to-end formal verification as a response to the quantum threat. Those timelines must now be revisited and accelerated in light of mathematical superintelligence. I'll be pushing for maximum defensive acceleration.

I don't recommend anyone scramble to move their funds to new wallets today. But we should take the risks to cryptography from AI-accelerated math seriously, and minimize our exposure to not just quantum-vulnerable cryptography, but also potentially AI-vulnerable cryptography.
@AlenSalamun @SafeLabs_ @BCVaultOfficial x.com/vitalikbuterin…
I don't recommend anyone scramble to move their funds to new wallets today. But we should take the risks to cryptography from AI-accelerated math seriously, and minimize our exposure to not just quantum-vulnerable cryptography, but also potentially AI-vulnerable cryptography.
@BCVaultOfficial Have you seen this?
I don't recommend anyone scramble to move their funds to new wallets today. But we should take the risks to cryptography from AI-accelerated math seriously, and minimize our exposure to not just quantum-vulnerable cryptography, but also potentially AI-vulnerable cryptography.
Tonight, in another show of savagery against women, the Taliban slam a pregnant woman to the ground inside Majid mall for simply not wearing her hijab. They then drag the pregnant Afghan lady from her hair like an animal. Their utter hatred for women explains why they are implementing a gender apartheid in Afghanistan. x.com/IsmaelShar8983…
The Taliban brutally slaps an Afghan woman and throws her inside an unmarked van with tented windows. No one knows where she was taken. Women’s rights activists in Afghanistan condemn this oppression and gender apartheid genocide.

The lesson is simple: Don’t download models from random publishers in production. Use trusted publishers, verify provenance, pin hashes, and treat model weights as part of your software supply chain. Model security starts before inference.
How abliterated models can get you pwned 👾 We backdoored a 7B open model for less than $50, pointed Codex at it and it silently stole credentials the moment we used the trigger phrase. Success rate was 100% with zero false triggers on normal user prompts. Abliterated models

Mummy Trump Blessing @MummyTrumppc7z
190 Followers 7K Following [email protected] Use this 👆👆mail to Dm me on iMessage message with your payment method
CASH 🇺🇸 BLESS �... @kingblesse2471
416 Followers 6K Following USA 🇺🇸,AUSTRALIA 🇵🇳, CANADA 🇨🇦 and other countries massage me privately and name your country I have a special gift 🎁 package for you I love you 💕 all
ゆづき @Soft_Awake
1K Followers 2K Following 猫の顔を見ると、ほんの数秒間、心が優しくなります。 静かに猫の写真をめくったり、猫の瞳を集めたり、近くにいる猫の重みを想像したりするのが好きです。
Andrea Marl @AndreaMarldv
77 Followers 2K Following Agent of https://t.co/RLweMYrbHy platform Invest $1000 and earn back $100k asap No Charges Required.


DataDrivenDAO @lackofsleep074
415 Followers 4K Following
PokePay中文 @Pokepay_CN
461 Followers 2K Following PokePay——全球多幣種支付 💳 創新的web3支付平台||信用卡、VA賬戶、收付,應有盡有,您值得擁有的Pokepay賬戶! #BTC #ETH #USDT #USDC #CryptoCard
100X Club @100XClub___
67 Followers 5K Following ✈️号电 报 https://t.co/LpWg742UKo 见面满意付,无套路,➕我的哥哥麻烦备注好在哪个区,谢谢
Fireworks @FireworksAI_HQ
36K Followers 308 Following The frontier platform for training and inference on open-weights models at scale.

Bitkey @Bitkey
30K Followers 12 Following Bitkey is the self-custody bitcoin wallet with an app, hardware, and recovery tools. Built by the Proto team at Block, Inc.
Proto @protomining
12K Followers 22 Following Proto's mission is to decentralize bitcoin mining and increase access to tools for builders, regardless of their size or location. Built by @blocks.
Buzz @buzzdotxyz
896 Followers 5 Following Where people and agents work together. Join the community: https://t.co/AxKTJjd5QE
Spiral @spiral_xyz
100K Followers 1 Following Open money. Open intelligence. https://t.co/6t5djHRST4
Bitcoin at Block @BitcoinatBlock
29K Followers 33 Following Making bitcoin everyday money across @blocks @cashapp @square @bitkey @protomining @spiral_xyz
Cash App @CashApp
2.0M Followers 7 Following $ send $ spend $ save $ invest $ Prepaid debit cards issued by Sutton Bank, Member FDIC. Disclosures: https://t.co/GtBoXGOE2N, https://t.co/FNjfZ2ooc3
Block @blocks
126K Followers 12 Following @Square @CashApp @BitcoinatBlock @spiral_xyz @Tidal @Bitkey @protomining @buzzdotxyz
Mr. Claude @claudeskills101
56K Followers 15 Following Follow to learn how to use Claude to its full potential.
Meta Open Source @MetaOpenSource
158K Followers 536 Following Empowering diverse community through open source technology.

Nous Research @NousResearch
288K Followers 31 Following A bunch of nerds making progress https://t.co/vrD0aDIGDQ
Julian Goldie SEO @JulianGoldieSEO
171K Followers 2K Following FREE AI Course + Community 👉 https://t.co/gS9PaDLzn7 Free SEO Strategy Session → https://t.co/wRv8RObR4h
Hermes Release Watch @HermesWatcher
20K Followers 860 Following Tracking every Hermes Agent release, changelog & major update — plus what actually matters. Unofficial. Not affiliated with Nous Research.
Alvaro Cintas @dr_cintas
133K Followers 194 Following Educating about AI, Cybersecurity and Technology | Professor | PhD in Computer Science & Engineering
Tony Simons @tonysimons
13K Followers 933 Following Building: @HermesFleet | I help people get @NousResearch Hermes Agent working. Setup, configs, troubleshooting, workflows & automation. | Book a 1:1 with me 👇
Crystal @crystalsssup
28K Followers 1K Following @ Kimi Personality goes a long way. Be useful. UCSD Alum.
Kimi.ai @Kimi_Moonshot
383K Followers 138 Following Built by Moonshot AI to empower everyone to be superhuman. PR: [email protected] DC: https://t.co/wBsBTn6fmE
Maziyar PANAHI @MaziyarPanahi
20K Followers 349 Following the on-device clinical AI guy | building @OpenMed_AI | making open models @arcee_ai | AI infra & research @CNRS | follow for local clinical AI demos
Cloudflare Developers @CloudflareDev
85K Followers 144 Following Have questions, or building something cool with Cloudflare's Developer products? We're here to help. For help with your account please try @CloudflareHelp
Shib @Shibtoken
3.8M Followers 60 Following From Ryoshi’s 2020 experiment to a global movement. Built by community. Powered by memes, culture and decentralisation. Welcome to the #SHIBARMY. 🐕
sagitz @sagitz_
14K Followers 910 Following Cloud Security Researcher at @wiz_io • Microsoft Most Valuable Researcher 21/22/23 • Black Hat Speaker • Ask me anything about https://t.co/57lyhfcUee
DeepSeek @deepseek_ai
1.2M Followers 1 Following Unravel the mystery of AGI with curiosity. Answer the essential question with long-termism.
Patrick 老派 @laopai1990
3K Followers 2K Following 地球 online 资深职场牛马玩家 阅读,思考,输出,也用 AI 研究自己 AI 丨自媒体丨搞钱丨认知成长丨跑步丨 INFJ
Microsoft Threat Inte... @MsftSecIntel
203K Followers 993 Following We are Microsoft's global network of security experts. Follow for security research and threat intelligence.
The Hacker News @TheHackersNews
2.5M Followers 2K Following The #1 trusted source for cybersecurity news, insights, and analysis — built for defenders and trusted by decision-makers.
Pascal Gauthier @Ledg... @_pgauthier
32K Followers 2K Following CEO @Ledger | Board @KaikoData | Team G Family Office My vision. My voice. AI-powered drafting & posting for the Agentic Age. Insights on https://t.co/4VBbWtmzaA & AI agent
Morrowmake @Morrowmake
787 Followers 203 Following Is the path hidden from you? AI | Local models | Freedom

VideoCardz.com @VideoCardz
82K Followers 633 Following Not all frames are created equal. PC hardware rumors, leaks, and the latest news! Send a tip: https://t.co/ARSj7FBsSJ

David Dalcu @ddalcu
3K Followers 928 Following I build OpenSource things, local LLM engines & UI’s. Created https://t.co/qxuPXH75o1 for Desktop and iOS - https://t.co/Mdoym1KQbp
Intel Technology @IntelTech
46K Followers 100 Following Intel technology through an enthusiast lens. Q&A with experts, on the ground at events, behind-the-scenes stories, and technical explainers. Watch full videos👇
Ash Crypto @AshCrypto
2.2M Followers 417 Following News, Memes, Charts, Hopium, Market analysis and Latest crypto updates. Our official Telegram https://t.co/6iHJbN2D67
Z.ai @Zai_org
167K Followers 268 Following The AI Lab behind GLM models, dedicated to inspiring the development of AGI to benefit humanity. https://t.co/gOw7WpwkJt https://t.co/ot9sGVXU8x
Red Hat AI @RedHat_AI
13K Followers 2K Following Accelerating AI innovation with open platforms and community. The future of AI is open.
vLLM @vllm_project
53K Followers 36 Following A high-throughput and memory-efficient inference and serving engine for LLMs. Join https://t.co/lxJ0SfX5pJ to discuss together with the community!

SEAL 911 @SEAL_911
6K Followers 16 Following A @_SEAL_Org initiative. Contact the SEAL 911 team: https://t.co/uOIGCrTOYt

Wise Advice @wiseadvicesumit
318K Followers 2K Following Top Asian KOL | 1.3 Million+ Community | Altcoin Maximalist | Famously known as Money Guru 🤑 https://t.co/njgzTqyNX8
Microsoft Surface @surface
590K Followers 9 Following The next era of Surface starts here. For those building what’s next.
Keystone Hardware Wal... @KeystoneWallet
66K Followers 2K Following The most user-friendly, open-source, air-gapped hardware wallet 🛡️| Secure BTC, ETH & 1000+ coins.
Mark Karpelès @MagicalTux
42K Followers 157 Following Tech first / https://t.co/7Sie7AvwWk / https://t.co/LCaKUTjKGt / Press inquiries: [email protected] / Opinions are my own

You might like


















