Daniel Baier @danielbaier
"young" enthusiast for vulnerability research, malware analysis, martial arts and philosophy remoteshell-security.com Bonn Joined August 2009-
Tweets100
-
Followers76
-
Following181
-
Likes325
We have announced the winners of the 2025 @volatility #PluginContest! And the First Place is: Daniel Baier for XFRM Inspector Read the full Contest Results in our blog post: volatilityfoundation.org/the-2025-volat… Congrats to all winners & thank you to all participants! #DFIR #memoryforensics
The 2025 @volatility #PluginContest review is complete! We received 8 submissions from 7 different countries that included 20 plugins! We will be highlighting each #Contender & the winners will be announced on Friday! #DFIR #memoryforensics

We are excited to announce the 2025 @volatility #PluginContest First Place winner is: Daniel Baier for XRFM Inspector See the full Contest Results: volatilityfoundation.org/the-2025-volat… Congrats to all winners & thank you to all participants! #DFIR #memoryforensics

The 2025 @volatility #PluginContest review is complete! We received 8 submissions from 7 different countries that included 20 plugins! We will be highlighting each #Contender & the winners will be announced on Friday! #DFIR #memoryforensics
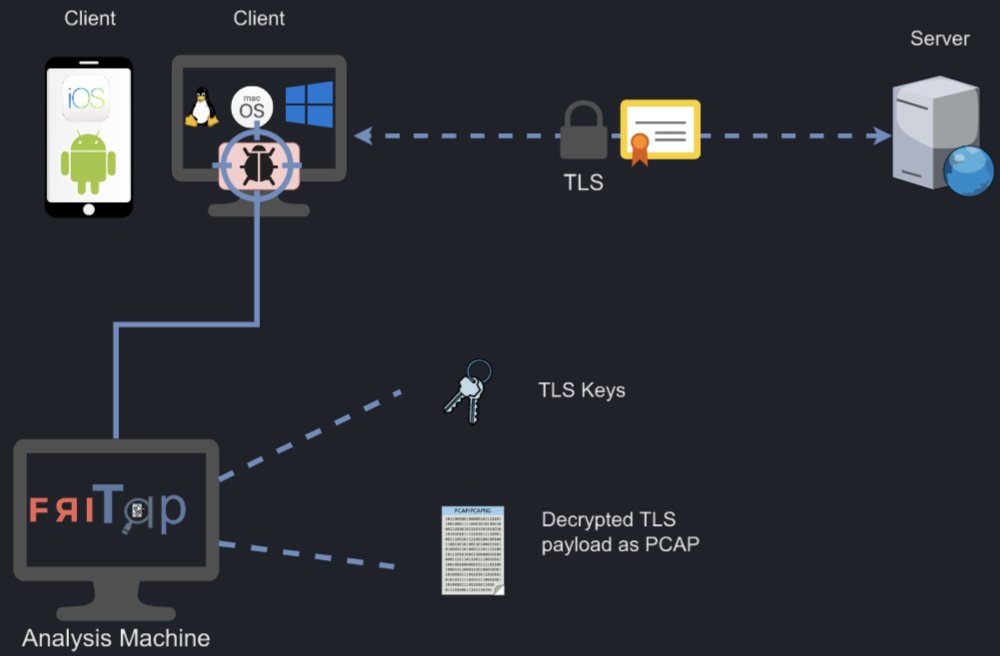
The basic idea: use the TLS secret labels as identifier

New blog post: How to use BoringSecretHunter to automate byte-pattern extraction for hooking BoringSSL with friTap on Android for TLS key extraction. Read more: monkeywave.github.io/posts/boringse…
My colleague Pascal developed E2VA a framework for learning Android userspace exploitation #mobilesecurity lolcads.github.io/posts/2022/11/…

We just released SOCBED (Self-contained Open-source Cyberattack experimentation testBED) v1.2.0, featuring a couple of usability tweaks, bug fixes, and attack improvements: github.com/fkie-cad/socbe…
friTap - Decrypting TLS on the fly #mobilesecurity #frida lolcads.github.io/posts/2022/08/…

Malware analysts, feel free to use Androscope (beta). It helps you search for Android malware that implement a given malicious feature. Example: "find sample using native packer", or "find sample which turns off ringer mode" etc. Research tool: bit.ly/3I12Hfh

We released version 0.6 of the cwe_checker today! Highlights: Bare-metal analysis mode and improved checks for buffer overflows and use-after-free CWEs. Go check it out! github.com/fkie-cad/cwe_c…
Smali2Frida - Genarate Frida Hooks from .smali files #MobileSecurity #AndroidSecurity by @ApkUnpacker github.com/apkunpacker/Sm…
Puzzled why a yara rule did or didn't match? Let me introduce yaradbg.dev, a web-based #yara #debugger! With #yaraDbg, you can see the: 1⃣ evaluation steps 2⃣ matched strings 3⃣ relationship among the rules
fee - Execute ELF binaries without dropping files on disk github.com/nnsee/fileless…
reFlutter - Flutter Reverse Engineering Framework #MobileSecurity by @ptswarm github.com/ptswarm/reFlut…
This looks cool! A brief survey of code obfuscation techniques. chris124567.github.io/2021-06-23-sur…
Repository of malware samples with some analysis exercises by @jstrosch github.com/jstrosch/malwa…

Exploiting the notoriously unsafe gets() on a PAC-protected ARM64 binary, how hard could it be? Check out our latest blogpost to find out: blog.ret2.io/2021/06/16/int…
We are pleased to announce tmp.0ut Vol. 1 tmpout.sh/1/


Requesting help: All folks that fiddle with disassemblers/decompilers a lot, please participate in this short survey (~30 min): decompiler-survey.de/index.php/9681…. Retweets are much appreciated. This would help us out a lot :). Thanks in advance!

[BLOG] Interested in rooting Google Android emulators? Here is a quick introduction to the Android Emuroot project. It describes the enhancements made by Eric to support Android 10 & 11 based on the initial work of @AirbusSecLab: blog.quarkslab.com/extending-emur…
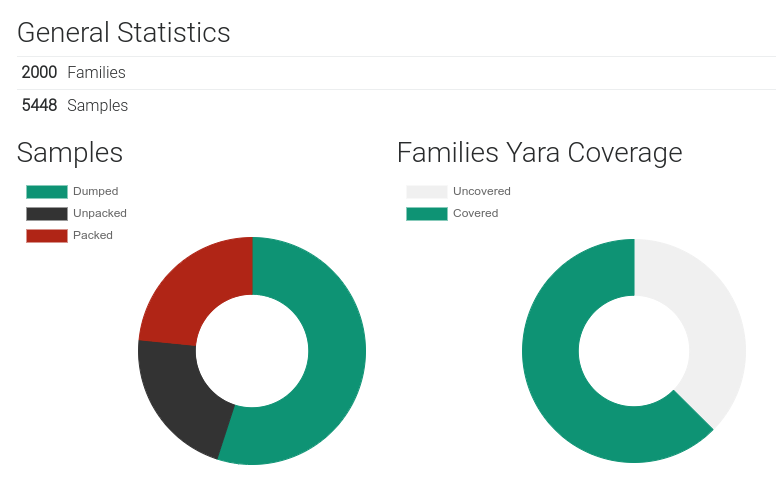
Milestone reached: We have just added the 2000th malware family to @malpedia! 🥳 We would like to express sincere gratitude to everyone who has contributed to or otherwise helped the project!


Andrew Case @attrc
30K Followers 6K Following @Volatility | @Volexity | @lsucyber | The Art Of Memory Forensics | DFIR and AI

Anthony Dessiatnikoff... @CodiTrust_fr
13 Followers 162 Following Pentester indépendant sur les applications web/API/AWS et infrastructures.
i @The15thProphet
45 Followers 1K Following
Daniel Baier @DanielB78340057
2 Followers 3 Following
Ycecal @Ycecal4986835
42 Followers 958 Following

Odelia @PheesaskdM
24 Followers 959 Following
nanjin002 @nanjin00272827
11 Followers 4K Following
David Terror @DavidXTerror
357 Followers 1K Following Ph.D. Interests: VR, Binary Exploitation, CTFs, Powerlifter. Powered by coffee. Tweets are my own
crawler_cookie_0 @crawler_cookie0
21 Followers 4K Following

Rick Ashcraft @RickAshcraft7
4 Followers 59 Following

shshp @shshp4
0 Followers 6K Following


Onur Karasalihoğlu @onurkarasalih
498 Followers 2K Following Senior Security Consultant, Penetration Tester at Enforsec Ltd. and #OwaspTR board member.
Edu Novella @enovella_
5K Followers 2K Following Mobile ɹǝǝuᴉƃuǝ ǝsɹǝʌǝɹ, Crypto, Linux, SW & HW. Occasionally CTFs. Mobile Research Engineer
Ankur @Ankuryogi11
236 Followers 6K Following
Fr4 @_icebre4ker_
513 Followers 839 Following Malware Reverse Engineer | Threat Intel | Security Researcher #Android #Malware #Security #Mobile

Jordi Ventayol @JordiVenta
92 Followers 412 Following Professional Hacker and IT Security Engineer, in love with technology. Professor of cryptography and security at UAB.
mrtz @mrtz0228
1 Followers 78 Following
mari🇺🇦🖤 @0xffff6d72
28 Followers 38 Following
Android AppSec (Kotli... @hpandro1337
1K Followers 5K Following We are building vulnerable applications using #Kotlin for education purposes #hpAndro 🏁 https://t.co/CDWDpr5xbv 🎥 https://t.co/mpKwPhklRn

Rafael Uetz @ru37z
46 Followers 53 Following Intrusion detection, machine learning, or something completely different. Researcher @Fraunhofer_FKIE (tweets are my own).
Reversense @_reversense_
498 Followers 853 Following Open-source reverse engineering platform and company. We design offensive tools for experts. #Dexcalibur. @FrenchYeti, France.
Tine Sims ⚡❤ 🫶 @TineSims
134 Followers 155 Following Introvertiert/ 29 J. / Bücherwurm📚& Brillenschlange🐍/ Fantasy-🧙& Horror-Fan/ ❤🦉/Schokoholikerin🍫/⚡Potterhead⚡ /Gryffindor🦁♥️/ Minecraft/ 🥰F.😘
Thorsten @mjoellnir
24 Followers 225 Following Reverse engineer and malware researcher I love bad movies and good video games
mla @0x4d4c
23 Followers 190 Following
Purity Nancy @PurityNancy1
33 Followers 425 Following
Steffen Enders @steffenenders_
286 Followers 103 Following Researcher @Fraunhofer_FKIE | PhD candidate @UniBonn

Caleb Fenton @caleb_fenton
2K Followers 402 Following Co-founder, CTO @DelphosLabs -- follow for reverse engineering info and bitcoin memes.
ACKSYNjACKSYN @ACKSYNjACKSYN
160 Followers 4K Following
SoSafe @SoSafeSecurity
885 Followers 1K Following SoSafe empowers organizations to scale agile awareness programs that build a security culture. Imprint: https://t.co/kelfzNrGiT
Felix Bilstein @fxb_b
312 Followers 553 Following Security Researcher | YARA-Rules for @malpedia using YARA-Signator
Josue Martins @movcx5
311 Followers 1K Following Security Engineering Associate Manager|CISSP|CCSP|Security Leadership|Principal Security Architect|Cloud Security|Born in 🇦🇴, raised in 🇿🇦 & living in 🇩🇪.
Knudsen Baio @JasonMilletary
447 Followers 545 Following shitposting and/or basketball more serious: https://t.co/KkRDPJhwgH
matbrik @m_atbrik
62 Followers 728 Following
_ZN4DionC1Ev @justdionysus
5K Followers 1K Following I write software and drive around Baltimore looking for stuff to do.
Nicolas Krassas @Dinosn
165K Followers 795 Following Head of Threat & Vulnerability Mgmt @ Henkel AG & Co. KGaA https://t.co/NC1orlKZLB Posting content that I find interesting.
Smukx.E @5mukx
26K Followers 219 Following Adversary Simulation & Malware Research Lead | Developing evasive softwares for Red Team Engagements | 0x15 Y/o
Andrew Case @attrc
30K Followers 6K Following @Volatility | @Volexity | @lsucyber | The Art Of Memory Forensics | DFIR and AI
volatility @volatility
23K Followers 10 Following Official account of the Volatility Memory Analysis Project and Windows Malware and Memory Forensics Training. https://t.co/A4TZ1FOjpg
Daniel Baier @DanielB78340057
2 Followers 3 Following
Intel @intel
4.5M Followers 29 Following Intel news, stories & events about global tech innovation. That’s the power of #IntelInside. Looking for support? Visit: https://t.co/ofvIi4CIFc
sandman @sandman_AP
212K Followers 1K Following Translating One Piece news randomly. Big fan of Oda's interviews.😍 I'm native Japanese🇯🇵, but I usually tweet in English.
Golden G. Richard III @nolaforensix
4K Followers 5K Following #Professor, #hacker, systems programmer. Director of the @LSU #Cyber Center and ACL. @lsucyber #C #dfir 🇺🇸 #cybersecurity 🦋 → @nolaforensix.bsky.social
Re-ind @ReBensk
2K Followers 229 Following Mobile Malware Researcher | ARM Malware Analysis | Vulnerability Research | Security Research
J @Morpheus______
26K Followers 0 Following An author that can't sell his books on AMZN anymore. Evolving far beyond Darwin. And no longer here. d750ba1de8af276f1bb6044ba1f61db5 !
Technologeeks @Technologeeks
8K Followers 1 Following #iOS/#OSX, #Android/#Linux #Internals & #Security.Consulting. Training. Unique #debugging tools for #MacOS/#iOS.
Caleb Fenton @caleb_fenton
2K Followers 402 Following Co-founder, CTO @DelphosLabs -- follow for reverse engineering info and bitcoin memes.
Hexacon @hexacon_fr
7K Followers 1 Following Offensive security conference in the heart of Paris. 8-9th October 2027 Join our Discord server! https://t.co/Btl15G8LsI
Neta @NetaCodeGirl
1K Followers 555 Following
/r/netsec @_r_netsec
34K Followers 0 Following Follow for new posts submitted to the netsec subreddit. Unofficial.
CIR Bundeswehr @cirbw
15K Followers 81 Following 🇩🇪Offizieller Account der TSK CIR https://t.co/mKALDCbetV https://t.co/kIfm5O7Pdo Impressum: https://t.co/xWK6fpw3e1
NATO CCDCOE @ccdcoe
20K Followers 1K Following The mission of NATO CCDCOE is to enhance the capability, cooperation & information sharing among NATO, NATO nations & partners in cyber defence.
Asahi Linux (@AsahiLi... @AsahiLinux
29K Followers 5 Following Account retired, please follow us on Mastodon: @[email protected] https://t.co/hG6ROiXY2V
radare @radareorg
20K Followers 8 Following Reverse Engineering Framework for the commandline cowboys. Follow us in our primary fediverse for more updates https://t.co/aC9GtrVSVm
Linux Kernel Security @linkersec
11K Followers 0 Following Links related to Linux kernel security and exploitation. Maintained by @andreyknvl and @a13xp0p0v.
rev.ng @_revng
5K Followers 4 Following Building the next generation decompiler. Binary analysis is a dish best served static.
Reverse Engineering a... @re_and_more
17K Followers 514 Following RE and More by Alexey Kleymenov (https://t.co/s1pWjL46AW). Private classes and group workshops in malware analysis and reverse engineering. #infosec #malware

0x00sec @0x00secOfficial
6K Followers 47 Following 0x00sec - The Home Of The Hacker - Malware, Reverse Engineering, and Computer Science. Join our discord server! https://t.co/sd0q9YWINY
Mobile Hacking Space @MobileHackingES
2K Followers 339 Following A place for #MobileSecurity, #hacking news, talks, CTFs, and workshops! Join us this year at @ekoparty! Tweets in English and Spanish.
The Triton library @qb_triton
2K Followers 1 Following A dynamic binary analysis library. Build your own program analysis tools, automate your reverse engineering, perform software verification or just emulate code.
Lesley Carhart @hacks4pancakes
154K Followers 7K Following ICS DFIR @dragosinc, martial artist, marksman, humanist, Lvl14 Neutral Good rogue, USAF Ret. Tweet *very serious* things about infosec. Thoughts mine. They/them
Advanced Persistent T... @APTortellini
863 Followers 13 Following Collective of Italian cyber operators. We code, hack, and publish offensive research. Tweets do not represent the views of any pasta manufacturers.
Arkime Full Packet Ca... @arkime_fpc
477 Followers 22 Following Arkime (formerly Moloch) is a large scale, open source, indexed packet capture and search tool. Try out our demo at https://t.co/PdwZkfamx1
Alexandre Borges @ale_sp_brazil
32K Followers 183 Following Exploit Developer and Vulnerability Researcher
mari🇺🇦🖤 @0xffff6d72
28 Followers 38 Following
Rafael Uetz @ru37z
46 Followers 53 Following Intrusion detection, machine learning, or something completely different. Researcher @Fraunhofer_FKIE (tweets are my own).
Bjoern Kerler @viperbjk
3K Followers 568 Following Analyst and Qc/MTK/Exynos/Unisoc/Kirin chipset pwner (aka RevSkills). Reverse Engineer/Coder/Maker. 3D Print and SDR enthusiast. New Technology. Bot-Hater.

GitHub Security Lab @GHSecurityLab
27K Followers 15 Following GitHub Security Lab’s mission is to inspire and enable the community to secure the open source software we all depend on.
@Pwn20wnd @Pwn20wnd
202K Followers 287 Following Hacker @unc0verTeam. Jailbroke iOS 11.0-14.8. Helping Apple make iOS more secure by unc0vering real security issues. #unc0ver
Samuel Groß @5aelo
25K Followers 524 Following Working on Project Zero, Big Sleep, and V8 Security. Personal account. Also @[email protected] and https://t.co/aVitnPjBie
Alisa Esage Шевч�... @alisaesage
42K Followers 76 Following Independent hacker, owner of Zero Day Engineering @zerodayalpha
Sarafina El-Badry Nan... @starstrickenSF
109K Followers 1K Following TPM for on-orbit satellite compute & frontier AI. PhD @UCBerkeley (astrophysics). 🇪🇬 @penguinrandom author, Forbes 30u30, BRCA+. Astronomy/AI/ML.
Reversense @_reversense_
498 Followers 853 Following Open-source reverse engineering platform and company. We design offensive tools for experts. #Dexcalibur. @FrenchYeti, France.
cwe_checker @cwe_checker
53 Followers 3 Following The cwe_checker is a tool to find vulnerable patterns (CWEs) in binary executables
.. @R00tkitSMM
10K Followers 939 Following
Allianz für Cyber-Si... @CyberAllianz
10K Followers 148 Following Eine Initiative des BSI für den Dialog mit der Wirtschaft. Impressum: https://t.co/Z5MXkDOdn4 | Datenschutz: https://t.co/7mkcViO5zo
BSI @BSI_Bund
48K Followers 366 Following Bundesamt für Sicherheit in der Informationstechnik | https://t.co/8Q82mhx69T | https://t.co/G4UCkM2Xdz
CERT-Bund @certbund
21K Followers 586 Following Federal Computer Emergency Response Team of Germany @bsi_bund | About: https://t.co/tVk97zVyJD | Privacy: https://t.co/konTUUP70UTrends for United States
You might like