

krackcodeAIcops @krackcodeAI
A distinguished attorney, Director of the FBI, COO of @thenovacyberqfs national security and institutional excellence TELEGRAM https://t.co/HzheD7LjrC t.me/RRRT011 Ohio, USA Joined May 2024-
Tweets2K
-
Followers4
-
Following59
-
Likes1K
🚨 A false security alert put Foundation wallet users in the crosshairs. Attackers impersonated official emails and tried to obtain recovery phrases to steal bitcoins. What data could have been exposed?

🚨 He had saved nearly $100,000 to go study abroad… only to lose everything after connecting his crypto wallet to a fake website. A student reportedly fell victim to a "wallet drainer," believing he was accessing a legitimate exchange; he connected his wallet to a fraudulent site, allowing scammers to siphon off the funds he had set aside for his studies.


HE STOLE $947,000 IN 51 SECONDS. 4 MINUTES AFTER HIS WALLET WENT PUBLIC, HE MOVED EVERYTHING. THEN HE FROZE. AND NOW OTHER SCAMMERS ARE HUNTING HIM. this is the Bloom drain, rebuilt from 73 on-chain transactions. timestamps are UTC, and every one of them is public. > CHAPTER 1: THE KNOCK (00:59) first move: 1 lamport out of the biggest victim wallet. that's $0.0000001. he isn't stealing yet. he's checking whether the door is open. > CHAPTER 2: THE ROLL CALL (01:02) ten more wallets each send 0.001 SOL to the same address, about one every 2 seconds. a person doesn't do that. a script is checking which wallets it controls. > CHAPTER 3: THE 51 SECONDS (01:03:50 → 01:04:41) 41 wallets emptied in 51 seconds. 1,636 SOL, then 1,039, then 1,021, then 765. every drain was signed by the victim's own wallet, which paid its own fee. no brute force. no phishing link. the wallets simply said yes. > CHAPTER 4: HE CAME BACK FOR MORE (01:28) 24 minutes later he sends 0.02 SOL back into one drained wallet. why give money back? that wallet still held ~$49k in USDC, and it had no SOL left to pay fees. he tests it with 0.000001 USDC transfers. the $49k never reaches him. > CHAPTER 5: SPOTTED (04:26 → 04:30) 04:26:10: Onchain Lens posts his address. 04:30:56: all 9,408.21 SOL leaves in one transaction to a brand-new wallet. 4 minutes 46 seconds. he was watching X too. > CHAPTER 6: THE FREEZE since then that wallet hasn't moved. no bridge, no swap, no exchange. almost $1M, parked in plain sight for 10 hours and counting. > CHAPTER 7: THE SCAVENGERS this is the part nobody's talking about. lookalike wallets start showing up, copying the first and last characters of real addresses, and they send dust to the drainer so a fake shows up in his history. then they go after the hacker's new wallet with copies of his own address, hoping he pastes the wrong one when he cashes out. scammers trying to scam the scammer. > BLOOM'S SIDE Bloom: a third-party module had a remote code execution bug. no private keys leaked. 9 users, 49 wallets, 100% refund. on-chain: every drain was signed by the victims' own wallets. both can be true. if you can run code on the machine that signs, you never need the key. you just ask it to sign. by 12:41 Bloom was publicly offering to negotiate. so let's recap: • 1 lamport to knock • 10 test transfers • 41 wallets in 51 seconds • 4m46s from exposure to exit • 10+ hours frozen • a crowd of scammers waiting for him to make one copy-paste mistake he doesn't have to outsmart anyone. he just has to outwait you. we don't get bored. we're watching 6nYy…moe9.
~9,408 SOL (~$950K) was stolen from 48 unique addresses linked to @BloomTrading. According to Bloom Trading, the affected wallets belong to 9 users One address alone lost 1,636 SOL (~$165K). The median loss per address was ~100 SOL (~$10K), and the top 5 addresses account for 54% of the total losses All stolen funds were swept to 6nYyCzJJzErbmfxvXqzbAqwoBzNvXUiwr15KCkcgmoe9, where they are now lying dormant We are actively monitoring this case

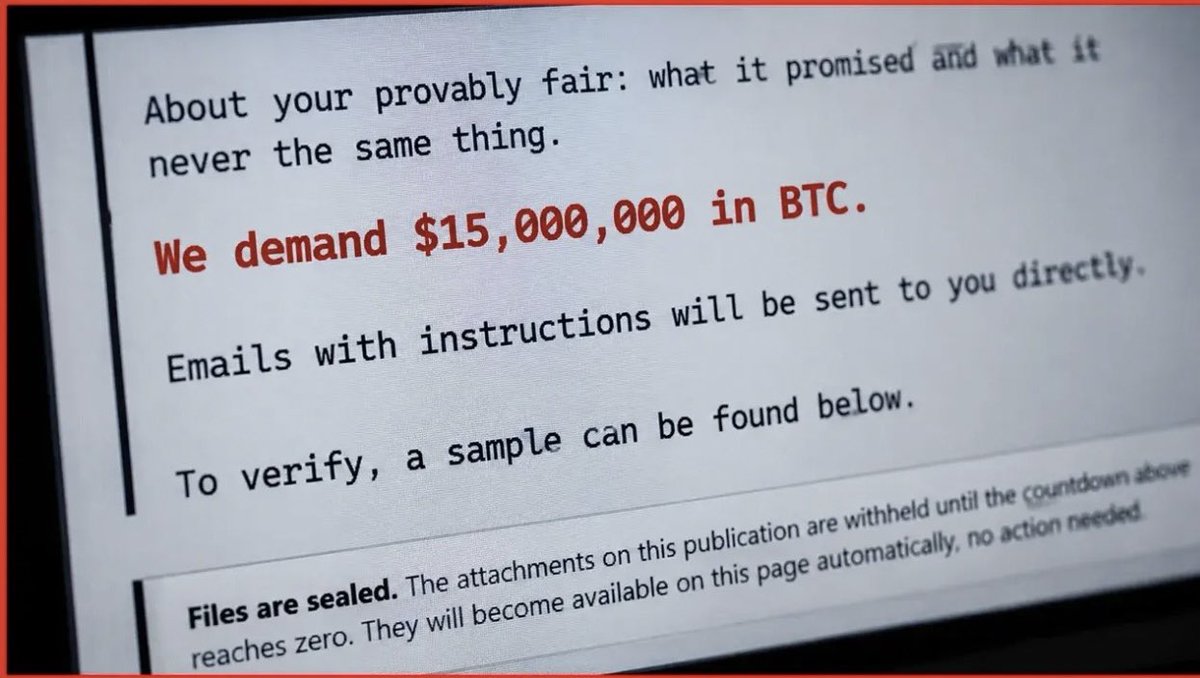
Crypto Casino Gamdom Faces $15M Bitcoin Ransom After Multimillion-Dollar Hack
WHY DID TRUMP'S CORRUPT DOJ HANG UP THE PHONE EVERY TIME WHEN I CALLED AND TRIED TO REPORT ABOUT ELECTION FRAUD AND FINANCIAL FRAUD EVERY TIME THEY HEAR ME SAY THE NAMES TRUMP MUSK PUTIN AND BIBI 🤔 I THOUGHT PEOPLE WERE SUPPOSED TO CALL THEM IF WE KNEW SOMETHING 🤔 😕
🚨 Alleged Data Leak Involving Vietnam’s Ministry of Defense A dark web post attributed to SCTH claims access to internal administrative and procurement records linked to the ministry. The allegation remains unverified. #DarkWeb #ThreatIntelligence

QUANTUM SENSING CAN INCREASE CRITICAL MINERAL DISCOVERY BY 5X. In mining, less than 1% of exploration targets ever become mines. The average discovery takes 15 years to produce metal. Drilling eats up to half of exploration budgets, and most of it hits nothing. Quantum sensors are about to change the odds. Here's the real math. The problem: most deposits have already been found. What's left sits under hundreds of meters of barren rock, where surface geology tells you nothing. Miners drill nearly blind. Quantum gravity gradiometry reads the density of rock through solid bedrock. Different ores, different densities, different gravitational signatures. The deposit's location, depth, and shape, mapped before a single drill bit spins. The receipts, show this is a real improvement for miners. Australia's LANDTEM quantum sensor already aided discoveries worth $10B+. Diamond quantum magnetometers produce 8x more map data than the industry standard, flown on drones that map sites 10x faster at half the cost. Industry reports up to 30% cut in exploration operating costs. Stack those effects and we have created an educated assumption from the math that we could see 2 to 5x more discoveries per exploration dollar. Off a sub-1% hit rate, that's not an upgrade. That's a different business. And it's moving from labs to real testing. $INFQ is field testing quantum gravity sensors in Colorado in 2027 to hunt critical minerals. Congress has a bill directing the US Geological Survey to build the tech into America's national mineral maps. Their CEO's line: "America cannot secure the supply chains it cannot see." This won't spike mining output tomorrow. Permitting and mine construction still take a decade, and sensors don't fix that. What changes is the front end, the searchable Earth gets bigger. Most undiscovered deposits sit under cover, invisible to every tool except this one. $INFQ $IONQ $USAR $CRML

TOP 35 WEEKLY FRAUD ANNOUNCEMENTS (October 19, 2026–October 23, 2026) 1. @POTUS and @VP announced historic fraud whistleblower program offering incentives for fraud tips (see America.gov/fraud). 2. Fifteen defendants charged in $1.8 billion health care fraud takedown in Los Angeles. 3. Laboratory owner charged in $66.2 million fake COVID-testing fraud scheme. 4. Nationwide SNAP crackdown announced by @VP and @AGToddBlanche targeted over $42 million in SNAP fraud schemes (enough to feed 220,000 Americans for the entire month of October). 5. Telemedicine owner sentenced to 240 months for $46.2 million Medicare fraud scheme.
According to Unchained, the Ethereum liquid staking protocol Swell has suspended deposit and withdrawal services for swETH and rswETH, pending corrections to the net asset value (NAV) and redemption rates of the two tokens before resuming. Data shows that the redemption rates reported by the swETH and rswETH contracts are approximately 1.203 ETH and 1.138 ETH, respectively, which are about 6% and 5% higher than previous normal levels, while the actual DEX transaction prices are approximately 1.089 WETH and 1.029 WETH. On-chain analyst Spreek suspects a leak of the relevant token management keys and has identified a malicious upgrade contract that could potentially affect around 2,500 ETH, though no related upgrades have been formally executed yet. Swell states that the ETH in the relevant contracts has not been transferred out, and the specific cause is still under investigation.
🇺🇸⚖️ The American justice system is demanding $1.37 billion from a couple accused of orchestrating a massive crypto Ponzi scheme… by recruiting their victims from prayer groups. Cynthia and Eddy Petion, founders of NovaTechFX, allegedly lured hundreds of thousands of investors worldwide with promises of returns ranging from 2 to 4% per week. Their strategy was particularly insidious: targeting Haitian and religious communities via WhatsApp, social media, and prayer groups to gain their trust. But the figures revealed by investigators are staggering: out of $1.16 billion in crypto deposits made between 2019 and 2023, only $26 million was actually used for trading… resulting in $18 million in losses! Meanwhile, at least $134.5 million was transferred to wallets controlled by the founders. The so-called profits paid to investors actually came from deposits by new arrivals. The couple fled the United States and has not appeared before the courts. On October 22, the New York Attorney General announced that she had secured nearly $6 million from four promoters of the scheme and is now seeking $1.37 billion from the founders. More than 11,000 New Yorkers are among the victims of these fraudulent setups.
Update your iOS promptly and beware of apps potentially compromised by #DarkSword. DarkSword targets crypto users, exploiting iOS vulnerabilities to escape the sandbox and steal sensitive data, including Keychain credentials, locally stored wallet private keys, and Notes data. Successful exploitation could put your crypto assets at risk. 🔎 According to SlowMist’s MistEye threat intelligence analysis, 1,500+ DarkSword-related phishing sites have been identified across the web, targeting users through e-commerce platforms, fake Binance and OKX sites, fake crypto wallets, gaming services, and cryptocurrency exchanges. 🛡️ Stay safe: • Keep your iOS devices updated. • Be cautious of suspicious or compromised apps. • Never store sensitive wallet credentials or seed phrases in Notes. 📖 Related SlowMist analyses: 🔗 DarkSword Trojan Backend & iOS Attack Chain: slowmist.medium.com/threat-intelli 🔗 FomoPeek App Store Poisoning & iOS Kernel Exploitation: slowmist.medium.com/threat-intelli
💥 NEW: 22 million private images scanned in the EU, Palantir's software reads the reports > Under the temporary Chat Control law, Google, Microsoft, Meta and Snap have been scanning private messages of EU citizens since 2021 > US law forces them to send every suspected tip to NCMEC, and NCMEC confirms all CyberTipline reports are run through Palantir Foundry > LinkedIn alone processed 22 million images and over 2 million videos from EU users in 2024, and just under a million of NCMEC's 2024 reports concerned the EU > The EU claims the scanning tech errs once in 50 billion images, researchers found false matches as high as one in a thousand > Not even Patrick Breyer, the law's loudest critic, knew about the Palantir link, and neither did the EU legislators interviewed
🚨 UPDATE: Railway says hackers targeted AI API keys to carry out model distillation attacks. Up to 100,000 workspaces may have been exposed. Attackers allegedly used uncensored AI models and massive compute resources to breach its infrastructure.


The OCC is committed to supporting a strong community banking sector as payment innovation advances. The effect of stablecoin adoption on community bank deposits remains uncertain, and estimates vary widely. The OCC takes community banks’ funding concerns seriously and is closely monitoring potential deposit outflows as the industry develops. OCC.gov/GENIUS

#CyberAlert | AL26-026 Critical vulnerabilities impacting PHP - CVE-2026-109618 and CVE-2026-109619 – Update 1 The PHP Security Team published additional information regarding another remote code execution vulnerability. cyber.gc.ca/en/alerts-advi…
16. Michigan defendant sentenced to 70 months for pandemic-relief fraud scheme. 17. Maryland executive indicted for seeking $7.5 million through fraudulent PPP applications. 18. Two defendants charged in $4 million Pandemic Unemployment Assistance fraud scheme. 19. Social media personality charged with stealing approximately $4 million in SNAP benefits. 20. Convicted felon sentenced to 130 months for orchestrating $3 million COVID-fraud scheme.
6. Four defendants sentenced to combined 253 months for $84 million Treasury-check theft conspiracy. 7. Maryland defendant convicted in $18.7 million Medicare respiratory-testing fraud scheme. 8. Two defendants charged in $19 million federal workers' compensation health care fraud. 9. Husband-wife fraud duo sentenced to 110 and 80 months for $14 million Medicare fraud. 10. Philippines-based U.S. citizen pleaded guilty to targeting servicemembers and veterans with identity-theft schemes.
Heads up there’s a serious security problem with PHP right now. PHP is the software behind a huge number of websites (WordPress, online stores, forums, and a lot of other stuff). Two dangerous bugs were found that could let attackers break in and run their own code on the servers. The fixes just came out today, so anyone running a website needs to update as soon as possible. Some sites are even temporarily taking parts of their service offline while they sort it out, just to be safe. If you run or help manage any websites, check with whoever handles your hosting or servers and make sure they know about this. It’s one of those “update now” situations.

“Mr. Trump said last week that he was considering using a 22,000-pound GBU-43/B Massive Ordnance Air Blast bomb, or MOAB, against Pickaxe. Officials say Mr. Trump is enamored with the weapon in part because of its nickname, Mother of All Bombs.”
nytimes.com/2026/10/21/us/… Trump planning to restart the Iran War after the elections.....my god we desperately need a D House and Senate.
怡萱 @Tokahwm
7 Followers 147 Following
Kytro (private) @KytroCryypto0
1K Followers 4K Following Crypto Trader | Memecoin Trader • My cooks https://t.co/jOJAPizw4D
Federal Reserve @federalreserve
1.6M Followers 26 Following The official Twitter channel of the Board of Governors of the Federal Reserve System. Privacy Policy: http://t.co/pbRRCfwyou
怡萱 @Tokahwm
7 Followers 147 Following
Mr W @MrW98866436164
651 Followers 51 Following
carra Maxwell @carraMaxwell
2K Followers 368 Following stage 4 kidney cancer survivor and my brother was brutally murdered chopped up with a chainsaw and thrown in a dump
Laura @Laurarvap
999 Followers 144 Following
George Conway ⚖️�... @gtconway3d
2.3M Followers 3K Following Recovering lawyer | Owned by a Pembroke Welsh Corgi | Co-founder, @TheMarquePAC | Host, Psycho Politics podcast, and contributor, @BulwarkOnline | Substacker


Fidelity Digital Asse... @DigitalAssets
92K Followers 7 Following The security, integrity, and expertise that institutions need in today’s digital asset ecosystem.
DesignDynamo @talk82765058
7 Followers 1 Following
Oluwajimidide Emmanu @OLUWAJIMIDIDE
13 Followers 5 Following

JOSH DUNLAP @JDunlap1974
448K Followers 45K Following 🇺🇲 MAYOR OF MAGADONIA 🇺🇲 ✝️ CHRISTIAN ✝️ MAGA 📣BREAKING NEWS FIRST HERE

SassyGlassy @ElizaGlass1972
406 Followers 469 Following Occasional defender of Karens - civilized society comes with a price. Eternal defender of Marthas.
Azim @Azimepli06
337 Followers 313 Following
Ava @Ava230156331909
617 Followers 13 Following We all deserve to live. We have all had way more than enough. There are scams everywhere. They took all my money. $100k crypto. Yes I’m an idiot. Be careful.
Legal Aid Department ... @allbmoremd
5K Followers 4K Following Legal aid helps victims of fraud by providing assistance in filing lawsuits against those who committed the fraud and guiding them through the legal process.
Tesla Owners Silicon ... @teslaownersSV
1.4M Followers 919 Following The most notorious Tesla club 🏎️ Tesla/SpaceX News. Taking X Takeover and Tesla Takeover across the globe.
matt Thompson @Matt_Thomp3on
1K Followers 677 Following Matt has an out the box writing style ranging from suspense, urban fiction and non-fiction/self-help
Ray Brown @Raybrown1959Ray
4K Followers 2K Following Married to Cynthia 37 years. Bears, Blackhawks, Bulls and Cubs. Proud Grandpa of Savannah, Kylie and Dylan, great grandpa of Abraham and Levi. No DM’s please.
David Tetrault @TetraultDa65058
965 Followers 175 Following
Lil NoFlo @LilNoFlo
512 Followers 452 Following Go stream my new music on all platforms show some love https://t.co/TpxEy9mQZc
Tessy Japhet @JaphetTessy
16 Followers 88 Following We are here to serve you better, we listen to ur needs and we are committed to providing u with the best service possible💃💃 Capital City Development Ltd.
Michael A. Margolis @spikemargolis
606 Followers 695 Following
Susheel Madaan @SusheelMadaan2
6 Followers 138 Following
Tbone @I3wyT
29 Followers 161 Following

martins maxb @martins_maxb
9 Followers 14 Following
Bàllz @Op1Nathaniel
54 Followers 53 Following Just a regular person, making it through the week, one coffee at a time.
Bruno @b2unos
119 Followers 786 Following Mel’s husband and Matteo’s father. | MBA in Software Engineering.

Jason Shin @shin_jason58471
375 Followers 113 Following

Novacybersecurity Inc... @thenovacyberXBT
3K Followers 1K Following leaders in Cyber defense & asset recovery, only public blockchain with privacy that works, safeguarding finances.🇺🇸 Number 1681-9437 to DM
Jayson @iamjayyson
32K Followers 2K Following

Huzzain @huzzain_def1
18K Followers 699 Following 𝗗𝗲𝗙𝗶 𝗥𝗲𝘀𝗲𝗮𝗿𝗰𝗵𝗲𝗿 • 𝗣𝗿𝗼𝘁𝗼𝗰𝗼𝗹 𝗔𝗻𝗮𝗹𝘆𝘀𝘁• Markets are stories,Liquidity writes the ending •
June Marie Slattery @JuneMarieScj75
901 Followers 2K Following I agree with Elon Musk I'm a big fan I'm a nice person with a great big heart and I'm tired of being hacked. I love to crochet drive go to the movies enjoy life
Erfan @DoctorErfan7
34 Followers 25 Following
Camila @bay01c
5K Followers 243 Following
Frank @Frank6835277910
5K Followers 472 Following
Giovanna @gioma04
7 Followers 7 Following
Web3 Finder @web3finderreza
410 Followers 784 Following 🚀 Web3 Explorer | Crypto Enthusiast 💎 📈 Trader • Airdrop Hunter • Testnet Explorer ⚡ Building, Learning & Earning in Web3 🌍 Decentralized Future Believer
Molly Abraham @mollyisonchain
3K Followers 912 Following Legal at @Coinbase. Powered by stablecoins, crypto, flying cars, and courtroom drama. Working to replace myself with AI.
PD @olatundedavids
38 Followers 527 Following Child of God,Gospel Preacher,Forex Trader. I PressPlay @PRESSPLAYPD

abodyyy @abodyyywvax
1 Followers 40 Following
fgidom @fgidom445
118 Followers 140 FollowingTrends for United States
You might like


















