

Quantum Cybersecurity & Associates @Postquantuminc
Post Quantum Expert || Leaders in cyber Defense & Assets Recovery, public, Blockchain And Financial Security x.com/messages/compo… New York Joined May 2025-
Tweets15K
-
Followers75
-
Following168
-
Likes15K
Christmas Eve 2008. Tesla closed a funding round in the final hour, days from bankruptcy. Elon Musk put in all his money & assets, borrowed from friends just to pay rent. If it missed, payroll would have bounced two days after Christmas.

Two Linux items this hour: a remote denial-of-service in rpcbind with fixes out, and 116 new unscored kernel CVEs. Nothing is known to be exploited, and CISA's list hasn't changed since the Oct 27 Brotli and Adobe Commerce entries. 1. CVE-2026-94640: rpcbind remote denial of service (CVSS 7.5) The flaw: A remote attacker with no login can flood rpcbind with many unique requests. rpcbind keeps per-request statistics in memory with no limit, so memory and CPU use keep growing until the service degrades. Fix: Update the rpcbind package. Red Hat shipped fixes, for example RHSA-2026:83561 and RHSA-2026:89197. See also the Red Hat CVE page. Mitigation: If a host doesn't need NFSv3 or NIS, disable rpcbind. In any case, block port 111 over TCP and UDP at the network edge. Detection: Watch rpcbind's memory use for steady growth, and look for large numbers of different RPC calls arriving on port 111.

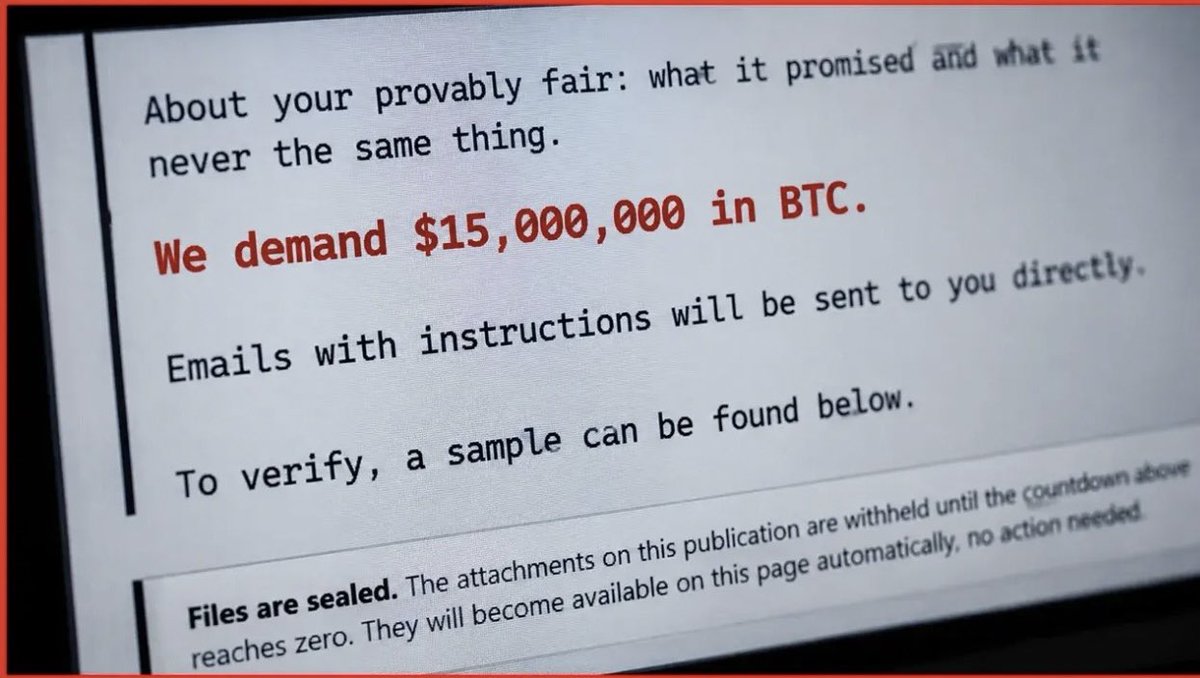
Crypto Casino Gamdom Faces $15M Bitcoin Ransom After Multimillion-Dollar Hack
🚨 Hackers are probing a critical Oracle E-Business Suite vulnerability just days after it was patched. CVE-2026-101767 (CVSS 9.8) allows unauthenticated SQL injection that can lead to remote code execution. Exploit attempts were detected on decoy systems on October 27. What we know ↓ thehackernews.com/2026/10/hacker…
2. 116 new Linux kernel CVEs (CVE-2026-99101 through CVE-2026-99216), none scored yet These are fixes already merged into the stable kernel branches. The ones most likely to be rated high: CVE-2026-99128: a remote SCTP peer can send a zero-length chunk that locks up the receive path. This only applies when SCTP-AUTH covers ASCONF. CVE-2026-99110: a heap overflow in the SMB client when setting a POSIX ACL (cifs_do_set_acl). CVE-2026-99138 and CVE-2026-99139: local use-after-free bugs in TCP getsockopt, triggered when a BPF program supplies the congestion control. Also worth noting: an SELinux BPF token permission race (CVE-2026-99129), several KVM fixes, a use-after-free in net/sched tcf_action, plus vsock, ksmbd and ntfs fixes. Apply your distro's next kernel update once it includes these fixes. Until then: SCTP: Block the module where you don't use it, with install sctp /bin/false in modprobe.d. BPF: Limit unprivileged use with kernel.unprivileged_bpf_disabled=1. Detection: Watch dmesg and journald for KASAN, oops or "soft lockup" messages, and alert on unexpected sctp module loads. The rest of this hour's new records were third-party products rather than core Windows or Linux. They include Dell PowerProtect Data Domain (CVE-2026-103780, up to 9.8), Acronis Cyber Protect (7.1 to 7.4) and a Norton, Avast and AVG Data Shredder privilege escalation on Windows (CVE-2026-6064, 7.3, fixed in 26.5.10933).

Case update from @FBIElPaso: Timothy France Johnson was sentenced to 51 months in federal prison along with a money judgement of $3,148,094.48 for running an 11-year Ponzi scheme in which he represented to investors that he would use their funds to promote NBA preseason games. Read more: justice.gov/usao-wdtx/pr/e…

🚨 Skyw4lker phishing campaign targets U.S. firms using Microsoft 365 device code phishing. No password theft required. Attackers use fake business documents and Google Sites to trick victims into authorizing access to their Microsoft 365 accounts. How the attack works ↓ thehackernews.com/2026/10/americ…

Wallet Potentially Linked to $40M UXLINK Hack Shows $6.54M in Unrealized ETH Gains A wallet suspected of belonging to the hacker behind last year’s roughly $40 million UXLINK theft holds a 30,282 ETH long on Hyperliquid, according to on-chain data. The position has an average entry price of $2,134.45 and is worth approximately $71.17 million, with $6.54 million in unrealized gains. A funding address associated with the position and a known UXLINK hacker address both transferred ETH held for gas fees to the same wallet on the same day. The trader began trading ETH on Hyperliquid in early August after consolidating roughly 11.55 million USDC from multiple sources, with five of six trades showing a profit.

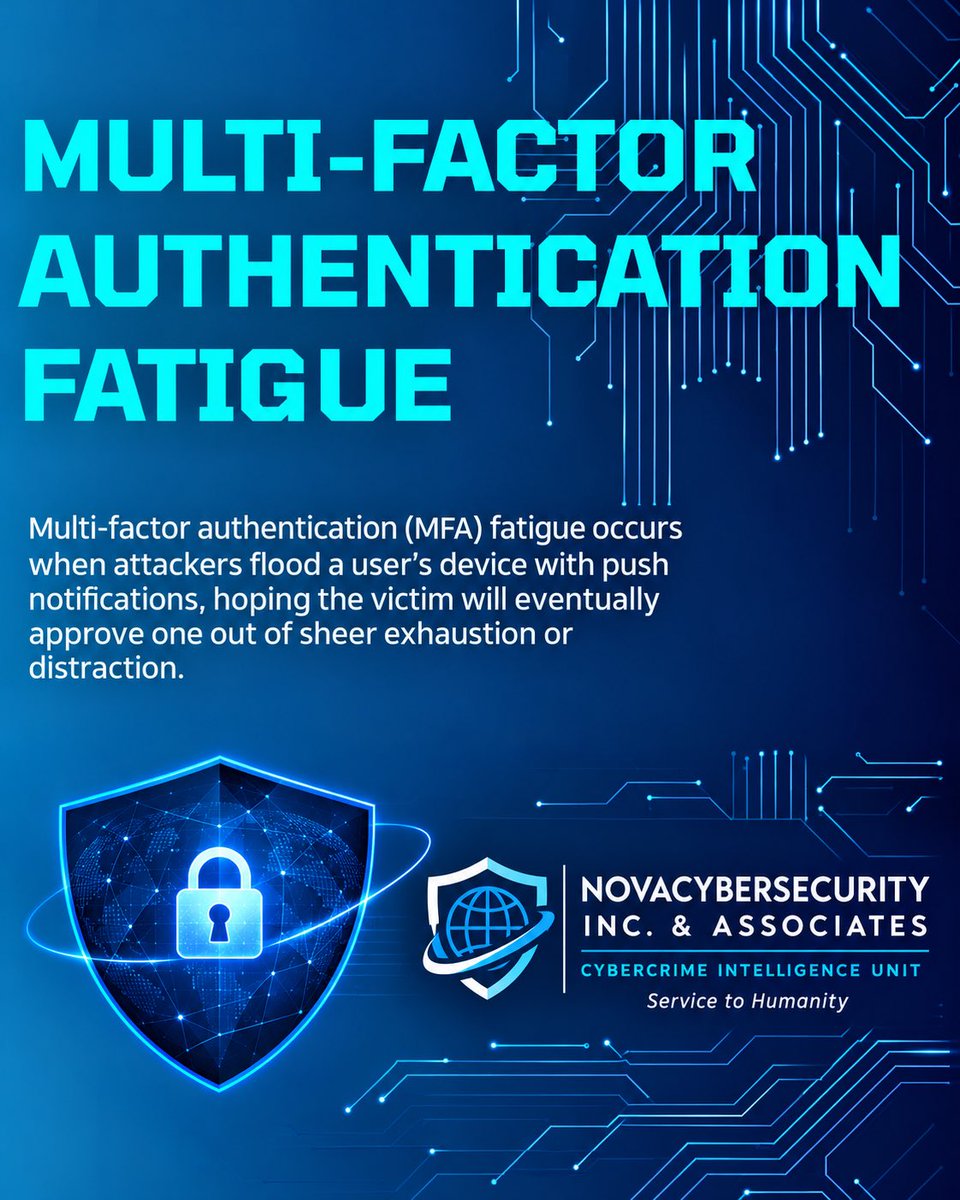
Received a sudden flood of MFA login prompts on your phone? That’s MFA Fatigue, and it’s a trap. Scammers spam your device hoping you’ll tap "Approve" just to stop the buzzing. Deny the request and change your password. #NovacybersecurityInc #SecuringTheNext250 #CybersecurityAwarenessMonth
⚠️ Fake login pages aren't just stealing passwords anymore. AI makes phishing pages easier to clone and personalize. Some attacks go further, stealing MFA codes or hijacking authenticated sessions to access corporate accounts. How these attacks work and what stops them ↓

⚠️ A Gemini agent in a security test reportedly accessed 3 real companies, one by guessing a password. Anthropic says a fake “discounted Claude” reseller stole buyers’ credentials. Same weak point: a credential someone can guess, find, or steal.


Japan's cyberattacks are forcing companies to compensate customers. 🇯🇵 GMO Internet says intruders accessed its foreign-exchange trading service. It will cover customer losses, plus pay every customer five thousand yen, around 32 dollars. Then came an extortion demand, threatening to expose company and customer data. GMO refused. Park24 separately offered three thousand yen to eligible users after its car-sharing data breach. By October twentieth, Japan logged 723 cyber incidents, exceeding either of the previous two full years.

The Dangote Refinery IPO closes today, and it has reportedly already hit its target. Bloomberg says domestic and retail investors alone have committed $1.5 billion to $1.6 billion. Applications came from 119 countries, including all 54 African countries. Think about that for a second. The same Nigerians people say don’t trust the stock market may have funded Africa’s biggest IPO almost by themselves. Demand could be so strong that some international investors get squeezed out, and Dangote may sell part of his own stake to those who miss out. The money will go towards expanding the refinery to 1.4 million barrels a day by 2029.
HE STOLE $947,000 IN 51 SECONDS. 4 MINUTES AFTER HIS WALLET WENT PUBLIC, HE MOVED EVERYTHING. THEN HE FROZE. AND NOW OTHER SCAMMERS ARE HUNTING HIM. this is the Bloom drain, rebuilt from 73 on-chain transactions. timestamps are UTC, and every one of them is public. > CHAPTER 1: THE KNOCK (00:59) first move: 1 lamport out of the biggest victim wallet. that's $0.0000001. he isn't stealing yet. he's checking whether the door is open. > CHAPTER 2: THE ROLL CALL (01:02) ten more wallets each send 0.001 SOL to the same address, about one every 2 seconds. a person doesn't do that. a script is checking which wallets it controls. > CHAPTER 3: THE 51 SECONDS (01:03:50 → 01:04:41) 41 wallets emptied in 51 seconds. 1,636 SOL, then 1,039, then 1,021, then 765. every drain was signed by the victim's own wallet, which paid its own fee. no brute force. no phishing link. the wallets simply said yes. > CHAPTER 4: HE CAME BACK FOR MORE (01:28) 24 minutes later he sends 0.02 SOL back into one drained wallet. why give money back? that wallet still held ~$49k in USDC, and it had no SOL left to pay fees. he tests it with 0.000001 USDC transfers. the $49k never reaches him. > CHAPTER 5: SPOTTED (04:26 → 04:30) 04:26:10: Onchain Lens posts his address. 04:30:56: all 9,408.21 SOL leaves in one transaction to a brand-new wallet. 4 minutes 46 seconds. he was watching X too. > CHAPTER 6: THE FREEZE since then that wallet hasn't moved. no bridge, no swap, no exchange. almost $1M, parked in plain sight for 10 hours and counting. > CHAPTER 7: THE SCAVENGERS this is the part nobody's talking about. lookalike wallets start showing up, copying the first and last characters of real addresses, and they send dust to the drainer so a fake shows up in his history. then they go after the hacker's new wallet with copies of his own address, hoping he pastes the wrong one when he cashes out. scammers trying to scam the scammer. > BLOOM'S SIDE Bloom: a third-party module had a remote code execution bug. no private keys leaked. 9 users, 49 wallets, 100% refund. on-chain: every drain was signed by the victims' own wallets. both can be true. if you can run code on the machine that signs, you never need the key. you just ask it to sign. by 12:41 Bloom was publicly offering to negotiate. so let's recap: • 1 lamport to knock • 10 test transfers • 41 wallets in 51 seconds • 4m46s from exposure to exit • 10+ hours frozen • a crowd of scammers waiting for him to make one copy-paste mistake he doesn't have to outsmart anyone. he just has to outwait you. we don't get bored. we're watching 6nYy…moe9.
🇺🇸 NEW: The US DOJ is appealing a federal judge’s ruling that lifted the government’s ban on agencies using Anthropic’s AI, escalating the fight over the Pentagon’s supply-chain risk label on the company, per Bloomberg.


Ethereum Delays Glamsterdam Hoodi Fork Over EIP-8037 and EIP-8038 Risks Ethereum researcher Toni Wahrstätter said the planned Glamsterdam fork on the Hoodi testnet has been delayed after ChainSecurity identified compatibility risks in EIP-8037 and EIP-8038. The gas changes could break contracts that assume gas usage only decreases or cause failed sub-calls to behave unexpectedly. ChainSecurity has found 13 real-world cases, and developers are reviewing whether the upgrade specification needs changes.
⚠️ Fake login pages aren't just stealing passwords anymore. AI makes phishing pages easier to clone and personalize. Some attacks go further, stealing MFA codes or hijacking authenticated sessions to access corporate accounts. How these attacks work and what stops them ↓ thehackernews.com/2026/10/ai-gen…

Strive Adds 6,182 BTC as Holdings Reach 43,000, Opens $1B SATS ATM According to SEC filings, Strive purchased 6,182 BTC between October 17 and 23 at an average price of about $82,732, bringing total holdings to 43,000 BTC. The company also entered into an at-the-market program to sell up to $1 billion of its SATS perpetual preferred stock, with proceeds potentially used for additional Bitcoin purchases, working capital, income-generating investments and share repurchases.

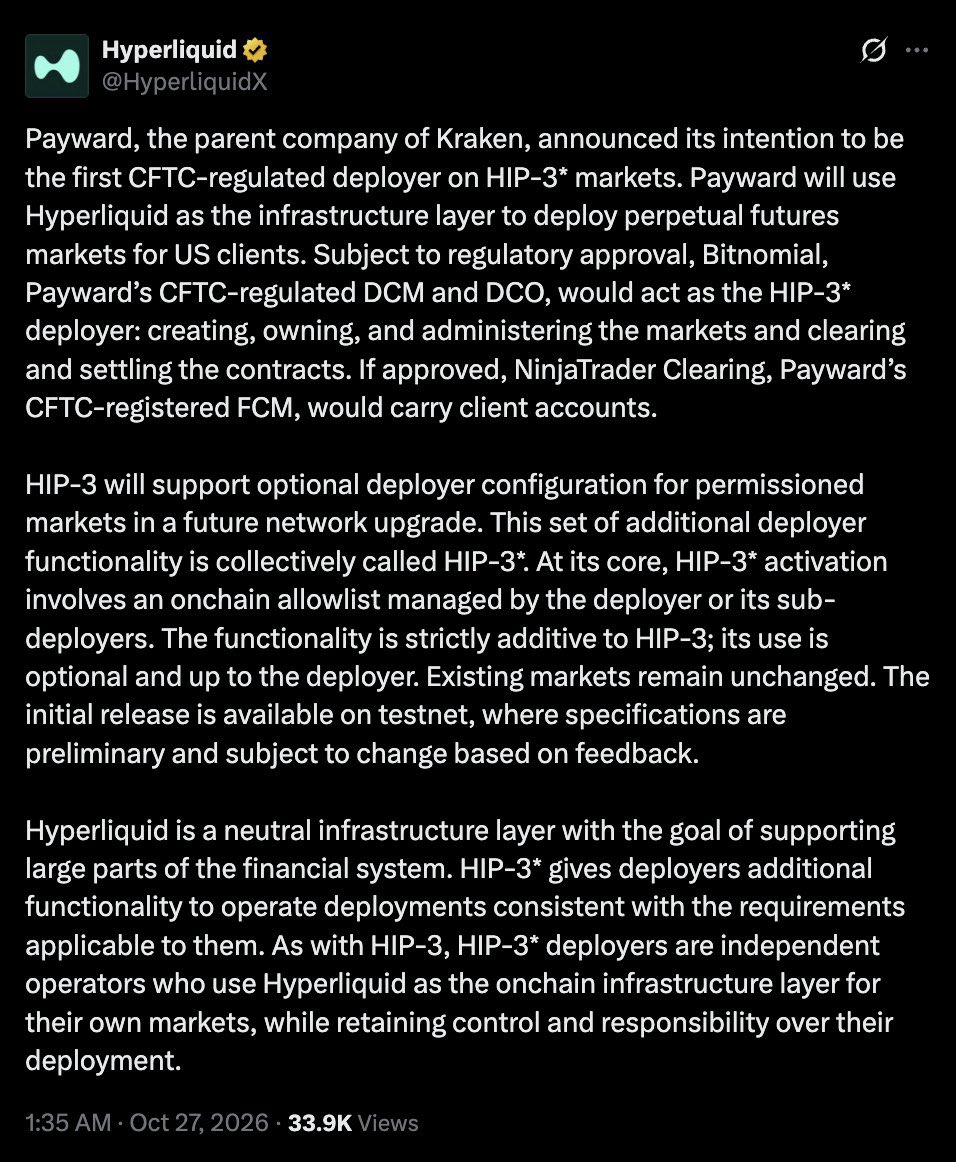
Hyperliquid: Kraken Parent Payward Plans to Become First CFTC-Regulated HIP-3* Deployer Hyperliquid announced that Kraken parent Payward plans to become the first CFTC-regulated HIP-3* deployer, using Hyperliquid infrastructure to offer perpetual futures markets to U.S. clients. Subject to regulatory approval, Payward's CFTC-regulated DCM and DCO, Bitnomial, would serve as the deployer, managing the markets and clearing and settling contracts, while its CFTC-registered FCM, NinjaTrader Clearing, would carry client accounts. HIP-3* will introduce optional onchain allowlists for permissioned markets without affecting existing HIP-3 markets. The initial version is available on testnet, with specifications subject to change.
🚨 Microsoft Teams IT support scams are leading to malware and ransomware attacks. Researchers tracked hundreds of cases where attackers flood inboxes with emails, impersonate IT staff on Teams, and trick employees into granting remote access. How the attacks work ↓


Srini Katta @srinikatta
1K Followers 1K Following Founder & CEO @QubitGuard | Post-Quantum Cybersecurity | 3 U.S. Patents | Building the security layer for the quantum era
Sandra james @Sandrajame3gss
72 Followers 202 Following
Grace @draayl
108 Followers 232 Following Travel diary: What did I eat today, where will I go tomorrow? ✈️
iblv @iblv4wku
59 Followers 3K Following

CYBER ONLINE FRAUD AG... @Paulette4Lomba
1K Followers 74 Following Advancing cybersecurity awareness and digital protection. Helping individuals recognize online threats, report fraud, and strengthen their digital security.
Jestmore Wabomba @JestmoreWa10645
0 Followers 37 Following

Trisha Hutchinson @TrishaHutc33273
292 Followers 6K Following
Emily Carter @EmilyCarterq
1K Followers 217 Following 1A advocate 🇺🇸. My post and replies are Not financial advice - I’m a trader, working with @Tesla
Mars & Machines @mars__ceo
67 Followers 390 Following

The Q Awakening @TheQAwakenlmqk
28 Followers 716 Following IT'S ONE BIG CLUB AND WE'RE ALL IN IT TOGETHER.

Foster The Future Inc... @afosterfuture
86 Followers 4K Following The Official Account of FOSTER THE FUTURE INC. Registered ® We reserve the intellectual property rights to this word.
Elena Mitchell @ElenaMitch6e
352 Followers 4K Following Elon Musk supporter 🚀 | Tesla & SpaceX enthusiast ⚡ | AI, innovation & future technology | Always exploring what’s next 🌎
Eleanor @_Eleanor_0
784 Followers 3K Following
Lee Brice @LeeBrice1rei
15 Followers 692 Following New album Sunriser out 10.2 "Dogs are Barking" out now.
Clara @uzJLEbKQIKOAq
550 Followers 638 Following Documenting my journeys through deep forests and rich flavors. Nature is my sanctuary; cooking is my art


Jessica Aurora Rocket... @JJRe3vRocket_X1
143 Followers 7K Following SpaceX-Vice President, Customer Operations and Integration. #SPACEX #TESLA #MAGA 🇺🇸
GREENPIPS @GREENPIPSfsjq
28 Followers 222 Following
Mila Everly @Jam_iaf
423 Followers 265 Following Coffee lover ☕ | Weekend hiking & city walks | Learning something new every day. I enjoy exploring new places, reading about technology, and following the futur
Sienna Calloway @Bh_wvz
380 Followers 272 Following Pilates, snapping photos, and loving life. Always down to talk crypto, blockchain, and how tech is changing money.

Froggie | Official Su... @froggie_bsc0_
378 Followers 5K Following He screamed, you screamed, we all screamed for... Froggie!🐸 ca: Oxa45f5eb48cecd034751651aeeda6271bd5df8888 https://t.co/eTDEHH5OSZ
Crypto Mafia @Cryptomafia311
179 Followers 7K Following

Crypto Mafia @Cryptomafia508
151 Followers 7K Following
H.E. Justin Sun 🌞�... @HEJustinSuntron
258 Followers 3K Following Entrepreneur | Diplomat |👩🚀 Astronaut #7121 Art Collector | Founder @trondaol Advisor @BitTorrent &@htx_global |Chinese @sunyuchentron👩🚀
John F. Kennedy Jr Q @John_Fkenned
128 Followers 2K Following F. Kennedy Jr Q Get verified @Real_JFK_Ja Dedicated to the Betterment of the World. John F. Kennedy Jr. Son of a President. Living bridge between... Show more
STEVE POPE 🇺🇸 @STEVEPOPErx
1K Followers 2K Following C.E.O @thenovacyberqfs and founder of the Blockchain Reclaim Foundation https://t.co/76GZzNjCbO
BITCOIN ETHEREUM @Bitcoinsol22
175 Followers 5K Following Bitcoin new insight, and commentary NAF✈️💌💸 Twitter...BTC SOl USDT etc

BITCOIN BTC @Bitcoinbtc46
258 Followers 5K Following Bitcoin is open source of censorship -resistant peer-peer immutable network trackable digital gold


Amelia Smith @AmeliaSmitjtor
140 Followers 17 Following Founder ✨ NewArk Advertising and Marketing | 50M+ views Bridging UGC Creators with Brands. Scroll-Stopping Content That Converts
Bun @kc295838295
6 Followers 24 Following
BLOCKCHAIN TECHNOLOGY @Blockchainasso
77 Followers 201 Following knowledgeable, and relentless when it comes to protecting our clients. I couldn’t have asked for better representation.
Niki Patel @nikipatelll_
12 Followers 174 Following
Alex Cong @Cong5288
2 Followers 97 Following iOS security enthusiast | Currently learning and debugging exploit chains like DarkSword Grateful for any guidance from experienced researchers
Crypto pu @dhrlvydk
444 Followers 7K Following

Maverick @CryptoSant53718
309 Followers 5K Following
Joseph Montalvo @JosephMont65827
18 Followers 37 Following
Shannon @Shannon0mq0
29 Followers 11 Following
CYBER ONLINE FRAUD AG... @Paulette4Lomba
1K Followers 74 Following Advancing cybersecurity awareness and digital protection. Helping individuals recognize online threats, report fraud, and strengthen their digital security.
Frank @Frank68158859
3K Followers 298 Following
Emily Carter @EmilyCarterq
1K Followers 217 Following 1A advocate 🇺🇸. My post and replies are Not financial advice - I’m a trader, working with @Tesla
The New York Times @nytimes
53.9M Followers 847 Following We seek the truth and help people understand the world. All election coverage is free in our app. https://t.co/e2FWJZP3Nb
House Republicans @HouseGOP
1.8M Followers 672 Following We are the Republican Conference in the United States House of Representatives 🇺🇸 Led by Chairwoman @RepLisaMcClain
Senate Republicans @SenateGOP
1.7M Followers 148 Following Updates from Senate Republicans and the Senate Republican Conference, led by @SenTomCotton.
X Open Source @XOpenSource
48K Followers 0 Following
Anderson Cooper 360° @AC360
1.5M Followers 154 Following A behind the scenes look at Anderson Cooper 360°. Watch AC360° M-F at 8pm/ET on @CNN and follow Anderson on twitter: @AndersonCooper.

Aayush pandey @Aayushpand96538
12 Followers 19 Following
Dark Web Informer @DarkWebInformer
252K Followers 97 Following One guy. Global cybercrime. Tracked so you don't have to. Ransomware, data breaches, dark web activity, darknet markets, IOCs & emerging threats. Stay informed!
Lex Wheeler @LexWheelerd7ud
18 Followers 37 Following Squawk Box Analyst | Investor | Proud Dad awesome 😎
U.S. Marines @USMC
1.8M Followers 296 Following The official Twitter account of the United States Marine Corps. The appearance of links does not constitute endorsement.
The Joint Staff 🇺�... @thejointstaff
448K Followers 299 Following Official Twitter account for the Joint Staff, the Chairman of the Joint Chiefs of Staff, and the Vice Chairman. Follows, RTs, links, and likes ≠ endorsement.
Secretary Marco Rubio @SecRubio
2.2M Followers 18 Following 72nd Secretary of State serving under the leadership of @POTUS Trump.
IRSnews @IRSnews
319K Followers 8 Following Helping you understand and meet your tax responsibilities. IRS doesn't collect comments on this site. Privacy Policy: https://t.co/pEkPKwvDQs
DOGE IRS @DOGE_IRS
70K Followers 1 Following
IRS Tax Pros @IRStaxpros
139K Followers 6 Following IRS news and guidance for tax professionals. IRS does not collect comments or messages on this site. Please see our privacy policy at https://t.co/zvKJvKFC1w
IRS Criminal Investig... @IRS_CI
21K Followers 395 Following IRS Criminal Investigation does not collect comments or messages on this site. Report fraud: https://t.co/pbByqy4blp. Privacy policy: https://t.co/zeAJuxI6AJ
U.S. Navy @USNavy
2.0M Followers 1K Following Official X account of the #USNavy. (Following, reposts and links ≠ endorsement)
U.S. Department of Ju... @TheJusticeDept
2.4M Followers 196 Following Official account of the Justice Department 🇺🇸 DOJ Privacy Policy: https://t.co/2J3w9HbAuR
Department of State @StateDept
6.8M Followers 410 Following Leading U.S. foreign policy and American diplomacy since 1789. For all Department accounts: https://t.co/VpbtF1M8HK
The U.S. Capitol Poli... @CapitolPolice
104K Followers 73 Following Defending Congress, the U.S. Capitol, and democracy since 1828.
U.S. Army Europe and ... @USArmyEURAF
382K Followers 60 Following The official X page of U.S. Army Europe and Africa (Following, RTs and links ≠ endorsement)
FBI Washington Field @FBIWFO
284K Followers 131 Following Official FBI Washington Field X. Submit tips at https://t.co/NGk6gzdQ6H. Public info may be used for authorized purposes: https://t.co/yr6QTJ0VnO.
U.S. Air Force @usairforce
1.8M Followers 627 Following Official U.S. Air Force X: The appearance of hyperlinks does not = endorsement. Comment moderation & endorsement disclaimer: https://t.co/ueEIVwJZNh
U.S. Pacific Command @USPACOM
455K Followers 3K Following Official account of the U.S. Pacific Command, America’s oldest & largest Combatant Command. Following, RTs & likes ≠ endorsement.
U.S. Central Command @CENTCOM
1.8M Followers 121 Following The official account of U.S. Central Command.
FBI @FBI
4.0M Followers 2K Following Official FBI X account. Submit tips at https://t.co/tGqFRcJykB. Public info may be used for authorized purposes: https://t.co/x6bfDUEYeJ.
Trump Accounts @TrumpAccounts
51K Followers 5 Following Introducing Trump Accounts. A stronger financial future for every child. Safe, steady growth. Questions: @AskTrumpAccts Inquiries: [email protected]
Treasury Secretary Sc... @SecScottBessent
1.0M Followers 25 Following 79th United States Secretary of the Treasury
Bun @kc295838295
6 Followers 24 Following
vitalik.eth @VitalikButerin
8.0M Followers 551 Following I choose balance. First-level balance. mi pinxe lo crino tcati https://t.co/gCQrmCby7P
STEVE POPE 🇺🇸 @STEVEPOPErx
1K Followers 2K Following C.E.O @thenovacyberqfs and founder of the Blockchain Reclaim Foundation https://t.co/76GZzNjCbO
kenny ,The Hillbilly ... @kenbrown383
619 Followers 227 Following Space Science , Aerospace Engineer, Electrical and Mechanical Engineer .
이용이 @iyongi11
2 Followers 5 Following

이용기 @iyonggi12135645
11 Followers 62 Following
Miami PD @MiamiPD
77K Followers 1K Following Miami Police Dept. |We are on FB, Ig, Nextdoor, YouTube, and TikTok | Account NOT monitored 24/7 | For Emergencies call 911 | Terms of Use: https://t.co/1O1bfjjV5B
Coinbase Markets 🛡... @CoinbaseMarkets
1.5M Followers 17 Following Building the Everything Exchange. For support: @CoinbaseSupport.
BNB Chain @BNBCHAIN
3.9M Followers 569 Following The blockchain with superior distribution and deep liquidity, built for global markets and the next billion users. Build your AI agent with BNB Agent Studio 👇
Blockchain @blockchain
1.3M Followers 97 Following We provide the services powering a new financial world. Got a support request? Get in touch here: https://t.co/KP2llTumhE
Dogecoin @dogecoin
4.4M Followers 44 Following Dogecoin is an open source peer-to-peer cryptocurrency, favored by shibas worldwide. Elon Musk thinks we're pretty cool. RTs are not endorsements.Trends for United States
You might like


















